

Ransomware victim disclosure
← All victimseTeam Inc.
Claimed by EndZone · listed 2 hours ago
Status timeline
- ListedSep 24, 2026
- Data leakeddate unknown
At a glance
- Group
- EndZone
- Status
- Data leaked
- Country
- United States
- Listed on leak site
- Sep 24, 2026
- Records
- 15000
About the victim
AI dossier — public-source company profileeTeam Inc. is a privately held global workforce solutions and business transformation company founded in 1999 by Ben Thakur. Certified as a Minority Business Enterprise (MBE), it has grown from a boutique IT staffing agency into a large global network managing thousands of internal employees and contract workers across multiple continents.
- Industry
- Staffing & Workforce Solutions
- Employees
- 15000
- Founded
- 1999
Attack summary
Severity: critical — Confirmed exfiltration of highly sensitive PII (SSNs, DOBs, home addresses, phone numbers) for 15,000 employees at scale, exposing individuals to identity theft and fraud risk.EndZone claims to have exfiltrated all 15,000 employee records from eTeam Inc., including personal identifiable information (PII) such as full names, email addresses, home addresses, dates of birth, Social Security numbers, phone numbers, employment contracts, manager information, hire dates, and salary data. The group states it previously engaged with eTeam privately and is now publishing the data as leverage.
Data the group says was taken
AI dossier — extracted from the leak post- employee names
- email addresses
- home addresses
- dates of birth
- Social Security numbers
- phone numbers
- employment contracts
- manager information
- hire dates
- salaries
- employment status records
- tax/payroll identifiers
What the group claims
eTeam Inc. is a privately held global workforce solutions and business transformation company. Founded in 1999 by Ben Thakur, certified as a Minority Business Enterprise (MBE). Grew from a boutique IT staffing agency into a global network managing thousands of employees and contract workers across continents.
The leak post
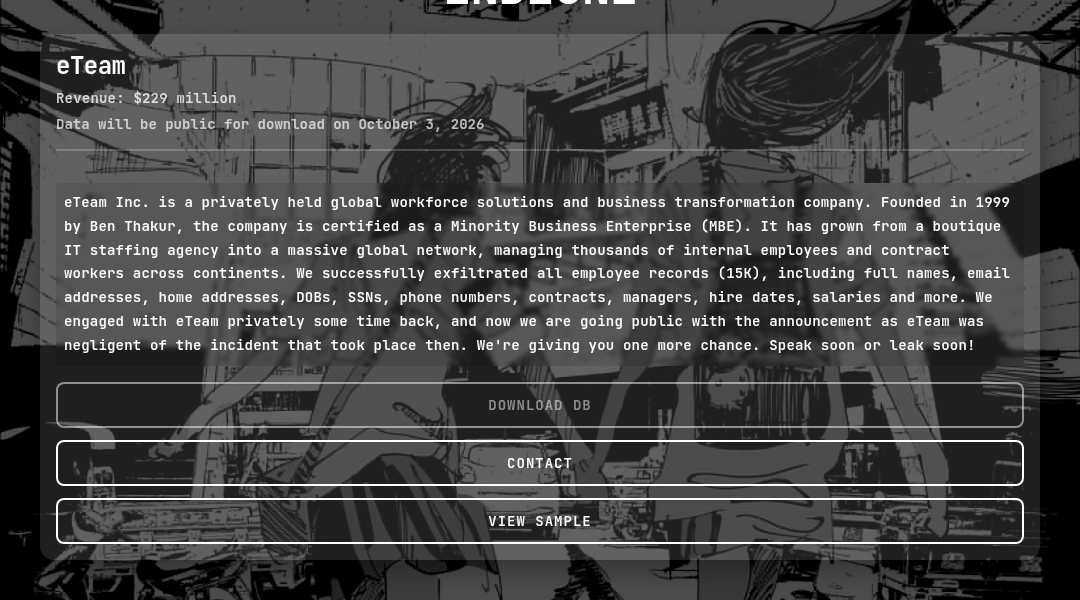
captured from the group's siteData will be public for download on October 3, 2026 eTeam Inc. is a privately held global workforce solutions and business transformation company. Founded in 1999 by Ben Thakur, the company is certified as a Minority Business Enterprise (MBE). It has grown from a boutique IT staffing agency into a massive global network, managing thousands of internal employees and contract workers across continents. We successfully exfiltrated all employee records (15K), including full names, email addresses, home addresses, DOBs, SSNs, phone numbers, contracts, managers, hire dates, salaries and more. We engaged with eTeam privately some time back, and now we are going public with the announcement as eTeam was negligent of the incident that took place then. We're giving you one more chance. Speak soon or leak soon! ### Sample Records | View image proof at the bottom ``` 637-88-2141,Adolfo,,Aguirre,,,"Aguirre, Adolfo",Adolfo Aguirre,M,,09/23/2003,22,,,,,,,,,,,Consultants,NJ,,$25-$29.99,,,,,,Technology Consulting Analyst,,,,,,,,eTeam,,,,,Terminated,,06/03/2024,,,07/16/2024,No,,08/31/2024,Involuntary Termination,08/14/2024,,,,,,,,,,,,Eligible (Regularly works more than 30 hours a week),No,No,No,,,…
Data the group says was taken
- employee records
- full names
- email addresses
- home addresses
- dates of birth
- SSNs
- phone numbers
- contracts
- manager information
- hire dates
- salaries
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.