

Ransomware victim disclosure
← All victimsCamellia Line
Claimed by N0n · listed 4 hours ago
Status timeline
- ListedOct 13, 2026
- Data leakeddate unknown
At a glance
- Group
- N0n
- Status
- Data leaked
- Country
- Japan
- Sector
- Ferry / RoRo shipping
- Listed on leak site
- Oct 13, 2026
- Data size
- 108 GB
- Records
- 181420 files
About the victim
AI dossier — public-source company profileCamellia Line is a ferry and RoRo (roll-on/roll-off) shipping operator. No public website or detailed operational information is available; the victim name appears in a ransomware leak post alongside multiple port and terminal operators.
- Industry
- Ferry & RoRo Shipping
Attack summary
Severity: medium — Confirmed exfiltration claimed (108 GB total data across the leak post); however, no specific proof files, screenshots, or granular data inventory are published for Camellia Line. Data involves operational/maritime records rather than regulated PII at scale.The N0n group claims to have encrypted Camellia Line's networks and exfiltrated operational data. The group lists the victim in a multi-victim extortion post but does not detail specific data categories or proof files attributed to Camellia Line itself.
What the group claims
Ferry and RoRo shipping operations
The leak post
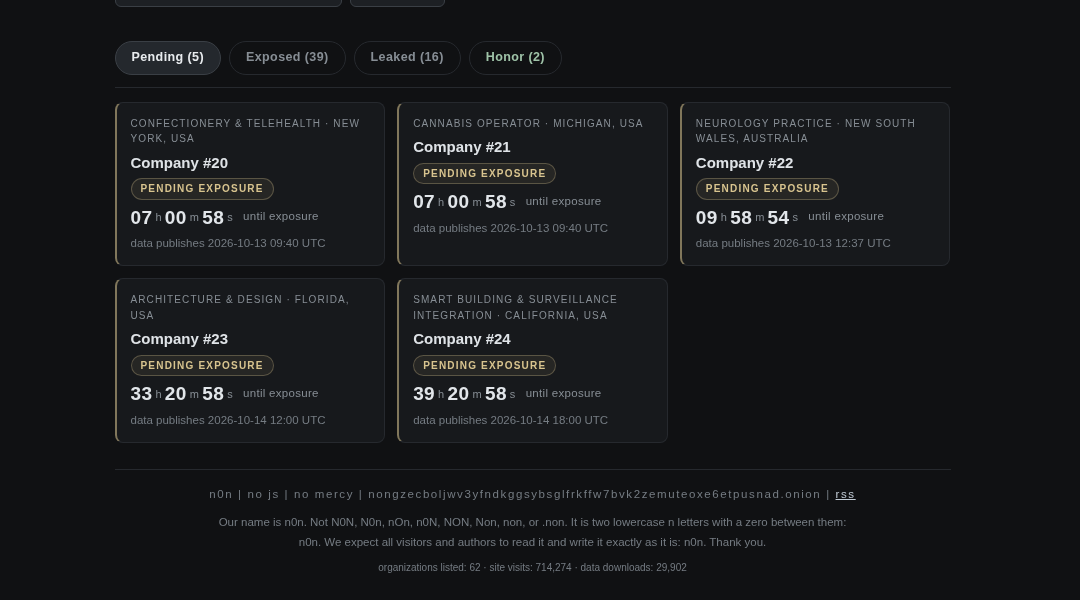
captured from the group's site# Your data has a deadline. Organizations below lost control of their networks. When the countdown ends without payment, their data becomes public. Those who honored their deadline are remembered with respect. Victim representatives: use the personal key from your ransom note to reach your negotiation room. ### Pusan Newport Company (container terminal operations) Port terminal operations · South Korea #### What will be published if no settlement is reached * Terminal operating system deployment and configuration records and operational container documentation 12,000,000 USD (approx. 114 BTC) pay exactly to this bitcoin address payment is verified automatically on the bitcoin network. your data is destroyed and this page is removed the moment the full amount arrives. no registration, no contact, no negotiation. one-time option: pay 10% of the settlement amount (12,000,000 USD (approx. 114 BTC)) to the same address in ONE transaction — the exact entry amount is 11.4 BTC (~USD 1,200,000). Then claim your private negotiation room with your transaction ID. the room key is revealed only to the claimant, never on this page. this can be done only once. ### ILCS Pelindo (port logistics…
Data the group says was taken
- Freight settlement and payment records
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.