

Ransomware victim disclosure
← All victimsUnknown County/Healthcare Entity
Claimed by Rhysida · listed 3 hours ago
Status timeline
- ListedOct 9, 2026
Current state: Listed for ransom
At a glance
- Group
- Rhysida
- Status
- Listed for ransom
- Country
- United States
- Sector
- Government/Healthcare
- Listed on leak site
- Oct 9, 2026
- Data size
- 2.6 TB
- Records
- 814500 files
About the victim
AI dossier — public-source company profileUnknown County or Healthcare Entity in the United States. Based on the disclosed data, the organization appears to be a county-level government agency or healthcare system managing public health, social services, and detention operations.
- Industry
- Government/Healthcare
Attack summary
Severity: critical — Confirmed exfiltration of highly regulated healthcare data (methadone clinic records under 42 CFR Part 2), personally identifiable information at massive scale (SSNs, medical diagnoses, government IDs for tens of thousands of individuals), and sensitive government operational records. Multiple protected classes of data and breach of federal confidentiality regulations.Rhysida claims to have exfiltrated 2.6 TB of data including medical records (particularly from a methadone clinic subject to strict 42 CFR Part 2 confidentiality rules), background-check dossiers with SSNs, county payroll and HR records, jail gang-intelligence files, and personal documents of thousands of individuals and county employees.
Data the group says was taken
AI dossier — extracted from the leak post- Medical records with patient names and diagnoses (2022-2026)
- Methadone clinic records (42 CFR Part 2 protected)
- Background-check dossiers with SSNs
- Medical-assistance files with driver licenses, Green Cards, SSN cards
- County payroll registers and salary records
- HR memos, contracts, pension and discipline databases
- Jail gang-intelligence files
- Tax forms and banking data
What the group claims
County-level entity with medical and law enforcement records including methadone clinic records, background checks, medical faxes, and jail gang-intelligence files.
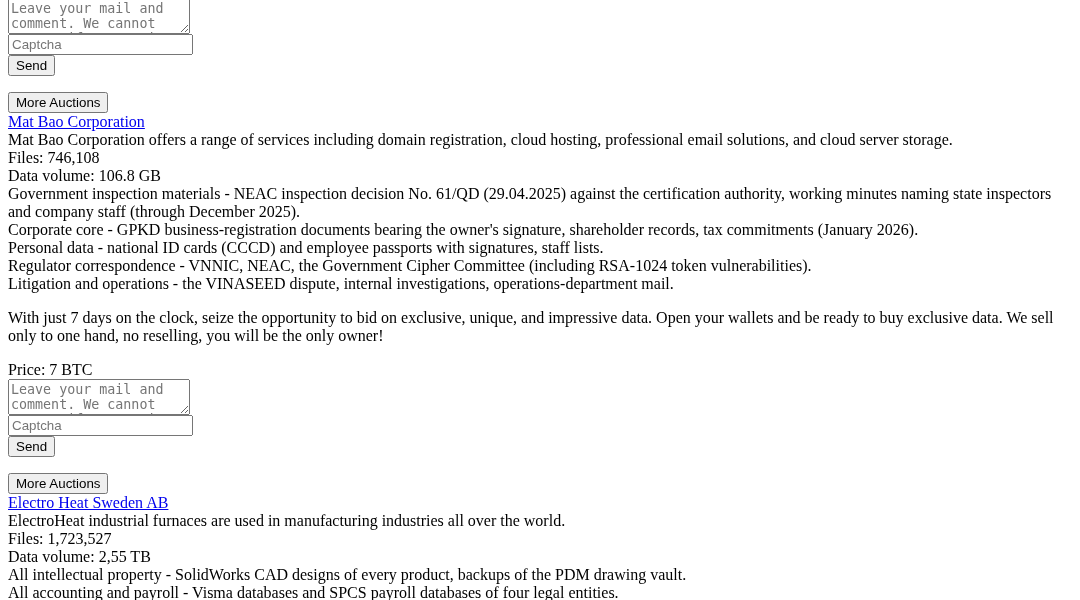
The leak post
captured from the group's siteSKAFF is a leader in Lebanon in the field of decorative fabrics. Files: 139,377Data volume: ~268 GB**Full HR dossiers - ~40 scans of Lebanese national ID cards (both sides + photos), a director's passport, civil-status extracts.Banking data - employee account files at Byblos Bank (named per person), Cedrus Bank corporate card program with banker contacts, account statements.Payroll violations - unpaid-salary analysis file, payroll module source code, staff leave requests.Employees' private lives - family photo archives on the work server.Commerce � price lists, Four Seasons and Les Galeries proposals, customs/export documents (Dubai, Erbil), customer claims. With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! Mat Bao Corporation offers a range of services including domain registration, cloud hosting, professional email solutions, and cloud server storage. Files: 746,108Data volume: 106.8 GBGovernment inspection materials - NEAC inspection decision No. 61/QD (29.04.2025) against the certification authority, worki…
Data the group says was taken
- background-check dossiers
- SSNs
- medical faxes
- methadone clinic records
- medical assistance files
- driver licenses
- Green Cards
- SSN cards
- tax forms
- bank data
- payroll registers
- HR memos
- contracts
- pension records
- discipline databases
- jail gang-intelligence files
Screenshot of the leak post
Sources
Source
Indexed 3 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.