

VictimsStuga Machinery Ltd
Stuga Machinery Ltd
listed as Stuga Machinery
A claim by the operator, not a confirmed breach.
No statement from the organisation is on record here. We index the listing; we never host the data.
Our capture of the post text · Our screenshot of the post
- Listed · Jun 6, 2026
- Data published · not yet, as far as the post says
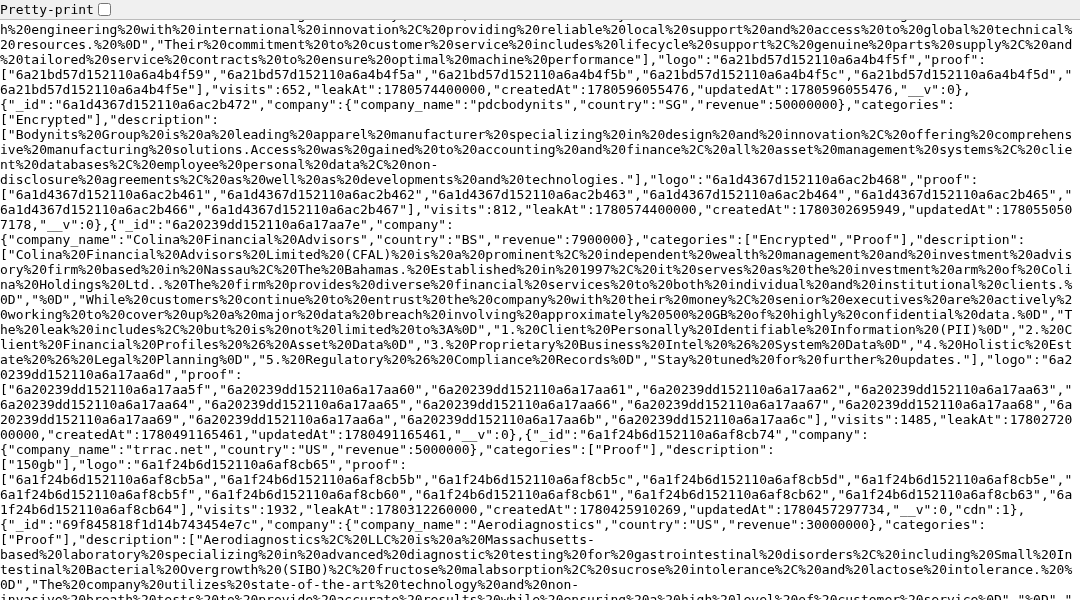
``` {"type":true,"message":"Success: got announcements.","payload":{"length":722,"announcements":[{"_id":"6a232c515ae71db30c46b0a3","company":{"company_name":"obrieneng.com","country":"US","revenue":20000000},"categories":["Proof"],"description":["contract%20nda%20confidential%20%20%20gov%5Cdot%5Cmilitary%5Cva%5Csam.gov%20other"],"logo":"6a232c515ae71db30c46b089","proof":["6a232c515ae71db30c46b072","6a232c515ae71db30…
Quoted from the captured post, reformatted. Original language preserved.
Extracted from the post text by the enrichment model; each item traces to a sentence in the capture. The post references about 6 proof files.
INC Ransom claims to have exfiltrated data from Stuga Machinery, with proof files advertised. The leak post describes access to company systems and data related to the machinery manufacturer.
Severity medium: Proof files are published (6 proof items) and exfiltration is claimed, but the leak post does not specify the nature or sensitivity of the data beyond general company systems. No PII, financial records, or regulated data types are explicitly mentioned in the available description.
- Treat every credential named in the post as compromised: reset, revoke sessions, enforce a second factor.
- Open the incident with NCSC and your regulator before data is published, not after.
- Watch the listing: a tracked domain is re-checked against every new post and you are paged when this one changes status or another operator names the organisation.