

Ransomware victim disclosure
← All victimsKarl Kuntze GmbH & Co.
Claimed by Safepay · listed 1 hour ago
Today
Age
since listed · listed for ransom
Status timeline
- ListedSep 16, 2026
Current state: Listed for ransom
At a glance
- Group
- Safepay
- Status
- Listed for ransom
- Country
- Germany
- Sector
- Manufacturing
- Listed on leak site
- Sep 16, 2026
What the group claims
Headquartered in Langenfeld, North Rhine-Westphalia, legally registered as Karl Kuntze (GmbH & Co.), HRA 16336.
The leak post
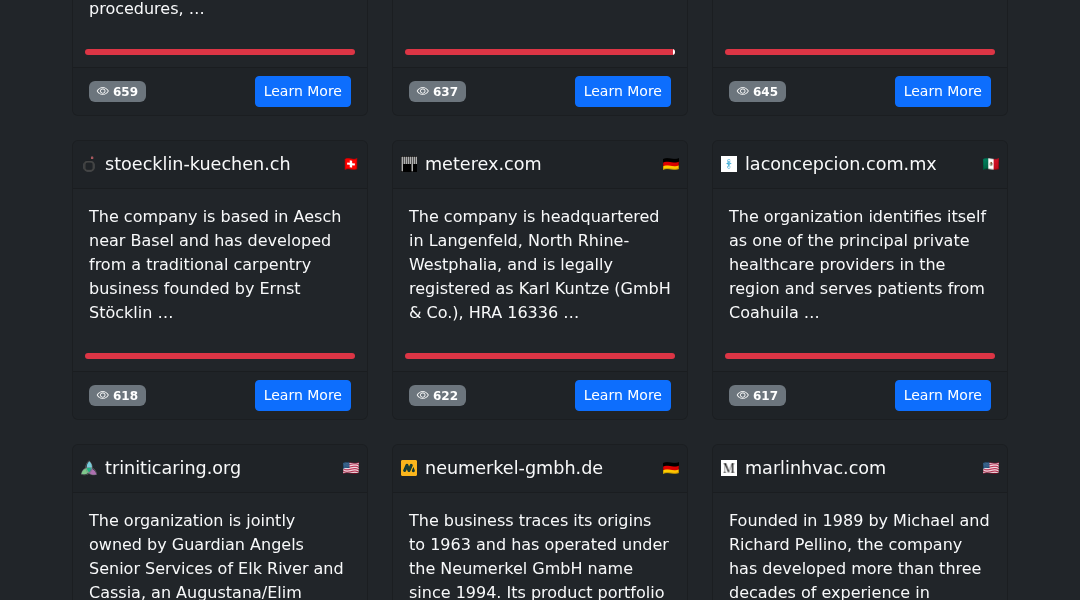
captured from the group's site# SafePay ransomware has never provided and does not provide the RaaS It serves as the country's primary online point of contact between public institutions and citizens, providing government information, administrative procedures, … Its headquarters and main wastewater-treatment facility are located at Industriering 28 in Lyss. The organization also operates the ARA Messen … Established in January 1970 as a regional computer-services center, the company has developed into a publicly listed systems integrator providing … The company is based in Aesch near Basel and has developed from a traditional carpentry business founded by Ernst Stöcklin … The company is headquartered in Langenfeld, North Rhine-Westphalia, and is legally registered as Karl Kuntze (GmbH & Co.), HRA 16336 … The organization identifies itself as one of the principal private healthcare providers in the region and serves patients from Coahuila … The organization is jointly owned by Guardian Angels Senior Services of Elk River and Cassia, an Augustana/Elim affiliation. Its headquarters … The business traces its origins to 1963 and has operated under the Neumerkel GmbH name since 1994. Its product portfolio … …
Screenshot of the leak post
Sources
Source
Indexed 1 hour agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.