Ransomware victim disclosure

← All victims

Lucid Motors

Claimed by Sovcali · listed 2 months ago

35 GB
Data size
56d
Age
since listed · listed for ransom

Status timeline

  1. ListedAug 11, 2026

Current state: Listed for ransom

At a glance

Group
Sovcali
Status
Listed for ransom
Listed on leak site
Aug 11, 2026
Data size
35 GB

About the victim

AI dossier — public-source company profile

Lucid Motors is an electric vehicle manufacturer. The company designs and produces luxury EVs. No additional details are available from public sources in this context.

Industry
Automotive Manufacturing

Attack summary

Severity: medium — The group has listed the victim and claims possession of archives, but provides no proof files, screenshots, or specific data inventory. Without published proof or clarification of what was accessed, the incident cannot be confirmed as critical or high-severity, though the automotive sector and potential engineering data warrant elevated concern.

Sovcali claims to possess archives from Lucid Motors and eShocan Engineering. The post does not specify whether data was exfiltrated, encrypted, or both, nor does it detail what specific data categories are at stake.

medium

What the group claims

Lucid Motors engineering archive claimed to be in possession of the ransomware group Sovcali.

The leak post

captured from the group's site
Sat, Aug 29 · 03:02 AM
In line with our previously discussed approach, the proposed strategy to formally demonstrate to Lucid that we are in possession of their data consists of the controlled upload of approximately 35 GB of technical material.This dataset comprises finite element analysis (FEA/CAE) files, specifically .fem model files, .h3d result files, .out and .spcf output files, together with associated summary reports in .pptx and .xlsx formats. The materials focus on stiffness studies, strain-energy evaluations, displacement assessments, and NVH analyses relating to the mid-sized IC display housing and the Pull/Outboard Switch simulations. 
### They Failed. 100GB Drops in 2 Days 
Despite giving the Lucid Motors company more than enough time to respond and deliberately keeping the pressure relatively low, they have still failed to take any appropriate action.In two days we will release a further update, make our position crystal clear, and also publish 100 GB of data

Data the group says was taken

  • engineering archive

Screenshot of the leak post
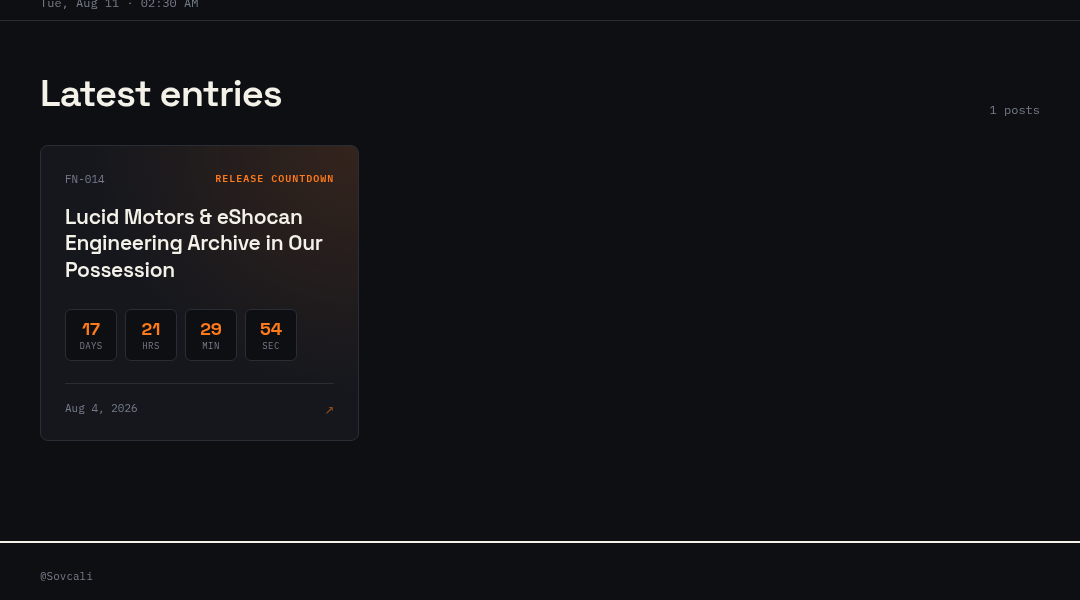
Leak screenshot for Lucid Motors

Sources

Source

Indexed 2 months ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Sovcali

Sovcali is a ransomware group first observed in August 2026 with an apparently financial motivation, though limited public documentation exists given its recent emergence and small known victim footprint. With only one confirmed victim recorded to date, the group remains obscure, and no attributions to a specific country of origin, threat actor collective, or ransomware-as-a-service infrastructure have been publicly documented by CISA, the FBI, Mandiant, or other reputable security research organizations at this time. What is known from available data is that Sovcali has demonstrated a targeting preference for the transportation sector within the United States, suggesting a degree of deliberate victim selection rather than opportunistic targeting, though the limited sample size makes definitive pattern analysis premature. No specific initial access vectors, encryption methods, extortion tactics, or toolsets have been publicly attributed to this group in open-source intelligence reporting. No notable high-profile campaigns, record ransoms, or law enforcement actions involving Sovcali have been publicly documented. Given its August 2026 first-observed date and minimal victim count, Sovcali should be considered an emerging and under-documented threat actor warranting continued monitoring as additional telemetry and reporting become available. The group has been linked to 6 public disclosures across our corpus. First observed on a leak site on August 9, 2026; most recent post August 24, 2026. The operation is currently active.

Timeline of this disclosure

  • August 11, 2026Lucid Motors listed by Sovcali on the group's public leak site
Data size
35 GB

Sector and geography

This disclosure adds to ransomware activity in the Automotive sector, which has 101 disclosures indexed across all operators we track.

If your organisation is affected

A listing by Sovcali means Lucid Motors appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Monitor for the data appearing on Sovcali's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.