

Ransomware victim disclosure

All victims

Unknown Company ($3.3M demand)

Claimed by Clop · listed 2 hours ago

Today
Age
since listed · data leaked

Status timeline

  1. ListedSep 20, 2026
  2. Data leakeddate unknown

At a glance

Group
Clop
Status
Data leaked
Listed on leak site
Sep 20, 2026

About the victim

AI dossier — public-source company profile

Unknown company. The leak post references 'State of Florida' and a large organization with data center operations, Salesforce instances, and SharePoint infrastructure, but the actual victim name has been redacted or remains unidentified in the available excerpt.

Attack summary

Severity: critical — Confirmed exfiltration of massive scale PII (12.9M+ Salesforce records, 8,300+ employee records), PHI indicators, physical security infrastructure documentation, credential artifacts, and access control systems. Data includes operational security-critical materials for data centers and facilities. Multiple sensitive data categories at enterprise scale.

The Clop group claims to have exfiltrated approximately 12.9 million Salesforce records, 645 GB of SharePoint data, customer contact information, employee PII, physical security documentation (data center drawings, floor plans, electrical diagrams), security policies, credential artifacts, and access control logs. The group also claims encryption of systems and threatened data publication after failed ransom negotiations.

critical

Data the group says was taken

AI dossier — extracted from the leak post
  • 12.9 million Salesforce records
  • 645 GB SharePoint data (288,729 files, 60,513 folders)
  • 182,000+ customer contact records
  • 8,300+ employee PII records
  • Executed contracts, MSAs, NDAs, leases, SOWs
  • Physical key inventory logs and contractor audit photos
  • Data center drawings, floor plans, electrical diagrams, security system schematics
  • CERM process library
  • Physical and information security policies
  • Regional security scorecards and KPI workbooks
  • Credential and access control artifacts (PasswordList.xlsx, Okta SSC lists, badge reports, access control forms)

What the group claims

Customer data, employee data, and other internal corporate data was compromised. Company engaged but made paltry offers and did not want to pay the requested amount, resulting in data leak.

The leak post

captured from the group's site
**IF YOU WANT TO SAVE YOUR BRAND AND NOT DIE BY MY HANDS:** Email us from your official email at [email protected] and lets see how rich you really are. 2.333% of my networth is a 8 figure amount, I hope you can pay that much because that is the demand, negotiable. Get your bosses in front of the white board in the war room. Clock is ticking moron. Kindly excuse our unprofessionalism.
We are aware of the situation involving a number of our CDNs being unreachable. We are working on restoring them. We estimate 24 to 48 hours till they are back. 91.215.85.22 remains accessible and usable. **Update, July 27, 3:01 a.m. ET:** All CDN mirrors are back online; however, content synchronization across all three mirrors is still ongoing. Addicionally, we are still working on preparing the release of the torrents. We kindly ask our visitors to seed once they become available. A notification will be posted upon release. All CDN mirrors are currently experiencing a service disruption. **All files are fully backed up and no data has been lost.** At this time we do not have an estimated time of resolution.We are working to restore service promptly and will share updates as they become avail…

Data the group says was taken

  • customer data
  • employee data
  • internal corporate data

Screenshot of the leak post
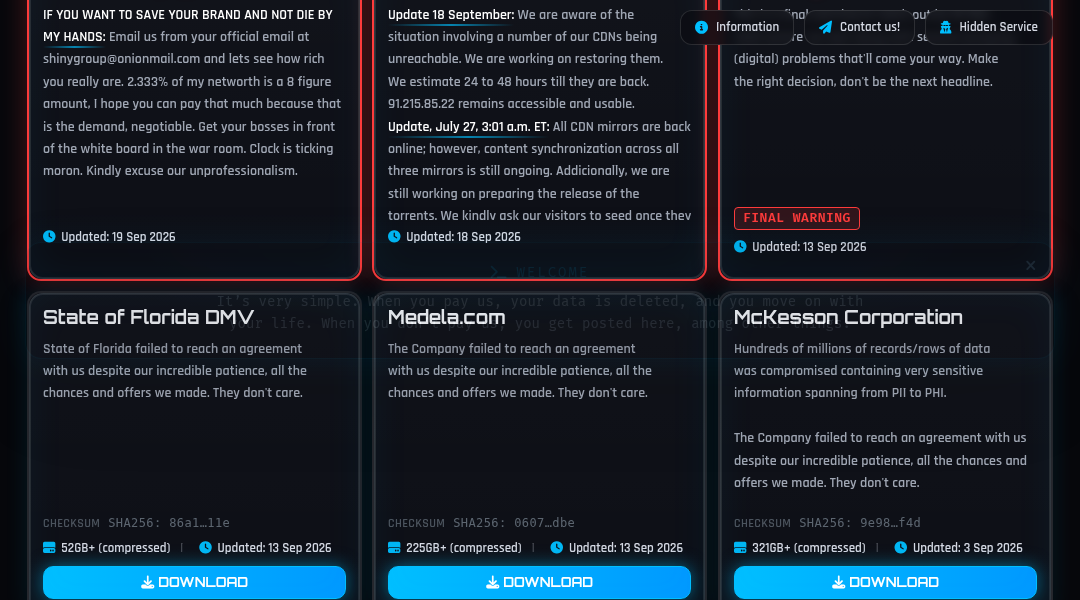
Leak screenshot for Unknown Company ($3.3M demand)

Sources

Source

Indexed 2 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About clop

Clop (also stylized as "Cl0p") is a financially motivated ransomware group and cybercriminal enterprise that emerged in early 2020 as an evolution of the earlier CryptoMix ransomware family, operating primarily for monetary extortion against large enterprise targets. The group is widely assessed by Mandiant, CISA, and other reputable researchers to have ties to Russian-speaking cybercriminal actors, with some researchers linking their operations to the broader FIN11 threat cluster; they operate a Ransomware-as-a-Service (RaaS) model while also conducting direct intrusion operations. Clop is particularly distinguished for its aggressive exploitation of zero-day and n-day vulnerabilities in managed file transfer (MFT) and enterprise software platforms as primary initial access vectors, most notably the exploitation of Accellion FTA (2020-2021), Fortra GoAnywhere MFT (CVE-2023-0669), and the MOVEit Transfer vulnerability (CVE-2023-34362) in 2023, and consistently employs double extortion tactics — exfiltrating sensitive data prior to or in lieu of encryption and threatening public disclosure on their dedicated leak site to coerce payment. Clop has been responsible for some of the most impactful ransomware campaigns on record, with their 2023 MOVEit exploitation campaign alone affecting over 1,000 organizations globally and impacting entities including Shell, the U.S. Department of Energy, British Airways, and numerous U.S. federal agencies, with the broader campaign representing one of the largest mass-exploitation events in ransomware history; Ukrainian law enforcement arrested six individuals linked to Clop operations in June 2021, though the group's core leadership is assessed to remain outside of effective law enforcement jurisdiction. As of the most recent publicly available intelligence, Clop remains active, continuing to leverage vulnerability exploitation campaigns against enterprise file transfer solutions and maintaining a victim count exceeding 1,250 known organizations, with consistent targeting concentrated in the United States, Canada, United Kingdom, Australia, and Germany across technology, business services, manufacturing, and consumer services sectors. The group has been linked to 1,352 public disclosures across our corpus. First observed on a leak site on March 13, 2020; most recent post September 20, 2026. The operation is currently active.

Also tracked as: Cl0p.

Timeline of this disclosure

  • September 20, 2026Unknown Company ($3.3M demand) listed by clop on the group's public leak site

If your organisation is affected

A listing by clop means Unknown Company ($3.3M demand) appeared on a ransomware extortion site and data attributed to it has been published. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Monitor for the data appearing on clop's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.