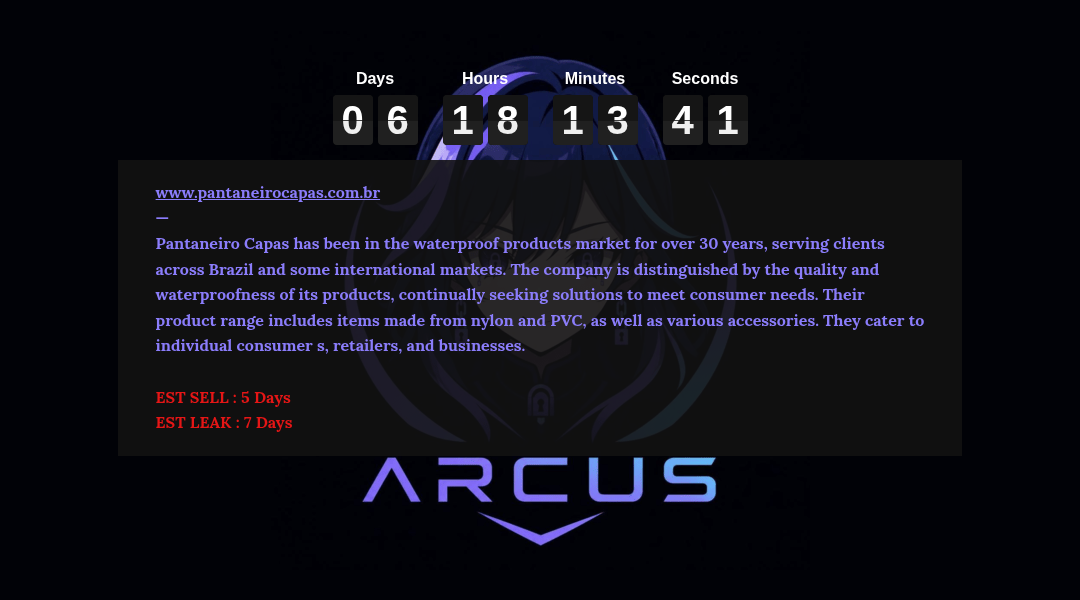
Arcusmedia is a relatively new ransomware group that emerged in May 2024, operating with apparent financial motivations based on their targeting patterns across multiple countries and sectors. The group's origin and potential state affiliations remain unclear given limited public documentation from established threat intelligence sources, though their targeting of victims across Brazil, the United States, Spain, UAE, and Mexico suggests either a geographically distributed operation or deliberate international scope. With 98 documented victims in a short operational timeframe, Arcusmedia has demonstrated notable activity levels, primarily focusing on technology, business services, agriculture and food production, and transportation/logistics sectors, though their targeting appears opportunistic rather than strategically focused given the "Not Found" classification as their primary sector target. Limited public reporting from major cybersecurity firms and law enforcement agencies means specific details about their attack methodologies, initial access vectors, encryption techniques, or whether they employ double extortion tactics remain undocumented in authoritative sources. No major campaigns, high-profile victims, or significant law enforcement actions against Arcusmedia have been publicly reported by CISA, FBI, or established threat intelligence organizations. Current operational status appears active based on the recent emergence timeframe, though comprehensive threat intelligence profiles from reputable sources have not yet been published given the group's recent appearance in the threat landscape. The group has been linked to 115 public disclosures across our corpus. First observed on a leak site on May 15, 2024; most recent post September 27, 2026. The operation is currently inactive.
Also tracked as: arcus media.
Sector and geography
This disclosure adds to ransomware activity in the Manufacturing sector, which has 3,696 disclosures indexed across all operators we track. Geographically, Pantaneiro Capas is reported in Brazil, a country with 209 ransomware disclosures in our corpus.
If your organisation is affected
A listing by Arcusmedia means Pantaneiro Capas appeared on a ransomware extortion site and data attributed to it has been published. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.
- Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
- Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
- Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
- Report the incident to your national CERT, CERT.br (Brazil), as required for your jurisdiction.
- Monitor for the data appearing on Arcusmedia's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.
How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.