

Ransomware victim disclosure
← All victimsReveal (Ipro.com)
listed as Ipro.com(revealdata.com) customer DB + full database backup · Claimed by Emperador · listed 17 days ago
Status timeline
- ListedAug 27, 2026
- Data leakeddate unknown
At a glance
- Group
- Emperador
- Status
- Data leaked
- Sector
- Technology
- Listed on leak site
- Aug 27, 2026
- Data size
- 300 GB
- Records
- 17000 files
About the victim
AI dossier — public-source company profileReveal is an AI-powered eDiscovery and investigations platform founded in 2008 that serves corporations, law firms, government agencies, and legal service providers. The company offers solutions for data management, litigation support, legal holds, FOIA requests, and data subject access requests across multiple industries.
- Industry
- Legal Technology & eDiscovery Software
- Founded
- 2008
Attack summary
Severity: critical — Exfiltration of customer database and full backup containing sensitive legal/case data with client relationships and transcripts. Customers include government and law firms handling regulated matters. Affects regulated sector (legal/government) with scale and sensitive operational data.The operator claims to have exfiltrated Reveal's customer database containing customer identifiers, contact information, location data, account metadata, internal system IDs, and client relationships. Additionally, a full database backup from 2023 (79.5 MB) is claimed to contain transcripts and case data. The operator states this is a re-posting of previously leaked data under a different alias.
Data the group says was taken
AI dossier — extracted from the leak post- customer identifiers
- contact information
- location data
- account metadata
- internal system IDs
- client relationships
- transcripts
- case data
What the group claims
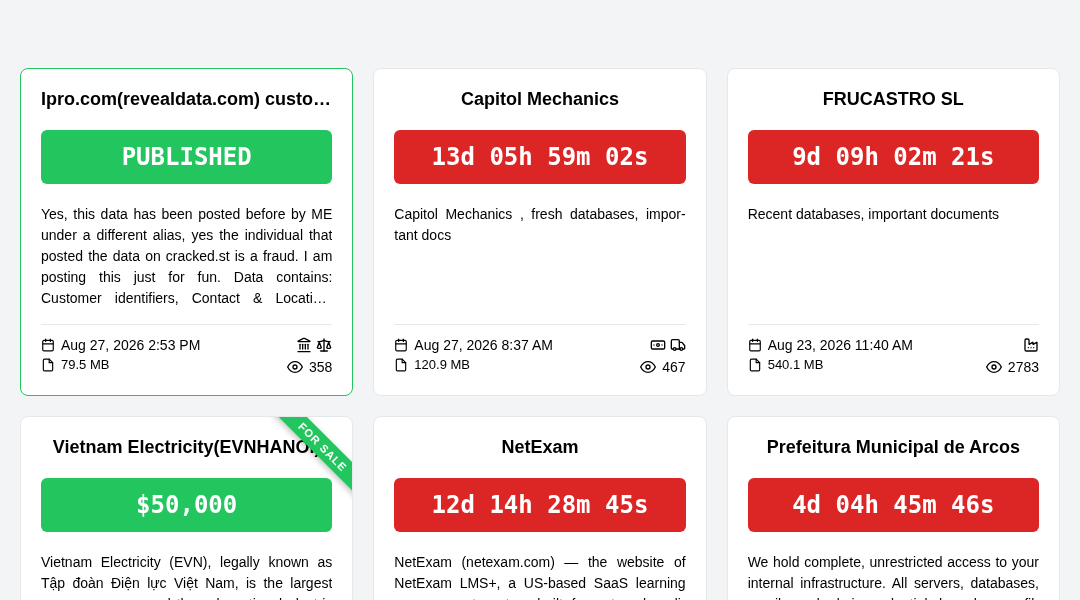
Yes, this data has been posted before by ME under a different alias, yes the individual that posted the data on cracked.st is a fraud. I am posting this just for fun. Data contains: Customer identifiers, Contact & Location, Account metadata, Internal System IDS, Client relationships. The full database backup contains everything such as transcripts, cases, though it is from 2023. [Size: 79.5 MB | Sector: Government, Law]
The leak post
captured from the group's site[ Ipro.com(revealdata.com) customer DB + full database backup Yes, this data has been posted before by ME under a different alias, yes the individual that posted the data on cracked.st is a fraud. I am posting this just for fun. Data contains: Customer identifiers, Contact & Location, Account metadata, Internal System IDS, Client relationships. The full database backup contains everything such as transcripts, cases, though it is from 2023. ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/iprocomrevealdatacom-customer-db-full-database-backup/) [ Capitol Mechanics , fresh databases, important docs ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/capitol-mechanics/) [ ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/frucastro-sl/) [ Vietnam Electricity (EVN), legally known as Tập đoàn Điện lực Việt Nam, is the largest power company and the sole national electric utility in Vietnam. Fully owned and controlled by the Vietnamese government since its inception in 1994, EVN operates as a vertically integrated monopoly responsible for the nationwide generation, transmission, and distribution of electricity, …
Screenshot of the leak post
Sources
- Victim siterevealdata.com
- Leak post/post/iprocomrevealdatacom-customer-db-full-database-backup/
Source
Indexed 17 days agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.