

Ransomware victim disclosure
← All victimsASCOM S.p.A.
listed as ASCOM S.p.A. ascom-italy.it serviced by an IT company Emilcom S.r.l. · Claimed by Blacknevas · listed 2 months ago
Status timeline
- ListedAug 14, 2026
- Data leakeddate unknown
At a glance
- Group
- Blacknevas
- Status
- Data leaked
- Country
- Italy
- Sector
- Manufacturing
- Listed on leak site
- Aug 14, 2026
- Data size
- 1.2 TB
- Records
- 145146 files
About the victim
AI dossier — public-source company profileASCOM S.p.A. is an Italian manufacturer specializing in travel lifts, gantry cranes, overhead cranes, and customized lifting solutions for marine, industrial, and infrastructure sectors. Founded in 1972 in Formigine (Modena), the company operates a 9,000 m² in-house production facility and serves customers in over 50 countries, with ISO 9001, 14001, and 45001 certifications.
- Industry
- Heavy Lifting Equipment & Marine/Industrial Machinery
- Address
- Via Della Fornace 16, 41043 Formigine (MO), Italy
- Founded
- 1972
Attack summary
Severity: low — The disclosure is an announcement with company background details but contains no stated proof files, screenshots, or specific data samples. No confirmation of exfiltration or encryption impact is provided in the leaked post itself.The blacknevas group claims to have accessed ASCOM S.p.A.'s systems via compromised IT service provider Emilcom S.r.l. The leak post does not specify whether data was encrypted, exfiltrated, or both, nor does it detail what specific data categories were compromised.
What the group claims
ASCOM S.p.A. is an Italian manufacturer of heavy lifting equipment for the marine (marinas & shipyards) and industrial sectors. Founded in 1972 by Gian Franco Schedoni in Formigine (Modena), the company began with overhead cranes and expanded into boat hoists (travel lifts) around 1982.Today it is a global specialist in travel lifts, gantry cranes, overhead cranes, and fully customized lifting solutions, with thousands of machines operating in over 50 countries. Production is fully in-house (9,000 m² facility), supported by its own engineering team using FEM analysis and modern CAD tools.Key facts:Certified ISO 9001, 14001 & 45001; all equipment CE-markedFocus on quality, customization, and sustainabilityServes marinas, shipyards, infrastructure, steel mills, renewable energy, mining, and moreHeadquarters: Via Della Fornace 16, 41043 Formigine (MO), ItalyPhone: +39 059 558038Email: [email protected]: ascom-italy.it
The leak post
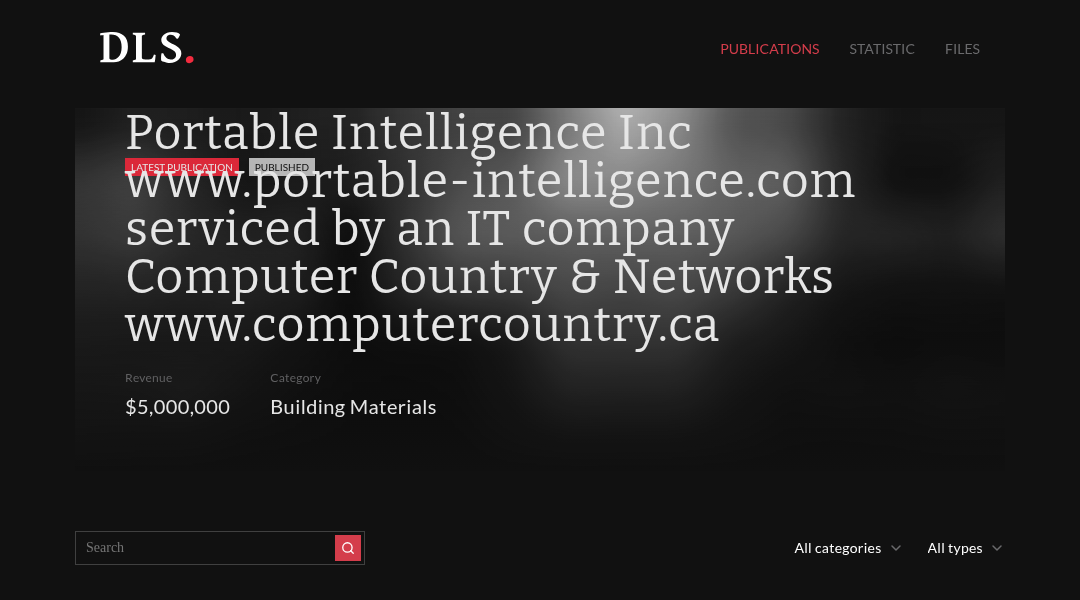
captured from the group's site[ Portable Intelligence Inc www.portable-intelligence.com serviced by an IT company Computer Country & Networks www.computercountry.ca ](http://ctyfftrjgtwdjzlgqh4avbd35sqrs6tde4oyam2ufbjch6oqpqtkdtid.onion/334ea365-5531-4a9e-902e-8936568e0e87) [ Jack Rutherford Customs Brokers Ltd / The Rutherford Group www.therg.ca serviced by an IT company Computer Country & Networks www.computercountry.ca Jack Rutherford Customs Brokers Ltd. is a Canadian customs brokerage company currently operating under the brand name The Rutherford Group. The company provides comprehensive logistics services, primarily: customs brokerage (import and export clearance, clearance through Canadian and US customs, compliance consulting, CARM, surety bonds, etc.). They have PIP (Partners in Protection) status.Transportation: shipping within Canada, the US, and internationally.Warehousing: bonded warehouses (including CBSA sufferance), pick & pack, storage, including FDA-certified warehouses in Port Huron, Michigan.The company was founded in 1974 by Jack Rutherford in Stratford, Ontario. Now a family-owned business (second generation – John Rutherford), it positions itself as a one-stop shop for cross-border logis…
Screenshot of the leak post
Sources
Source
Indexed 2 months agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.