

Ransomware victim disclosure
← All victimsDebene S.A.
listed as Unknown company · Claimed by TiMc · listed 47 minutes ago
Status timeline
- ListedSep 30, 2026
Current state: Listed for ransom
At a glance
- Group
- TiMc
- Status
- Listed for ransom
- Listed on leak site
- Sep 30, 2026
- Data size
- 1TB+
About the victim
AI dossier — public-source company profileDebene S.A. is an IT solutions company operating data center and file storage infrastructure. The group's post references healthcare-related systems (COVID-19 database, Oncomine KB), suggesting involvement in medical or life sciences technology services.
- Industry
- IT Solutions & Healthcare Technology
Attack summary
Severity: critical — Confirmed exfiltration of 1TB+ data including PII, healthcare records (COVID-19 database), and proprietary source code. Healthcare data and regulated information at scale qualify as critical; operational compromise of DC/FS infrastructure amplifies impact.TiMc claims to have compromised Debene S.A.'s data center and file storage systems, exfiltrating 1TB+ of data including personally identifiable information (PII), trade records, database backups, COVID-19 records, and proprietary SaaS source code. The group alleges total intranet control and threatens full data publication after a deadline.
Data the group says was taken
AI dossier — extracted from the leak post- Personally identifiable information (PII)
- Trade records
- MySQL database backups (20GB+)
- COVID-19 database
- SaaS source code (Oncomine KB and other applications)
- Intranet data
The group's post references roughly 3 proof file previews advertised (Gofile links) proof files.
What the group claims
Intranet breached with total control gained. Data exfiltrated includes COVID-19 database, SaaS source code including oncomine KB, and other PII. Full data breach after deadline.
The leak post
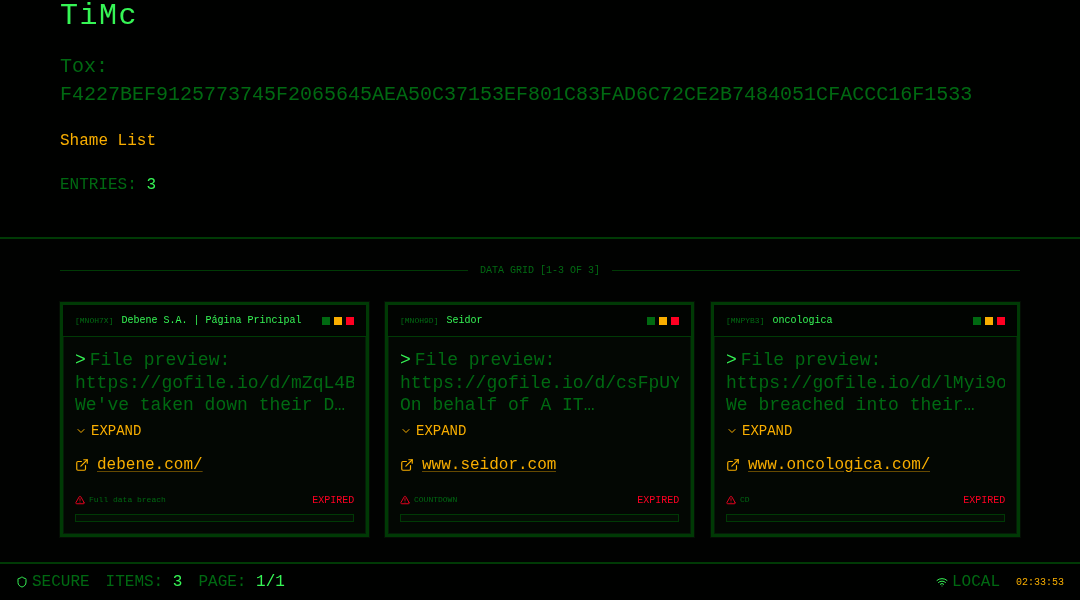
captured from the group's siteDATA GRID [1-3 OF 3] Debene S.A. | Página Principal File preview: https://gofile.io/d/mZqL4B We've taken down their DC and FS, 100GB+ of the data including PII, Trade record and Full 20GB+ MySQL database backup files Due to their non-behavior we choose to put them on our shame list , full data breach will take place after the deadline File preview: https://gofile.io/d/csFpUY On behalf of A IT solution company , the first response to the data breach was trying to cover the truth, shame on you When the countdown was over, we will public your newest 200GB+ data. File preview: https://gofile.io/d/lMyi9o We breached into their intranet and have total control of it , with 1TB+ data exfiltrated including covid-19 database and SaaS src code like oncomine KB and Other PII Full data breach after the DDL
Data the group says was taken
- COVID-19 database
- SaaS source code
- PII
Screenshot of the leak post
Sources
Source
Indexed 47 minutes agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.