

Ransomware victim disclosure

← All victims

Yale University Press (Yale Books)

Claimed by Scarlettgroup · listed 4 hours ago

64000+ PII records, 28000+ transactions
Records
Today
Age
since listed · listed for ransom

Status timeline

  1. ListedOct 9, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Listed on leak site
Oct 9, 2026
Records
64000+ PII records, 28000+ transactions

About the victim

AI dossier — public-source company profile

Yale University Press is the scholarly publishing division of Yale University, responsible for publishing and distributing academic, educational, and general-interest books. The organization operates the Yale Books platform for showcasing and selling its publications.

Industry
Academic Publishing

Attack summary

Severity: critical — Confirmed exfiltration of PII at scale (64k+ records) affecting students and employees, combined with partial payment card data from 28k+ transactions, API secrets, and sensitive educational/administrative records. This meets the threshold for regulated sensitive data exposure.

Scarlettgroup claims to have exfiltrated 64,000+ personal records (PII) from students and employees, 28,000+ payment transaction records with partial card data (CC type, masked PAN, expiration, billing details), source code, educational course materials, instructor and student request data, exam resources with answer keys, API secrets, registration forms, and additional administrative exports.

critical

Data the group says was taken

AI dossier — extracted from the leak post
  • 64k+ student and employee PII
  • 28k+ transaction records with partial payment card data
  • Source code
  • Course materials and assets
  • Course resources
  • Instructor requests
  • Student requests
  • Exam desk copies with answer keys
  • API secrets and keys
  • Registration form entries
  • WPForms exports

What the group claims

Yale University Press's Yale Books website showcases and sells scholarly, academic, and general-interest books.

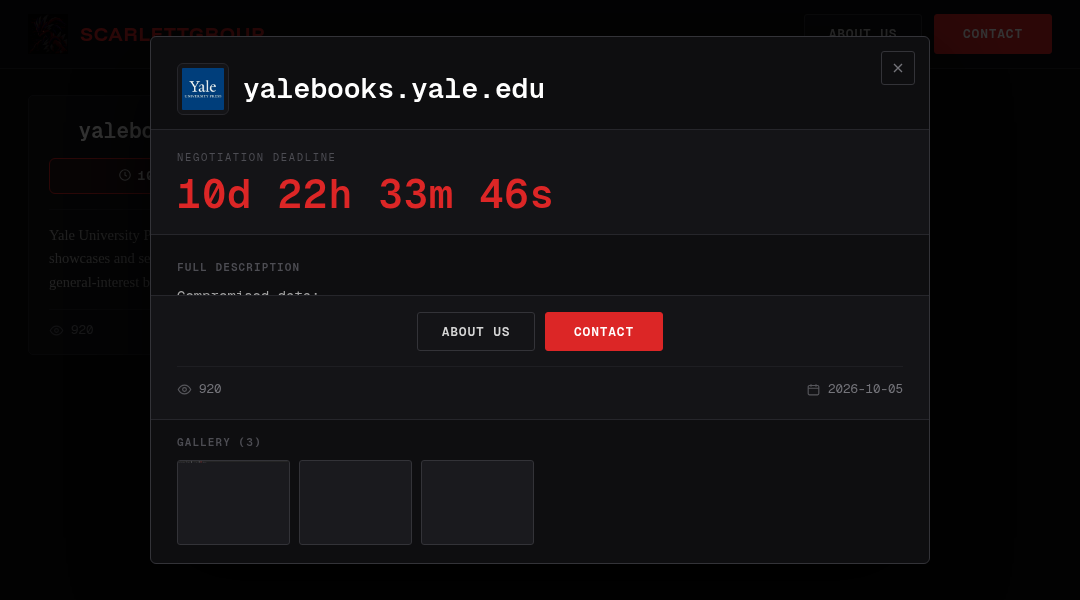
The leak post

captured from the group's site
[ Yale University Press’s Yale Books website showcases and sells scholarly, academic, and general-interest books. ](http://scarlettgugldabhgz3uertpnxglxytddxbd5vnoma5pihfk6k5q2sid.onion/?open=02e92f3aae2c37615f)
Compromised data: 64k+ PII on all students and employees 28k+ TXNS (CC Type, masked PAN, MM/YY, Billing, Total, Date, ID) Yalebooks Source Code Course Assets Course Resources Instructor Request Student Request Exam Desk Copies (with answer keys) Secrets Keys Registration Form Entries WPForms Export & More

Data the group says was taken

  • PII
  • Credit Card Transactions
  • Source Code
  • Course Assets
  • Course Resources
  • Instructor Requests
  • Student Requests
  • Exam Desk Copies
  • Answer Keys
  • Secret Keys
  • Registration Form Entries
  • WPForms Export

Screenshot of the leak post
Leak screenshot for Yale University Press (Yale Books)

Sources

Source

Indexed 4 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Scarlettgroup

Scarlettgroup is a ransomware threat actor first observed in October 2026 with an apparent financial motivation, though its limited operational history makes comprehensive attribution difficult at this time. Based on available data, the group has recorded at least one confirmed victim, with targeting concentrated in the United States and a demonstrated focus on the education sector, a vertical commonly pursued by ransomware actors due to historically under-resourced cybersecurity postures and the sensitivity of student and institutional data. Beyond these initial targeting patterns, Scarlettgroup remains an obscure and poorly documented threat actor with no substantial public reporting from authoritative sources such as CISA, the FBI, Mandiant, or established threat intelligence vendors as of the time of this profile's compilation; its origin, affiliation, tooling, initial access methods, and extortion tactics have not been publicly characterized in sufficient detail to permit confident attribution or methodological assessment. Given the group's very recent emergence and minimal victim count, it is possible that Scarlettgroup represents either an early-stage independent ransomware operation, a new affiliate under an established Ransomware-as-a-Service framework, or a rebranded entity, though none of these hypotheses can be confirmed without additional corroborating intelligence. Analysts should treat this group as an emerging and developing threat warranting continued monitoring, particularly within the US education sector. The group has been linked to 3 public disclosures across our corpus. First observed on a leak site on October 8, 2026; most recent post October 9, 2026. The operation is currently active.

Timeline of this disclosure

  • October 9, 2026Yale University Press (Yale Books) listed by Scarlettgroup on the group's public leak site
Records
64000+ PII records, 28000+ transactions

Other recent disclosures by Scarlettgroup

Scarlettgroup has been linked to 3 public victims on Darkfield. A sample of the most recent:

See the full Scarlettgroup dossier →

Sector and geography

This disclosure adds to ransomware activity in the Education / Publishing sector. Geographically, Yale University Press (Yale Books) is reported in United States, a country with 3,176 ransomware disclosures in our corpus.

If your organisation is affected

A listing by Scarlettgroup means Yale University Press (Yale Books) appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CISA (United States), as required for your jurisdiction.
  • Monitor for the data appearing on Scarlettgroup's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.