

Ransomware victim disclosure
← All victimsVera Science
Claimed by Genesis · listed 15 hours ago
Status timeline
- ListedOct 1, 2026
- Data leakeddate unknown
At a glance
- Group
- Genesis
- Status
- Data leaked
- Country
- United States
- Sector
- Healthcare
- Listed on leak site
- Oct 1, 2026
About the victim
AI dossier — public-source company profileVeroScience is a biotechnology company focused on developing therapies for metabolic diseases and immunological disorders. The company operates a hybrid academic-industrial model and conducts preclinical and clinical research nationwide. It is known for Cycloset®, an FDA-approved dopamine D2 receptor agonist for type 2 diabetes treatment.
- Industry
- Biotechnology & Pharmaceuticals
Attack summary
Severity: critical — Confirmed exfiltration of medical data and pharmaceutical information from a biotechnology company with active clinical programs. Medical data at this scale combined with pharmaceutical research data and customer information represents regulated sensitive data exposure.The Genesis group claims to have exfiltrated approximately 200 GB of data from VeroScience, including medical data databases, pharmaceutical data, and customer records taken from company file servers.
Data the group says was taken
AI dossier — extracted from the leak post- Medical data databases
- Pharmaceutical data
- Customer data
- Company file server data
What the group claims
A Biotechnology Company
The leak post
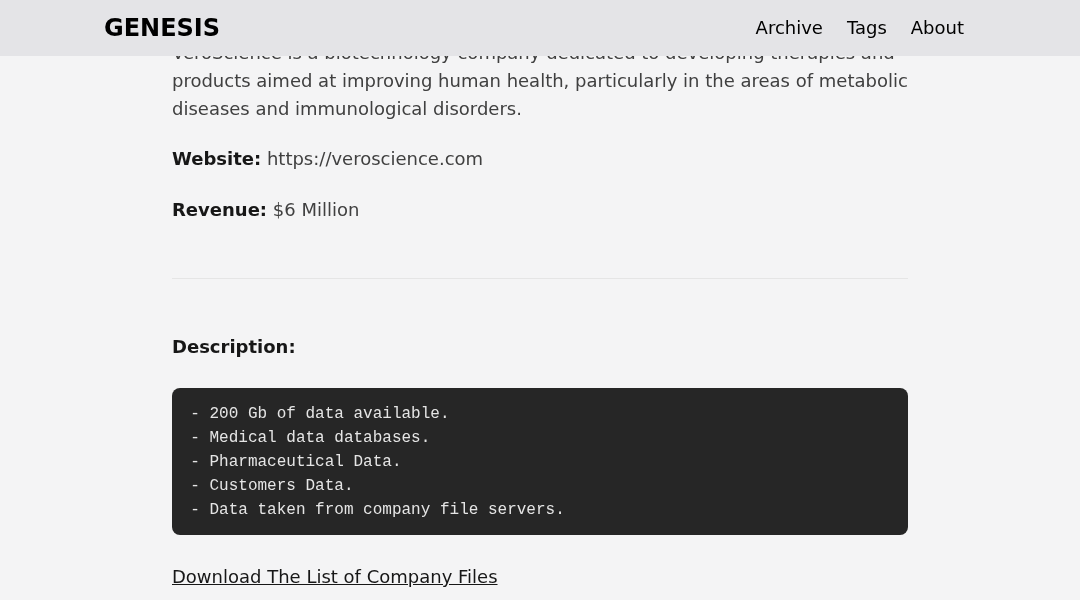
captured from the group's siteVeroScience is a biotechnology company dedicated to developing therapies and products aimed at improving human health, particularly in the areas of metabolic diseases and immunological disorders. ``` - 200 Gb of data available. - Medical data databases. - Pharmaceutical Data. - Customers Data. - Data taken from company file servers. ``` [Download The List of Company Files](http://genesis6ixpb5mcy4kudybtw5op2wqlrkocfogbnenz3c647ibqixiad.onion/download/b01a7fe1fb949a40cf23.zip)
Screenshot of the leak post
Sources
Source
Indexed 15 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.