

Ransomware victim disclosure

All victims

LETI (Laboratorio de Diagnóstico y Aplicaciones Terapéuticas, SA)

Claimed by Deadlock · listed 2 days ago

2d
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 14, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Country
Spain
Listed on leak site
Sep 14, 2026

About the victim

AI dossier — public-source company profile

LETI is a Spanish biopharmaceutical company specializing in diagnostic laboratory services and therapeutic applications. No public website or additional company details are available in the disclosure.

Industry
Biopharmaceutical / Diagnostic Laboratory

Attack summary

Severity: low — The leak post contains only a listing/announcement with the victim name mentioned briefly at the end of a truncated excerpt. No proof files, data inventory, or operational impact details are provided in the available text.

Deadlock claims to have exfiltrated data from LETI but provides no specific details about the scope, nature of data, or operational impact in the truncated leak post excerpt provided.

low

What the group claims

Spanish biopharmaceutical company founded in 1999, headquartered in Madrid. Specializes in research, development and manufacture of products for allergy diagnostics and allergen immunotherapy (ASIT).

The leak post

captured from the group's site
Furniture Bargaining Council in South Africa. This is the tariff council for the furniture, mattress and upholstery industry.The platform serves employers and employees in the industry in regions such as Gauteng, North West, Mpumalanga, Limpopo and the Free State to handle legal and administrative processes. 
186,207 files (incl. 58,000+ scanned documents), structured as: 47,749 unique SA ID numbers 39,014 bank account records 10,498 salary/payment values 28,175 pension fund records 20,420 payroll files 13,209 medical aid records 20,661 dispute/arbitration files — including unpublished award drafts and settlement discussions Full staff list with personal email addresses, and personal folders of employees
SHAHEEN LAW GROUP PLC - Richmond, Virginia, USA
, established 1995 by (†2025 - the General Assembly of Virginia honored him with a resolution; google it, it is touching). Now run by his three sons. 48 employees across four offices: Richmond, Midlothian, Virginia Beach, Newport News. What do they do? They close 150+ real estate transactions EVERY MONTH for some of the largest corporate relocation programs in America. When a Fortune-500 moves an employee to Virginia, this firm holds …

Screenshot of the leak post
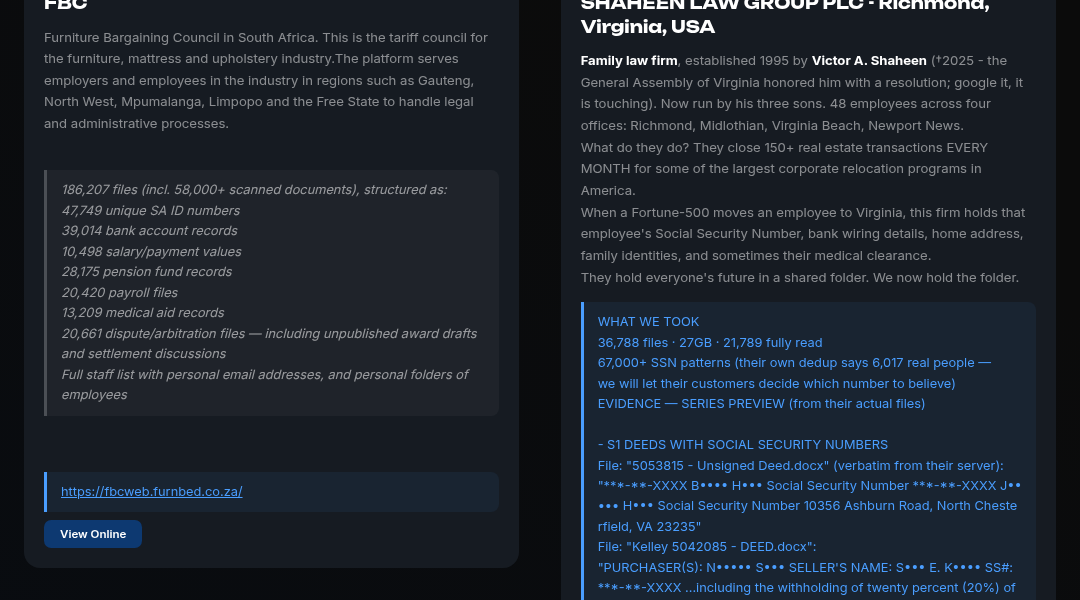
Leak screenshot for LETI (Laboratorio de Diagnóstico y Aplicaciones Terapéuticas, SA)

Sources

Source

Indexed 2 days ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Deadlock

Deadlock is a ransomware group first observed in June 2026 with an apparent financial motivation, having claimed responsibility for attacks against at least 10 known victims across a geographically diverse target set. Given the recency of their emergence and limited public documentation by major threat intelligence organizations such as CISA, FBI, or Mandiant at this time, a comprehensive technical profile cannot be fully established. Based on available victimology data, the group has demonstrated a targeting pattern spanning Singapore, China, Sweden, Spain, and Nigeria, suggesting an opportunistic or globally distributed operational scope rather than a regionally focused campaign. Targeted sectors include manufacturing, business services, telecommunications, and financial services, indicating a preference for industries with high operational dependencies and potential for significant disruption, which is consistent with financially motivated ransomware actors seeking maximum leverage for ransom payment. No confirmed attribution regarding country of origin, RaaS affiliation, or specific tooling has been publicly documented by authoritative sources as of this profile's preparation. Due to the group's nascent operational timeline and the limited volume of publicly verified intelligence, analysts should treat this profile as preliminary and subject to significant revision as additional technical indicators, victim disclosures, and research reporting become available. Continued monitoring is advised given the cross-sector and cross-regional targeting behavior observed in this early operational phase. The group has been linked to 118 public disclosures across our corpus. First observed on a leak site on June 15, 2026; most recent post September 14, 2026. The operation is currently active.

Timeline of this disclosure

  • September 14, 2026LETI (Laboratorio de Diagnóstico y Aplicaciones Terapéuticas, SA) listed by Deadlock on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the Biopharmaceutical sector. Geographically, LETI (Laboratorio de Diagnóstico y Aplicaciones Terapéuticas, SA) is reported in Spain, a country with 351 ransomware disclosures in our corpus.

If your organisation is affected

A listing by Deadlock means LETI (Laboratorio de Diagnóstico y Aplicaciones Terapéuticas, SA) appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, INCIBE-CERT (Spain), as required for your jurisdiction.
  • Monitor for the data appearing on Deadlock's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.