

Ransomware victim disclosure
← All victimsAquamar, Inc.
Claimed by METAENCRYPTER · listed 23 hours ago
Status timeline
- ListedSep 28, 2026
Current state: Listed for ransom
At a glance
- Group
- METAENCRYPTER
- Status
- Listed for ransom
- Sector
- Food & Beverage
- Listed on leak site
- Sep 28, 2026
- Data size
- 130 GB
About the victim
AI dossier — public-source company profileAquamar, Inc. is a Food & Beverage company. No public website or detailed information is available to confirm further operational scope or scale.
- Industry
- Food & Beverage
Attack summary
Severity: medium — Confirmed exfiltration of 130 GB of data, but no specific details on data type, PII scale, or regulatory sensitivity are disclosed in the leak post. Food & Beverage sector typically carries lower regulatory sensitivity than healthcare or finance unless PII or trade secrets are involved.METAENCRYPTER claims to have exfiltrated 130 GB of data from Aquamar, Inc. The group's standard protocol involves listing the victim, disclosing a manifest of files and representative samples, and threatening progressive public release if negotiation is not initiated before a stated deadline.
Data the group says was taken
AI dossier — extracted from the leak post- exfiltrated files (nature unspecified)
What the group claims
Specializes in providing high-quality, wild-caught seafood products.
The leak post
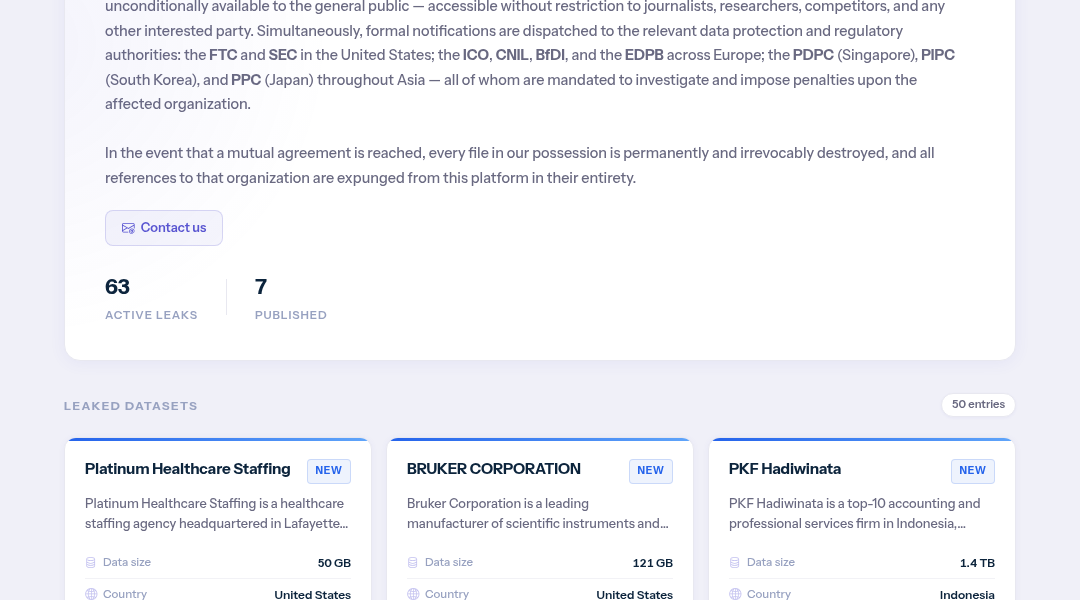
captured from the group's siteThis platform publishes data belonging to organizations that have elected to forgo negotiation entirely.Upon a company's initial listing, the complete manifest of exfiltrated files is disclosed alongside a curated selection of representative samples. Should the organization fail to establish contact prior to the stated deadline, a portion of the compromised data is released into the public domain.Should all subsequent attempts at resolution prove fruitless, the full volume of acquired data is made permanently and unconditionally available to the general public — accessible without restriction to journalists, researchers, competitors, and any other interested party. Simultaneously, formal notifications are dispatched to the relevant data protection and regulatory authorities: the and in the United States; the , , , and the across Europe; the (Singapore), (South Korea), and (Japan) throughout Asia — all of whom are mandated to investigate and impose penalties upon the affected organization.In the event that a mutual agreement is reached, every file in our possession is permanently and irrevocably destroyed, and all references to that organization are expunged from this platform in th…
Screenshot of the leak post
Sources
Source
Indexed 23 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.