

Ransomware victim disclosure

All victims

Spa and Salon Management

Claimed by Direwolf · listed 3 hours ago

Today
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 22, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Listed on leak site
Sep 22, 2026

About the victim

AI dossier — public-source company profile

Spa and Salon Management is a personal care business operating in Florida. No additional details about its specific services, scale, or operations are available from the leak post or public sources.

Industry
Health & Beauty / Personal Care

Attack summary

Severity: low — The victim is listed without any supporting proof files, data inventory, or description of operational impact. The leak post appears to be a generic announcement with no substantive evidence of compromise.

The group lists 'Spa and Salon Management' among claimed victims but provides no details about the nature of the attack (encryption, exfiltration, or both) or what data was targeted.

low

What the group claims

Spa and Salon Management company based in Florida

The leak post

captured from the group's site
Spa and Salon Management · Florida
##  PTT Oil and Retail Business
PTT Oil and Retail Business
##  Hospital Clnico Universidad de Chile
Hospital Clnico Universidad de Chile
Law Firms , Legal Services

Screenshot of the leak post
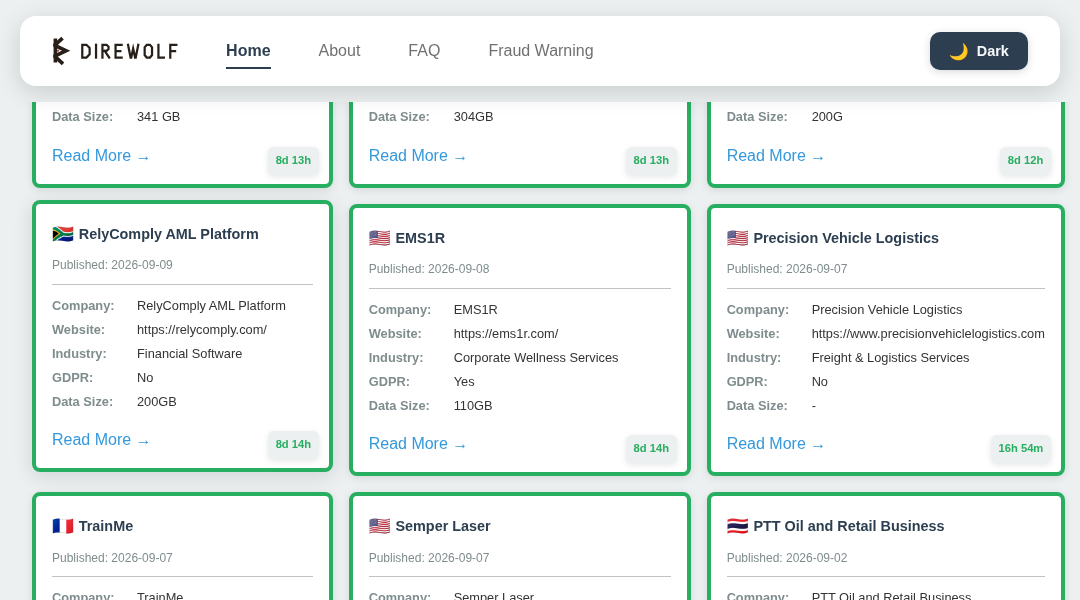
Leak screenshot for Spa and Salon Management

Sources

Source

Indexed 3 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About direwolf

Direwolf is a ransomware group that emerged in May 2025 with primarily financial motivations, having targeted 71 known victims across multiple sectors and geographic regions. The group's origin and potential affiliations remain undocumented in public threat intelligence reports, with no confirmed information regarding whether they operate as a Ransomware-as-a-Service model or as an independent entity. Their attack methodology and technical capabilities have not been extensively documented by major cybersecurity firms or government agencies, though their targeting patterns indicate a focus on manufacturing, technology, healthcare, and transportation/logistics sectors across Malaysia, the United States, Thailand, Singapore, and Taiwan. No major high-profile campaigns or significant ransomware demands have been publicly attributed to this group by CISA, FBI, or established security researchers such as Mandiant. Given the group's recent emergence and limited public documentation, their current operational status and long-term threat posture remain unclear, requiring continued monitoring by the cybersecurity community to establish a more comprehensive threat profile. The group has been linked to 139 public disclosures across our corpus. First observed on a leak site on May 27, 2025; most recent post September 22, 2026. The operation is currently active.

Also tracked as: DIRE WOLF.

Timeline of this disclosure

  • September 22, 2026Spa and Salon Management listed by direwolf on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the Health & Beauty / Personal Care sector. Geographically, Spa and Salon Management is reported in United States, a country with 11,033 ransomware disclosures in our corpus.

If your organisation is affected

A listing by direwolf means Spa and Salon Management appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CISA (United States), as required for your jurisdiction.
  • Monitor for the data appearing on direwolf's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.