

Ransomware victim disclosure
← All victimsMicro-Comm
Claimed by Barracuda · listed 2 hours ago
Status timeline
- ListedSep 25, 2026
Current state: Listed for ransom
At a glance
- Group
- Barracuda
- Status
- Listed for ransom
- Listed on leak site
- Sep 25, 2026
About the victim
AI dossier — public-source company profileMicro-Comm is a defense/military contracting company. Limited public information is available; the company does not maintain a clearnet public site.
- Industry
- Defense/Military Contracting
Attack summary
Severity: critical — Alleged exfiltration of declassified U.S. military contract documentation poses national security and regulatory risk. Defense sector data is highly sensitive. The claim references 'DECLASSIFIED' material, suggesting potential exposure of government-related information.Barracuda claims to have encrypted Micro-Comm's systems and exfiltrated data, including materials allegedly related to declassified U.S. military contracts. No ransom demand is explicitly stated in the post; the group's standard approach is to solicit payment for decryption software.
Data the group says was taken
AI dossier — extracted from the leak post- Declassified U.S. military contract documents
What the group claims
Micro-Comm DECLASSIFIED U.S. Military Contract
The leak post
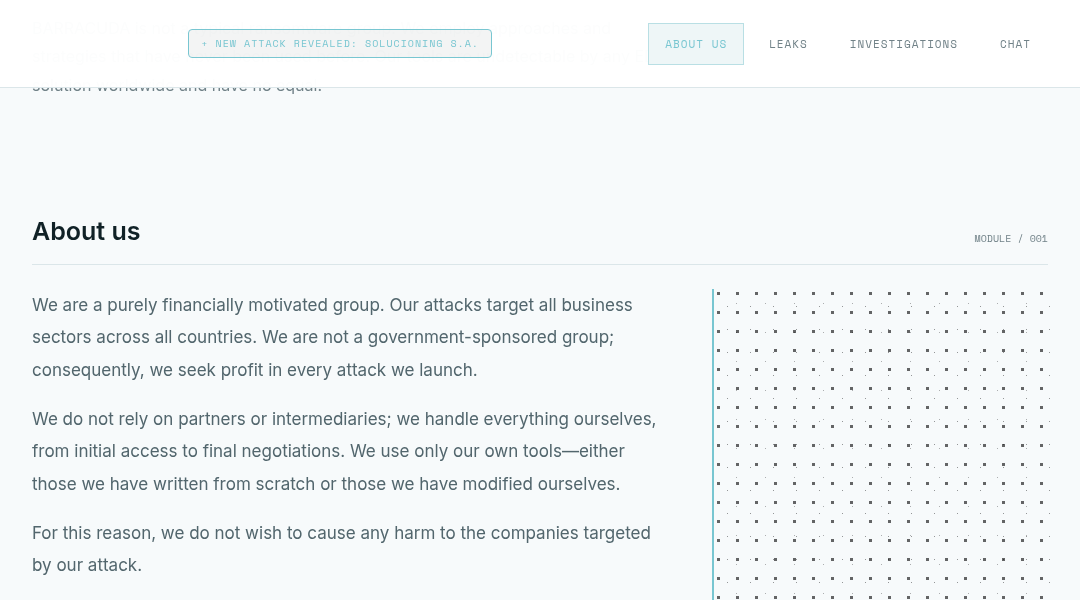
captured from the group's site[ VR Advogados: how the company facilitates fraud against the state? ](http://uvm6hk4wwstfddja5z5htgtlehmfyflffijz6iozsuqyacyibzxefkqd.onion/investigations?article=VR%20Advogados%3a%20how%20the%20company%20facilitates%20fraud%20against%20the%20state%3f) [ Micro-Comm DECLASSIFIED U.S. Military Contract ](http://uvm6hk4wwstfddja5z5htgtlehmfyflffijz6iozsuqyacyibzxefkqd.onion/investigations?article=Micro-Comm%20DECLASSIFIED%20U.S.%20Military%20Contract) INDEPENDENT OFFENSIVE SECURITY GROUP / 2026 BARRACUDA is not a typical ransomware group. We employ approaches and strategies that have never been used before. Our tools are undetectable by any EDR solution worldwide and have no equal. We are a purely financially motivated group. Our attacks target all business sectors across all countries. We are not a government-sponsored group; consequently, we seek profit in every attack we launch. We do not rely on partners or intermediaries; we handle everything ourselves, from initial access to final negotiations. We use only our own tools—either those we have written from scratch or those we have modified ourselves. For this reason, we do not wish to cause any harm to the companies targeted by ou…
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.