

Ransomware victim disclosure
← All victimsMid Atlantic Gynecologic Oncology and Pelvic Surgery Associates
Claimed by Netrunner · listed 4 hours ago
Status timeline
- ListedOct 8, 2026
- Data leakeddate unknown
At a glance
- Group
- Netrunner
- Status
- Data leaked
- Country
- United States
- Sector
- Healthcare
- Listed on leak site
- Oct 8, 2026
About the victim
AI dossier — public-source company profileMid Atlantic Gynecologic Oncology and Pelvic Surgery Associates (MAGOPSA) is a gynecologic oncology practice operating in the mid-Atlantic region, providing clinical services and procedures for patients with female reproductive health concerns.
- Industry
- Healthcare – Gynecologic Oncology
Attack summary
Severity: medium — Healthcare provider with likely access to patient medical records and PII; data published status confirmed, but no proof files listed yet and no specific data inventory disclosed. Sensitivity is inherent to the sector, but limited disclosure details prevent higher classification.The netrunner group claims to have compromised MAGOPSA and published their data. No specific details on encryption, exfiltration method, or data categories have been disclosed in the leak post.
What the group claims
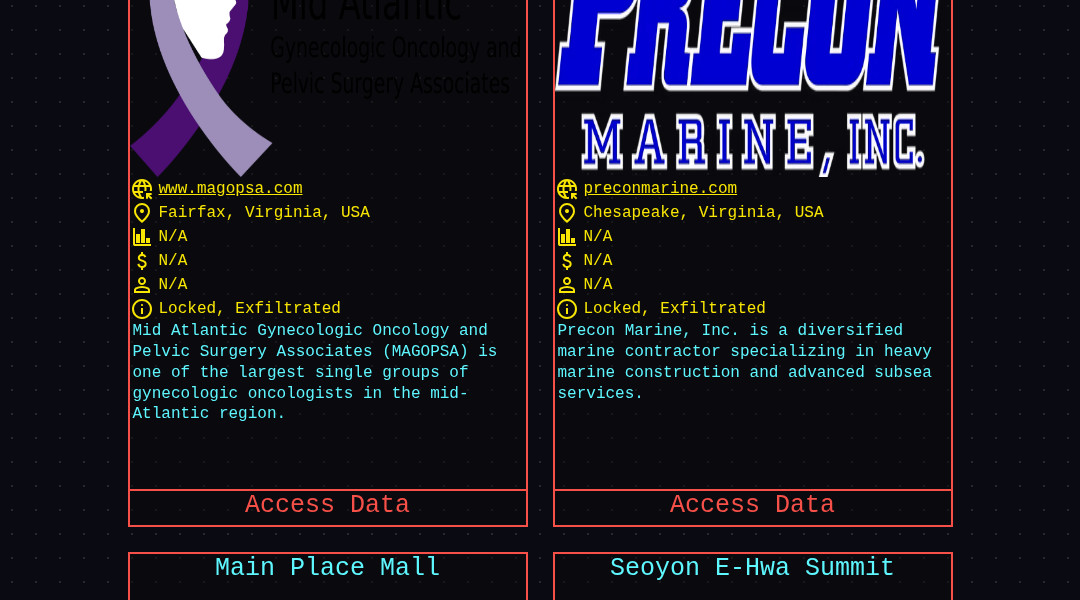
Mid Atlantic Gynecologic Oncology and Pelvic Surgery Associates (MAGOPSA) is one of the largest single groups of gynecologic oncologists in the mid-Atlantic region.
The leak post
captured from the group's siteMid Atlantic Gynecologic Oncology and Pelvic Surgery Associates Mid Atlantic Gynecologic Oncology and Pelvic Surgery Associates (MAGOPSA) is one of the largest single groups of gynecologic oncologists in the mid-Atlantic region, delivering a wide variety of clinical services and procedures to meet the needs of patients with health and medical concerns related to the female reproductive tract. Sample Files List Coming Soon
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.