

Ransomware victim disclosure

All victims

IT services company (web/software/payment/digital)

Claimed by VEXY · listed 4 hours ago

Today
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 18, 2026

Current state: Listed for ransom

At a glance

Group
VEXY
Status
Listed for ransom
Listed on leak site
Sep 18, 2026

About the victim

AI dossier — public-source company profile

The leak post lists multiple companies across different sectors (fashion, office equipment, cloud hosting, IT services, real estate, environmental services, food & beverage, adhesives) with no clear primary victim. The post does not establish a coherent single attack or target.

Industry
IT Services

Attack summary

Severity: low — No proof files, no attack description, no data exfiltration claimed, no operational impact stated. Post is merely a list of company profiles without evidence of breach or ransom demand.

The post does not describe any specific attack, encryption, exfiltration, or operational disruption. It appears to be a list of company descriptions without evidence of a breach or attack claim.

low

What the group claims

IT services company providing web design & development, software/application development, payment gateway services, digital marketing, mobile applications, software testing and cloud-related services.

The leak post

captured from the group's site
stpfashionlab.it is the website of STP Fashion Lab, a Tuscan company that has specialized in making Made in Italy womenswear for over twenty years. It produces the FRIVOLITÉ brand, founded in 2019, which targets independent, sensitive, and playful women.
Japanese company providing office equipment, IT equipment and services, office furniture, meeting/conferencing systems, and computer support.
Strad Solutions provides cloud hosting, dedicated servers, managed IT, cybersecurity, and disaster recovery services for businesses worldwide.
i2k2 Networks Pvt. Ltd., established in 1999, is a leading Indian provider of cloud computing, web hosting, managed IT, data center, backup, disaster recovery, and DevOps solutions. With 25+ years of experience, 4,000+ customers, Tier III-compliant data centers, and 24/7 support, i2k2 delivers secure, scalable, and reliable IT solutions worldwide.
Logar Network Solutions is a Brazilian managed IT services provider (MSP) that delivers outsourced IT management, cybersecurity, cloud infrastructure, backup and disaster recovery, software licensing, hardware lifecycle management, and custom software development. The company primarily serves medium-sized bus…

Screenshot of the leak post
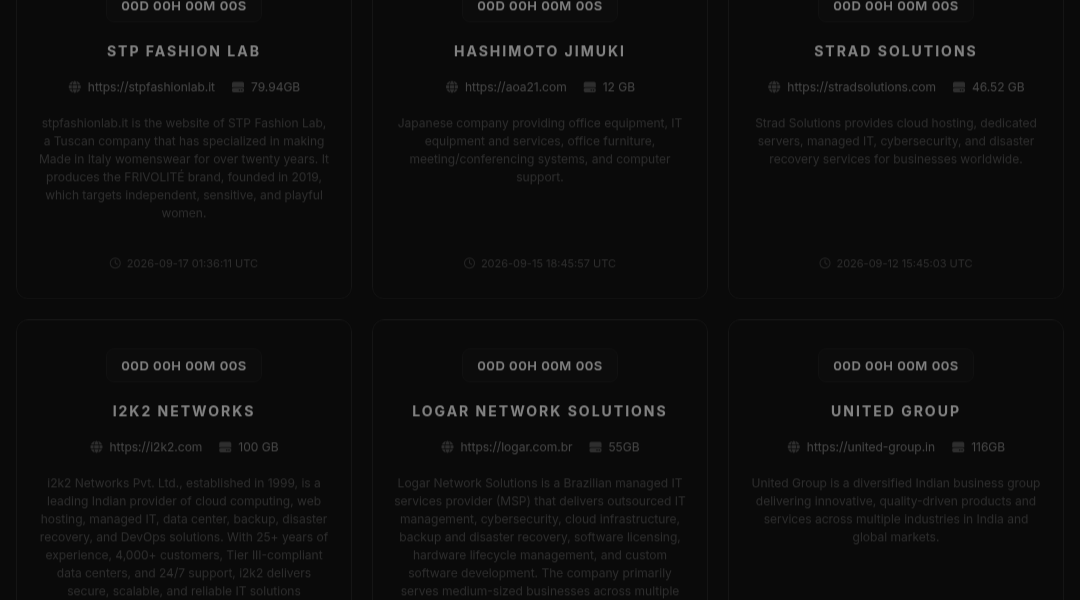
Leak screenshot for IT services company (web/software/payment/digital)

Sources

Source

Indexed 4 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About VEXY

VEXY is a ransomware group first observed in September 2026 with an apparent primary motivation of financial gain, though limited public documentation exists given its nascent operational history and small victim footprint. Based on available data, the group has claimed responsibility for attacks against two known victims, with targeting concentrated in Brazil and Ecuador, suggesting a regional focus on Latin American organizations. VEXY has demonstrated interest in the manufacturing and food and beverage sectors, industries that are frequently targeted due to their operational sensitivity and lower tolerance for downtime, which can increase the likelihood of ransom payment. No authoritative attribution regarding country of origin, RaaS affiliation, or technical tooling has been publicly documented by CISA, FBI, Mandiant, or other reputable threat intelligence sources at this time, and the group's attack methodology, encryption implementation, and extortion tactics remain uncharacterized in open-source reporting. Given its very recent emergence and limited victim count, VEXY should be considered an emerging and closely monitored threat, particularly for organizations operating in Latin American manufacturing and food production verticals, though its long-term operational capability and sustainability have yet to be established. The group has been linked to 19 public disclosures across our corpus. First observed on a leak site on September 4, 2026; most recent post September 18, 2026. The operation is currently active.

Timeline of this disclosure

  • September 18, 2026IT services company (web/software/payment/digital) listed by VEXY on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the IT Services sector.

If your organisation is affected

A listing by VEXY means IT services company (web/software/payment/digital) appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Monitor for the data appearing on VEXY's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.