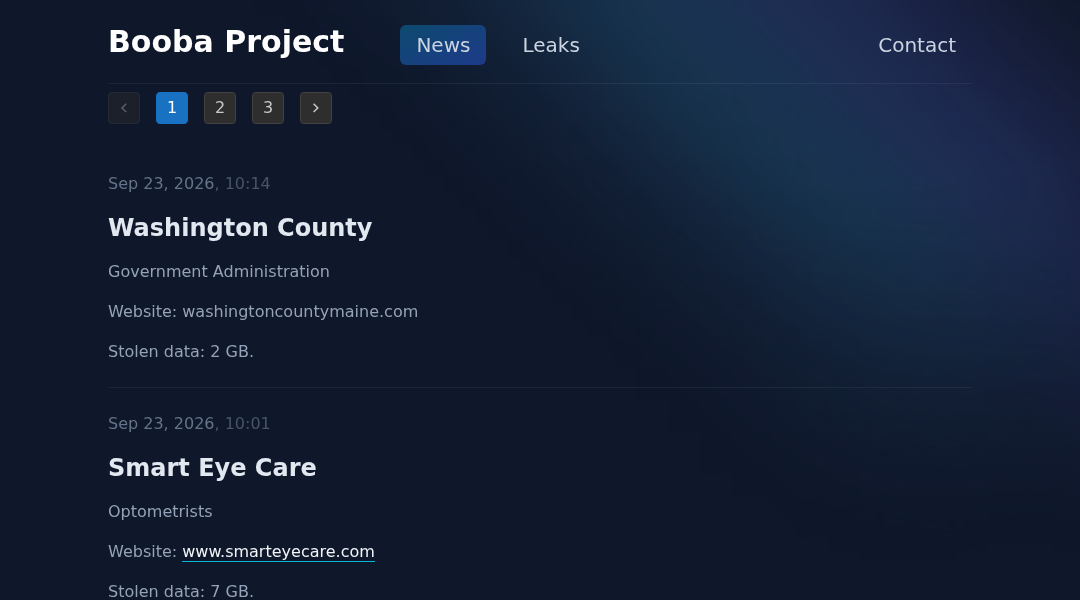
BOOBA is a ransomware group first observed in August 2026 with a primary financial motivation, though due to its extremely recent emergence and limited documented activity, comprehensive public intelligence on this group remains scarce across major threat intelligence sources including CISA, FBI, and Mandiant. Based on available data, the group has claimed or confirmed at least one known victim, with targeting concentrated in the Information Technology sector, suggesting a deliberate focus on technology organizations which may reflect an interest in maximizing leverage through access to sensitive technical data or downstream supply chain exposure. No verified attribution regarding country of origin, RaaS affiliation, or links to established threat actor groups has been publicly documented at this time, and specific details regarding initial access vectors, tooling, encryption methodology, or extortion tactics have not yet been formally reported by reputable security researchers. No notable high-profile campaigns, record ransom demands, or law enforcement actions involving BOOBA have been publicly recorded as of the time of this assessment. Given the group's August 2026 first-observed date and minimal victim count, BOOBA should be considered an emerging or nascent threat actor whose activity profile, capabilities, and operational scope remain largely uncharacterized pending further investigative reporting and intelligence collection. The group has been linked to 2 public disclosures across our corpus. First observed on a leak site on August 10, 2026; most recent post September 26, 2026. The operation is currently active.
If your organisation is affected
A listing by BOOBA means COSEF - Consorzio di Sviluppo Economico del Friuli appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.
- Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
- Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
- Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
- Report the incident to your national CERT, CSIRT Italia (Italy), as required for your jurisdiction.
- Monitor for the data appearing on BOOBA's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.
How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.