

Ransomware victim disclosure
← All victimsUnknown (SharePoint T1-T4 #1)
Claimed by HELIX · listed 2 hours ago
Status timeline
- ListedSep 25, 2026
Current state: Listed for ransom
At a glance
- Group
- HELIX
- Status
- Listed for ransom
- Listed on leak site
- Sep 25, 2026
About the victim
AI dossier — public-source company profileUnknown company. Victim identity obscured in leak post; only reference is 'SharePoint T1-T4 #1', indicating exfiltrated SharePoint libraries staged in tiered release format.
Attack summary
Severity: medium — Confirmed exfiltration of business data (SharePoint content) with published proof mechanism (tiered release countdown), but victim identity is completely unknown and data sensitivity cannot be assessed. No regulated data category is evident.HELIX claims exfiltration of SharePoint libraries from an unidentified victim. Data is staged in four tiers (T1–T4) with staggered public release on a countdown timer. No operational encryption or disruption is mentioned.
Data the group says was taken
AI dossier — extracted from the leak post- SharePoint libraries (tier-staged)
What the group claims
SharePoint libraries staged T1 (least) to T4 (most). Release countdown live on Helix. Tiers unlock by stage when each set timer reaches 0.
The leak post
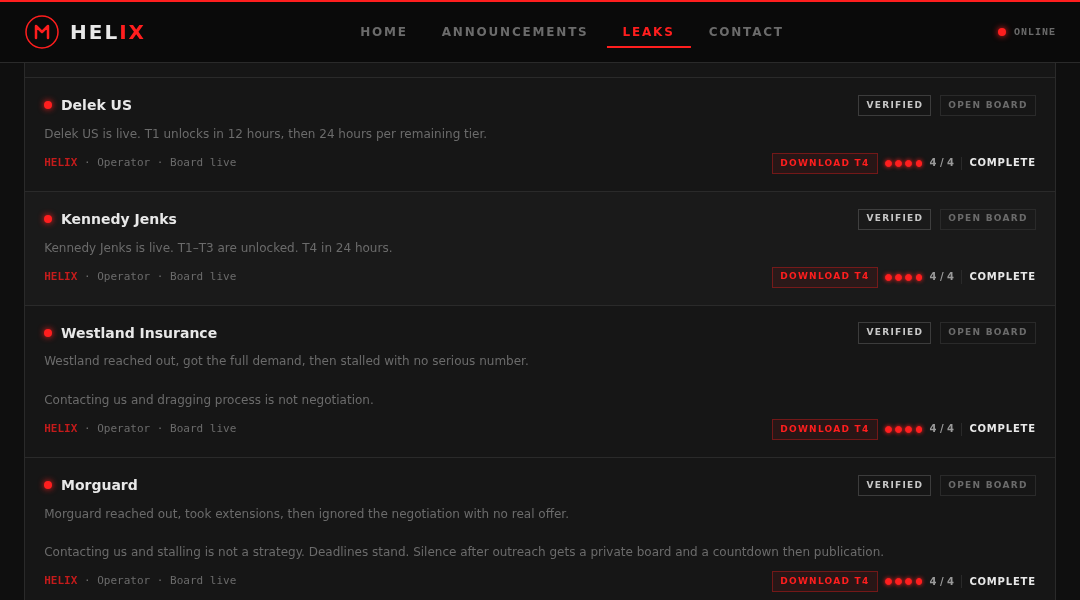
captured from the group's sitePublished feeds. Opening a feed leaves this page for the board. [ AmSpec is live. T1 unlocks on the current 24-hour cadence, then 24 hours per remaining tier. · Operator · Board live ](http://helixr2sncrd3ndsz5oho6mzqw3x5u7mvox5zcsngc5wm7v4l5k7oryd.onion/p/05d7e14bd3e7d7efce2406aad744dc6daa15edfbca7d38cb8ced622125d3c989) [ Delek US is live. T1 unlocks in 12 hours, then 24 hours per remaining tier. · Operator · Board live ](http://helixr2sncrd3ndsz5oho6mzqw3x5u7mvox5zcsngc5wm7v4l5k7oryd.onion/p/169f107db2a3ef002d03c665c3adf1f71560d1c5463ef35f720a9d5062f80d4b) [ Kennedy Jenks is live. T1–T3 are unlocked. T4 in 24 hours. · Operator · Board live ](http://helixr2sncrd3ndsz5oho6mzqw3x5u7mvox5zcsngc5wm7v4l5k7oryd.onion/p/1ba8b0df41a617631d09ae43a2bb4a5748b5b3f2b1cd007251bb3598a5ddcf44) [ Westland reached out, got the full demand, then stalled with no serious number. Contacting us and dragging process is not negotiation. · Operator · Board live ](http://helixr2sncrd3ndsz5oho6mzqw3x5u7mvox5zcsngc5wm7v4l5k7oryd.onion/p/380506d310d5417b836512938f95a302a7fb021fbe54b9f392da079aaf9ade1e) [ Morguard reached out, took extensions, then ignored the negotiation with no real offer. Contacting us and s…
Data the group says was taken
- SharePoint libraries
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.