

Ransomware victim disclosure
← All victimsShanghai Tunnel Engineering Co Ltd
Claimed by GLOBAL CYBERNETIC COLLECTIVE · listed 1 hour ago
Status timeline
- ListedSep 29, 2026
- Data leakeddate unknown
At a glance
- Status
- Data leaked
- Country
- China
- Listed on leak site
- Sep 29, 2026
About the victim
AI dossier — public-source company profileShanghai Tunnel Engineering Co Ltd (STECS) is a civil engineering and construction company specializing in rail transit and underground projects. The company is based in Shanghai's Xuhui District and has completed over 30 major projects for clients including the Land Transport Authority and Public Utilities Board.
- Industry
- Civil Engineering & Construction
- Address
- 1099 South Wanping Rd. Xuhui District, Shanghai 200232
Attack summary
Severity: low — Post contains only announcement and threat; no proof files, screenshots, or data samples are publicly available. Data custody is claimed as 'active' but no exfiltration details, data inventory, or operational impact is specified. Deadline has expired with no follow-through on disclosure.The leak post claims data exfiltration from Shanghai Tunnel Engineering Co Ltd. The operator states files are pending disclosure and available upon ticket request, but no public dump is currently available and no specific data categories are detailed in the post.
What the group claims
Leading civil engineering and construction company specializing in rail transit and underground projects in Singapore. Has completed over 30 major projects for clients like the Land Transport Authority and Public Utilities Board. Prioritizes safety, environmental responsibility, and improving urban infrastructure in Southeast Asia.
The leak post
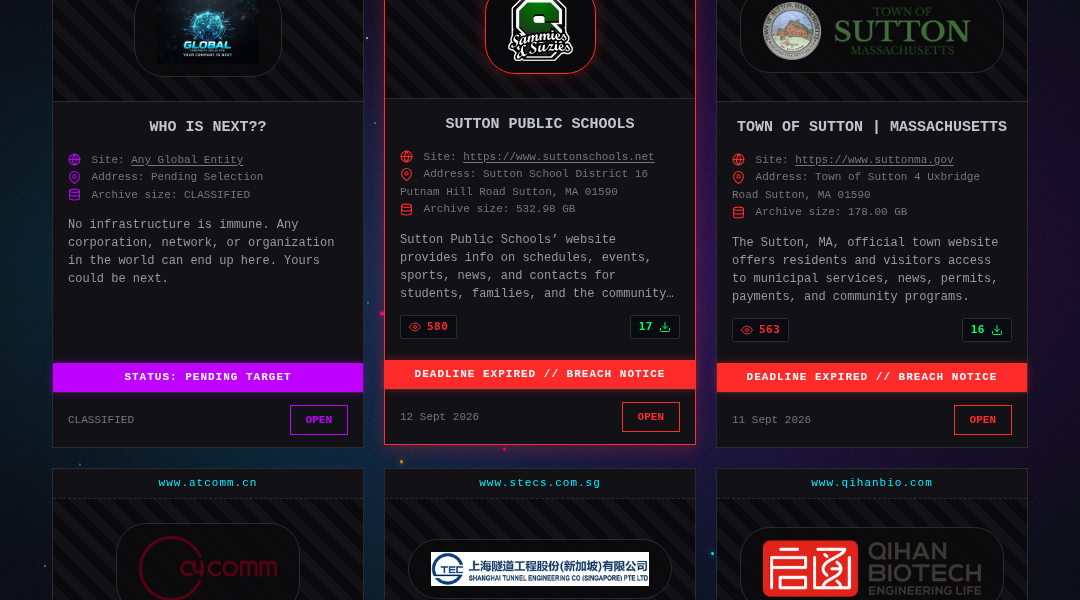
captured from the group's siteSystem Status: • Security: • Protocol: • Integrity: No infrastructure is immune. Any corporation, network, or organization in the world can end up here. Yours could be next. No system is untouchable. Any organization, corporate infrastructure, or commercial entity in the world can become the subject of the next publication. Prepare your security posture or expect exposure. > CONNECTING TO STORAGE NODE... > ARCHIVE UNDER ENCRYPTION // PENDING DISCLOSUREDATA CUSTODY ACTIVE // NO PUBLIC DUMP AVAILABLE YET [[ REQUEST FULL ARCHIVE VIA TICKET ]](http://globalrbweyhxxa5b65bjjsm5bfuqfs5ydizefupqcminoedzn6o2sqd.onion/#modal-ticket) Sutton Public Schools’ website provides info on schedules, events, sports, news, and contacts for students, families, and the community in Sutton, MA. DEADLINE EXPIRED // BREACH NOTICE A SOON RELEASE IS EXPECTED // THE FILES WILL BE AVAILABLE FOR DOWNLOAD SOON. Sutton School District 16 Putnam Hill Road Sutton, MA 01590 The Sutton Public Schools website (Sutton, MA) is the key resource for the local school district, serving students, families, and the community. It offers an academic calendar with holidays, early dismissals, and open house events, plus spor…
Screenshot of the leak post
Sources
Source
Indexed 1 hour agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.