

Ransomware victim disclosure
← All victimsUnknown Company ($3.3M demand)
Claimed by Cl0p · listed 2 hours ago
Status timeline
- ListedSep 20, 2026
- Data leakeddate unknown
At a glance
- Group
- Cl0p
- Status
- Data leaked
- Listed on leak site
- Sep 20, 2026
About the victim
AI dossier — public-source company profileUnknown company. The leak post contains generic placeholder language ('The Company') repeated throughout, with no identifying details provided. The victim name itself is a generic descriptor with only a claimed demand figure.
Attack summary
Severity: critical — Confirmed exfiltration of PII and PHI at massive scale (hundreds of millions of records, 12.9M Salesforce records); sensitive infrastructure blueprints, security documentation, and active credentials exposed; operational disruption claimed. The combination of regulated data classes, scale, and infrastructure/security artifact exposure meets critical threshold.Cl0p claims exfiltration of hundreds of millions of records spanning PII and PHI, along with 12.9 million Salesforce records, 645 GB of SharePoint data, and sensitive infrastructure documentation. The group also claims encryption/operational disruption. A $13 million ransom demand is stated in the post.
Data the group says was taken
AI dossier — extracted from the leak post- 12.9 million Salesforce records
- PII (Personally Identifiable Information)
- PHI (Protected Health Information)
- 645 GB SharePoint internal corporate data
- 182,000+ customer contact records
- 8,300+ employee records (name, email, title, phone)
- Executed contracts, MSAs, NDAs, leases, SOWs
- Physical key inventory logs and contractor audits
- Data center drawings, floor plans, electrical diagrams, security schematics
- CERM (Critical Environment Reliability Management) process library
- Physical and information security policies
- Security scorecards and performance packages
- Credential and access control artifacts (PasswordList.xlsx, Okta SSO access lists, badge reports, access control forms)
What the group claims
Customer data, employee data, and other internal corporate data was compromised. The company engaged but made paltry offers and did not negotiate adequately.
The leak post
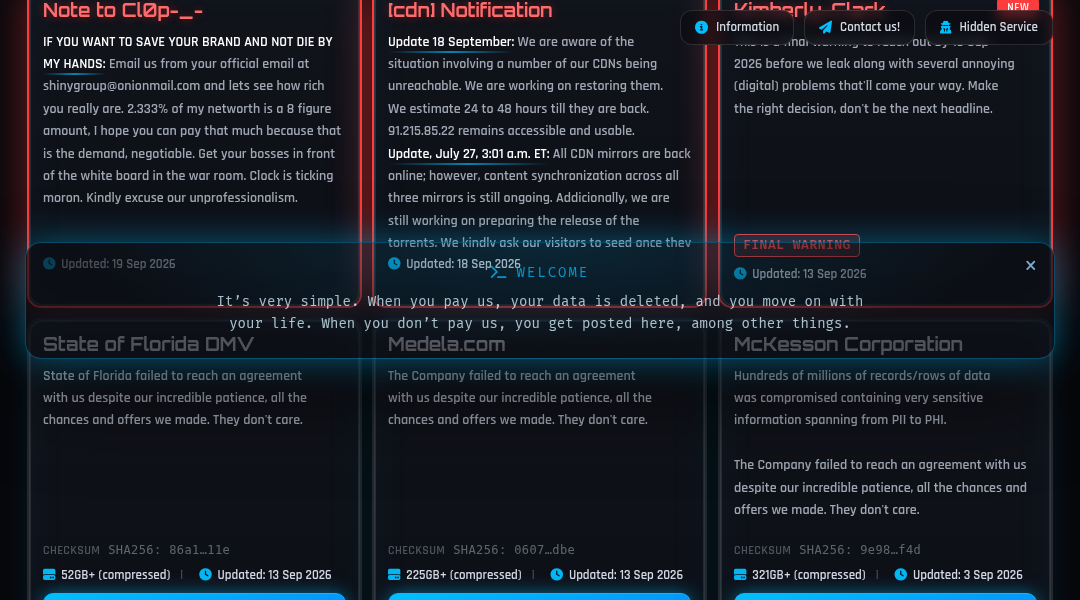
captured from the group's site**IF YOU WANT TO SAVE YOUR BRAND AND NOT DIE BY MY HANDS:** Email us from your official email at [email protected] and lets see how rich you really are. 2.333% of my networth is a 8 figure amount, I hope you can pay that much because that is the demand, negotiable. Get your bosses in front of the white board in the war room. Clock is ticking moron. Kindly excuse our unprofessionalism. We are aware of the situation involving a number of our CDNs being unreachable. We are working on restoring them. We estimate 24 to 48 hours till they are back. 91.215.85.22 remains accessible and usable. **Update, July 27, 3:01 a.m. ET:** All CDN mirrors are back online; however, content synchronization across all three mirrors is still ongoing. Addicionally, we are still working on preparing the release of the torrents. We kindly ask our visitors to seed once they become available. A notification will be posted upon release. All CDN mirrors are currently experiencing a service disruption. **All files are fully backed up and no data has been lost.** At this time we do not have an estimated time of resolution.We are working to restore service promptly and will share updates as they become avail…
Data the group says was taken
- customer data
- employee data
- internal corporate data
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.