

Ransomware victim disclosure
← All victimsHyvision System Inc
Claimed by METAENCRYPTER · listed 4 hours ago
Status timeline
- ListedSep 22, 2026
Current state: Listed for ransom
At a glance
- Group
- METAENCRYPTER
- Status
- Listed for ransom
- Country
- South Korea
- Listed on leak site
- Sep 22, 2026
- Data size
- 1 TB
About the victim
AI dossier — public-source company profileHyvision System Inc is a South Korea-based manufacturer of automatic test and measurement equipment for mobile camera modules. The company produces testing and measuring systems for camera modules, CCM testers, smart component testers, vision inspector testers, secondary batteries, and smart components.
- Industry
- Electronics Manufacturing & Test Equipment
Attack summary
Severity: high — Confirmed exfiltration of 2 TB of internal data from a manufacturing company with disclosed proof manifest and threat of public release; operational impact and data sensitivity unknown but scale and group intent indicate significant business risk.METAENCRYPTER claims to have exfiltrated approximately 2 TB of internal data from Hyvision System Inc. The group states they have disclosed a complete manifest of exfiltrated files with representative samples, and threaten to release the full volume to the public and notify data protection authorities if the company does not negotiate before a stated deadline.
Data the group says was taken
AI dossier — extracted from the leak post- internal company files
- business data
- technical documentation
What the group claims
A Korea-based company principally engaged in the manufacture of automatic test and measurement equipment for mobile camera modules. Its products include testing and measuring system for camera modules, ccm tester, smart comp. tester, vision inspector tester, secondary batteries, and smart components.
The leak post
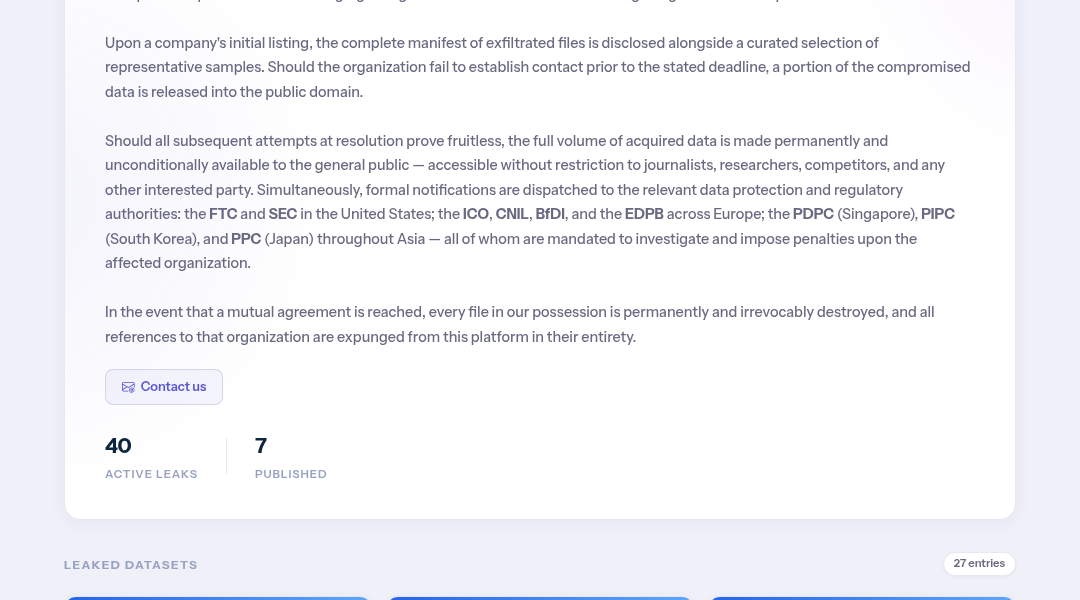
captured from the group's siteThis platform publishes data belonging to organizations that have elected to forgo negotiation entirely.Upon a company's initial listing, the complete manifest of exfiltrated files is disclosed alongside a curated selection of representative samples. Should the organization fail to establish contact prior to the stated deadline, a portion of the compromised data is released into the public domain.Should all subsequent attempts at resolution prove fruitless, the full volume of acquired data is made permanently and unconditionally available to the general public — accessible without restriction to journalists, researchers, competitors, and any other interested party. Simultaneously, formal notifications are dispatched to the relevant data protection and regulatory authorities: the and in the United States; the , , , and the across Europe; the (Singapore), (South Korea), and (Japan) throughout Asia — all of whom are mandated to investigate and impose penalties upon the affected organization.In the event that a mutual agreement is reached, every file in our possession is permanently and irrevocably destroyed, and all references to that organization are expunged from this platform in th…
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.