

Ransomware victim disclosure
← All victimsNavitrans
Claimed by Emperador · listed 3 days ago
Status timeline
- ListedSep 13, 2026
- Data leakeddate unknown
At a glance
- Group
- Emperador
- Status
- Data leaked
- Sector
- Transportation
- Listed on leak site
- Sep 13, 2026
- Data size
- 600 MB
- Records
- 17000 files
About the victim
AI dossier — public-source company profileNavitrans is a Colombian distributor and service provider specializing in commercial trucks and heavy machinery. The company operates a nationwide network of workshops providing vehicle sales, spare parts distribution, and maintenance and repair services.
- Industry
- Commercial Vehicles & Heavy Machinery Distribution
Attack summary
Severity: medium — Confirmed exfiltration of business-sensitive data (pricing, financing) at moderate scale (223.2 MB) with no indication of regulated PII or critical infrastructure disruption. No proof files explicitly advertised.The emperor group claims to have exfiltrated sensitive operational data from Navitrans, including pricing information, financing details, and other confidential business records totaling 223.2 MB.
Data the group says was taken
AI dossier — extracted from the leak post- pricing information
- financing details
- operational data
What the group claims
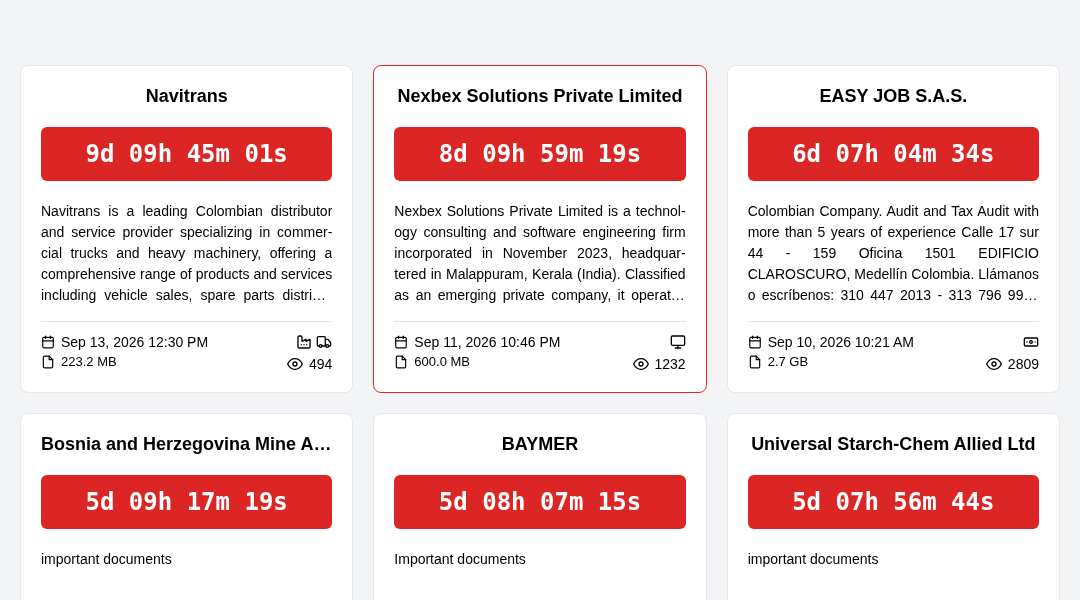
Navitrans is a leading Colombian distributor and service provider specializing in commercial trucks and heavy machinery, offering a comprehensive range of products and services including vehicle sales, spare parts distribution, and maintenance and repair services through a nationwide network of workshops. This post includes sensitive data about prices, financing, and other operational information. [Size: 223.2 MB | Sector: Manufacturing, Transportation]
The leak post
captured from the group's site[ Navitrans is a leading Colombian distributor and service provider specializing in commercial trucks and heavy machinery, offering a comprehensive range of products and services including vehicle sales, spare parts distribution, and maintenance and repair services through a nationwide network of workshops. This post includes sensitive data about prices, financing, and other operational information. ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/navitrans/) [ Nexbex Solutions Private Limited is a technology consulting and software engineering firm incorporated in November 2023, headquartered in Malappuram, Kerala (India). Classified as an emerging private company, it operates with a paid-up capital of 10 million Indian rupees (₹10 Lakhs) and a compact team, generating estimated annual revenue of less than $1.2 million USD. Its core business focuses on computer programming, custom mobile application development (such as its corporate loyalty platforms Nexi Paints and Grace Petroleum), and digital solutions for retail automation, e-commerce, and smart lead management for growing small and medium-sized enterprises. We have access to all their databases wi…
Screenshot of the leak post
Sources
- Leak post/post/navitrans/
Source
Indexed 3 days agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.