

Ransomware victim disclosure
← All victimsColombian Audit and Tax Audit Company
Claimed by Emperador · listed 2 hours ago
Status timeline
- ListedSep 21, 2026
- Data leakeddate unknown
At a glance
About the victim
AI dossier — public-source company profileA Colombian audit and tax audit firm based in Medellín with more than 5 years of operating experience. The company provides auditing and tax services to clients.
- Industry
- Professional Services / Auditing
- Address
- Calle 17 sur 44 - 159 Oficina 1501 EDIFICIO CLAROSCURO, Medellín, Colombia
Attack summary
Severity: high — Confirmed exfiltration of employee and customer PII at scale, combined with sensitive tax and financial documents. Multiple regulated data types typical of audit firms create significant regulatory and personal privacy exposure.The emperor group claims to have exfiltrated personal data of employees and customers, tax documents, databases, and other company documents. The post advertises 17,000 documents as proof of the breach.
Data the group says was taken
AI dossier — extracted from the leak post- employee personal data
- customer personal data
- tax documents
- databases
- company documents
The group's post references roughly 17000 documents proof files.
What the group claims
Colombian company specializing in Audit and Tax Audit with more than 5 years of experience, located at Calle 17 sur 44 - 159 Oficina 1501 Edificio Claroscuro, Medellín, Colombia.
The leak post
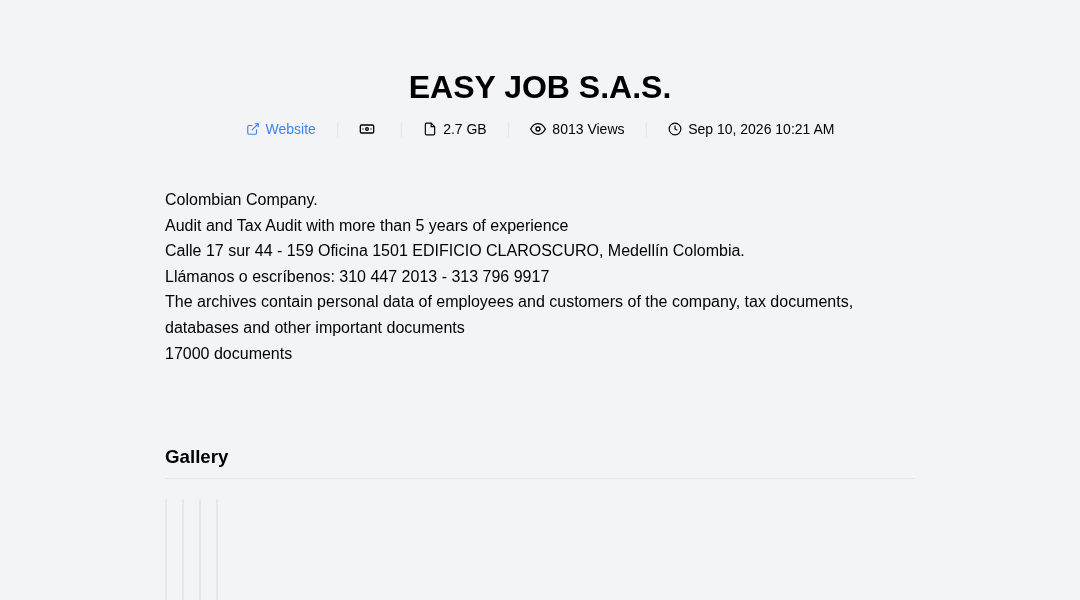
captured from the group's siteColombian Company.Audit and Tax Audit with more than 5 years of experienceCalle 17 sur 44 - 159 Oficina 1501 EDIFICIO CLAROSCURO, Medellín Colombia.Llámanos o escríbenos: 310 447 2013 - 313 796 9917The archives contain personal data of employees and customers of the company, tax documents, databases and other important documents17000 documents
Data the group says was taken
- personal data of employees
- personal data of customers
- tax documents
- databases
- other important documents
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.