

Ransomware victim disclosure
← All victimsMetrocolor SA
Claimed by Emperador · listed 4 hours ago
Status timeline
- ListedOct 13, 2026
Current state: Listed for ransom
At a glance
- Group
- Emperador
- Status
- Listed for ransom
- Country
- Peru
- Sector
- Printing / Publishing
- Listed on leak site
- Oct 13, 2026
- Records
- several thousand documents
About the victim
AI dossier — public-source company profileMetrocolor SA is a Peruvian commercial printing company that produces packaging, labels, boxes, books, magazines, booklets, and promotional products. The company maintains personnel and customer records as part of its business operations.
- Industry
- Printing & Packaging
Attack summary
Severity: medium — Confirmed exfiltration of personnel and customer data at moderate scale ('several thousand documents'). No proof files advertised, no encryption disruption mentioned, and no ransom demand publicly stated for this specific victim, though the group demonstrates capability across multiple targets.The emperador group claims to have exfiltrated several thousand documents containing personnel and customer data from Metrocolor SA. No encryption activity is stated, and no ransom demand is specified for this victim.
Data the group says was taken
AI dossier — extracted from the leak post- Personnel records
- Customer data
- Commercial documents
What the group claims
A Peruvian company from the printing industry. Commercial printing, packaging, labels, boxes, books, magazines, booklets and promotional products.
The leak post
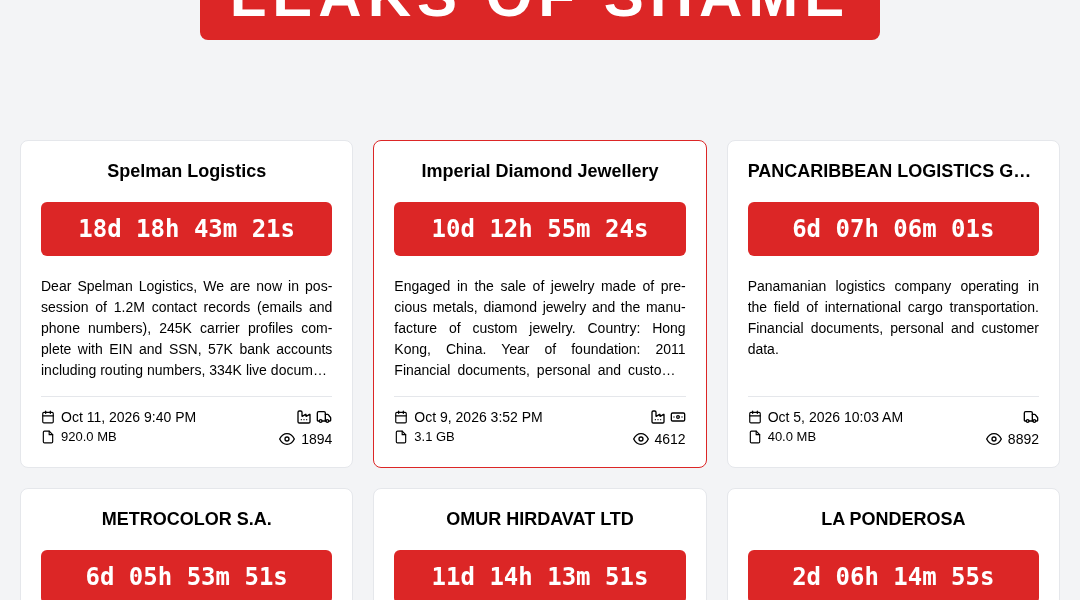
captured from the group's site[ Dear Spelman Logistics, We are now in possession of 1.2M contact records (emails and phone numbers), 245K carrier profiles complete with EIN and SSN, 57K bank accounts including routing numbers, 334K live document URLs, and 4.5M carrier registry entries pulled from your MVMNT TMS. Your exposure extends well beyond your own walls. We have also reached into the systems of your partners, including: ALG Canada Inc Line Transportation Inc Maverick Acquisition Ventures Inc Reliable Freight Solutions Rhode Sense and more. If you would rather not have us contact your partners and make life difficult for your employees, we suggest you pay the following: $500,000 in BTC or XMR. You will shortly receive an email explaining how to reach us. If that fails, contact us at: Email: [email protected] / [email protected] Session: 05651c7323273b723588d47455471ee9e27feb5187a30f2933554a705aacb38358 ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/spelman-logistics/) [ Engaged in the sale of jewelry made of precious metals, diamond jewelry and the manufacture of custom jewelry. Country: Hong Kong, China. Year of foundation: 2011 Financial documents, personal and customer…
Data the group says was taken
- personnel data
- customer data
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.