

Ransomware victim disclosure
← All victimsUnknown US County/Government Entity
Claimed by Rhysida · listed 2 hours ago
Status timeline
- ListedSep 17, 2026
Current state: Listed for ransom
At a glance
- Group
- Rhysida
- Status
- Listed for ransom
- Country
- United States
- Listed on leak site
- Sep 17, 2026
- Data size
- 2.6 TB
- Records
- 814,500 files
About the victim
AI dossier — public-source company profileThe victim_name 'Unknown US County/Government Entity' represents a US county government organization. The leak post contains multiple distinct victim datasets, suggesting this entry conflates multiple attacks or a single multi-target operation. The primary victim appears to be a US county with health and social services functions.
- Industry
- Government / Public Health
Attack summary
Severity: critical — Confirmed exfiltration of large-scale regulated PII and health data from US county government, including 42 CFR Part 2 protected substance-abuse treatment records, SSNs, medical records, and law-enforcement intelligence files. This represents multiple categories of federally protected information and impacts critical government/health functions.Rhysida claims to have exfiltrated 814,500 files (2.6 TB) from a US county government entity. The group asserts capture of highly sensitive data including patient health information (PHI) from medical assistance and methadone clinics, background checks with full SSNs, medical faxes with diagnoses, confidential 42 CFR Part 2 records, county payroll with salaries, and jail gang-intelligence files. The post indicates the group is attempting to sell the data exclusively to a single buyer.
Data the group says was taken
AI dossier — extracted from the leak post- Background-check dossiers with full SSNs
- Medical faxes with patient names and diagnoses (2022–2026)
- Methadone clinic records (42 CFR Part 2)
- Medical-assistance files with driver licenses, Green Cards, SSN cards, tax forms
- County payroll registers with salaries and HR records
- Jail gang-intelligence and gang-member master list
- Patient health information (PHI)
The group's post references roughly 814500 proof files.
What the group claims
A US county entity with medical, social services, and law enforcement data including methadone clinic records, background checks, and jail gang-intelligence files.
The leak post
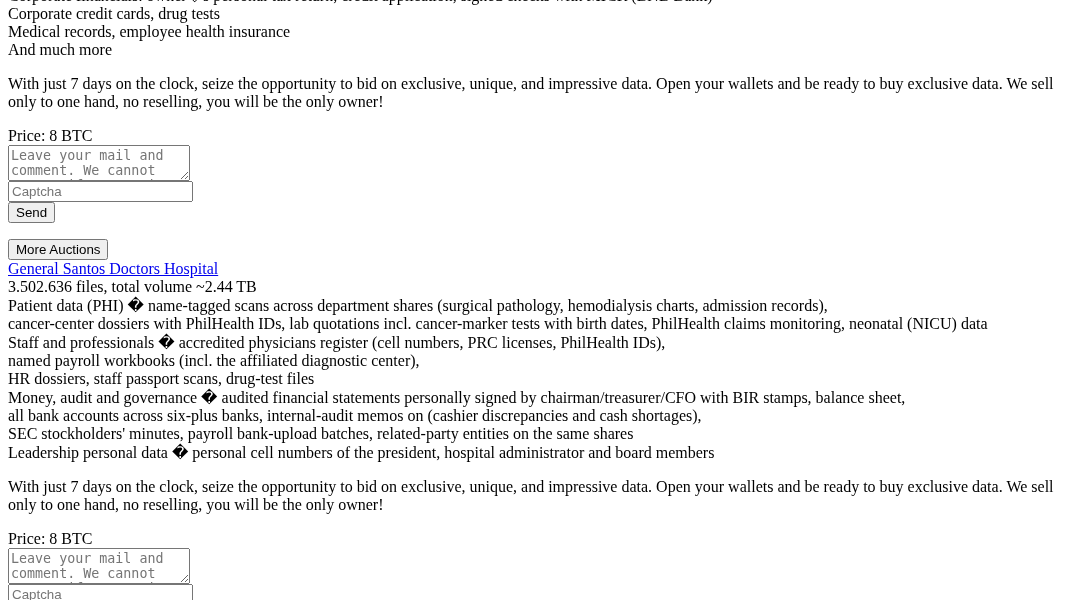
captured from the group's siteAxdia International is a German electronics company that brings together a wide range of modern small electronics and electric mobility products. With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! Owner�s documents: employee evaluations, salary rates, bonuses, job offers, family documentsCFO�s documents: client credit reports, bankruptcy records, tax documents, father�s medical records (guardianship court case)Corporate financials: owner�s personal tax return, credit application, signed checks with MICR (BNB Bank)Corporate credit cards, drug testsMedical records, employee health insuranceAnd much more With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! 3.502.636 files, total volume ~2.44 TBPatient data (PHI) � name-tagged scans across department shares (surgical pathology, hemodialysis charts, admission records), cancer-center dossiers with …
Data the group says was taken
- background-check dossiers with SSNs
- medical faxes
- methadone clinic records (42 CFR Part 2)
- medical-assistance files
- driver licenses
- Green Cards
- SSN cards
- tax forms
- bank data
- county payroll registers
- HR memos
- contracts
- pension records
- discipline databases
- jail gang-intelligence files
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.