

Ransomware victim disclosure

← All victims

Studio di Consulenza (Italian)

Claimed by MS13-089 · listed 59 minutes ago

Today
Age
since listed · listed for ransom

Status timeline

  1. ListedOct 2, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Country
Italy
Listed on leak site
Oct 2, 2026

About the victim

AI dossier — public-source company profile

Studio di Consulenza is an Italian consulting firm specializing in accounting, tax declarations, statutory audits, and corporate restructuring advisory. The firm provides comprehensive financial and legal consulting services to business clients.

Industry
Financial / Accounting / Legal Consulting

Attack summary

Severity: low — The post contains no proof files, screenshots, or operational impact claims. The listing is incoherent and provides no evidence of actual data exfiltration or encryption. Only an announcement with fragmentary service descriptions.

The group claims to have compromised Studio di Consulenza but provides no details of what data was exfiltrated or what operational disruption occurred. The leak post is incoherent, mixing descriptions of unrelated companies (maritime operations, disability services, urology practice) with fragments about the target firm's accounting and tax services.

low

Data the group says was taken

AI dossier — extracted from the leak post
  • Accounting records
  • Tax documentation
  • Audit files
  • Corporate restructuring data

What the group claims

Aree di specializzazione: contabilità, bilanci, dichiarazioni fiscali, incarichi di sindaco e revisore legale, consulente tecnico d'ufficio, ristrutturazioni e operazioni straordinarie. Consulenza Societaria, ordinaria e straordinaria.

The leak post

captured from the group's site
Empresa con más de 25 años de experiencia en el rubro marítimo, orientada a ejecutar operaciones con estándares de calidad, control de riesgo y tiempos de respuesta consistentes... 
At Brittany Residential, Inc., we believe in creating a world where individuals with developmental disabilities are supported, valued, and empowered to live fulfilling lives. Our dedicated team provides compassionate, person-centered care that...
Virginia Urology (VU) has a long history of providing quality care to the Greater Richmond metro area since 1929. This practice prides itself on its strong commitment to the community’s urological needs by recruiting highly... 
Aree di specializzazione: contabilità, bilanci, dichiarazioni fiscali, incarichi di sindaco e revisore legale, consulente tecnico d’ufficio, ristrutturazioni e operazioni straordinarie. Consulenza Societaria, ordinaria e straordinaria, ivi...

Screenshot of the leak post
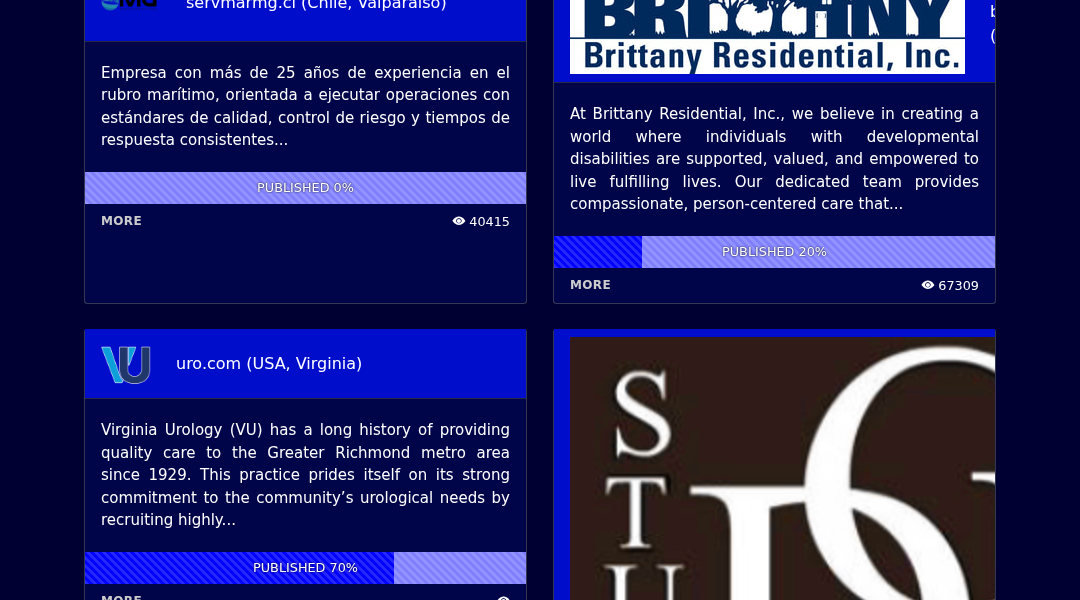
Leak screenshot for Studio di Consulenza (Italian)

Sources

Source

Indexed 59 minutes ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About MS13-089

MS13-089 is a ransomware group first observed in May 2026 with an apparent financial motivation, though its limited documented activity makes comprehensive attribution difficult at this time. Based on available data, the group has claimed or been linked to a single known victim, with targeting focused on the United States and specifically the Healthcare and Social Services sector, a pattern consistent with threat actors who deliberately select high-pressure targets likely to pay ransoms quickly to restore critical operations. No public reporting from CISA, the FBI, Mandiant, or other established threat intelligence sources has yet documented the group's specific initial access vectors, tooling, encryption methods, or affiliation with known ransomware ecosystems, and it remains unclear whether MS13-089 operates as a Ransomware-as-a-Service platform or as an independent closed group. Given its extremely recent emergence and minimal victim footprint at the time of this writing, MS13-089 should be considered an emerging and under-documented threat, and the Healthcare sector in particular should monitor for indicators of compromise as the group's tactics, techniques, and procedures become more clearly defined through ongoing incident investigations and threat intelligence collection. Current status remains active based on first observation date, though the full scope of its operations has yet to be established in open-source reporting. The group has been linked to 22 public disclosures across our corpus. First observed on a leak site on May 14, 2026; most recent post October 2, 2026. The operation is currently active.

Timeline of this disclosure

  • October 2, 2026Studio di Consulenza (Italian) listed by MS13-089 on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the Financial / Accounting / Legal sector. Geographically, Studio di Consulenza (Italian) is reported in Italy, a country with 203 ransomware disclosures in our corpus.

If your organisation is affected

A listing by MS13-089 means Studio di Consulenza (Italian) appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CSIRT Italia (Italy), as required for your jurisdiction.
  • Monitor for the data appearing on MS13-089's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.

Studio di Consulenza (Italian) data breach — MS13-089 ransomware attack (2026) · Darkfield