

Ransomware victim disclosure

All victims

Unknown Moving and Logistics Company

Claimed by Dark Project · listed 1 hour ago

27000
Records
Today
Age
since listed · data leaked

Status timeline

  1. ListedSep 16, 2026
  2. Data leakeddate unknown

At a glance

Status
Data leaked
Listed on leak site
Sep 16, 2026
Records
27000

About the victim

AI dossier — public-source company profile

A moving and logistics company offering local, long-distance, and international moving services, lab relocation, and logistics solutions to residential and commercial clients.

Industry
Transportation & Logistics

Attack summary

Severity: high — Confirmed exfiltration of employee PII and financial records at scale (27,000 files), combined with operational disruption from encryption. No ransom demand explicitly stated in post.

Dark Project claims to have exfiltrated approximately 27,000 internal files and encrypted the company's systems. Stolen data includes financial records, internal working materials, and employee personal data.

high

Data the group says was taken

AI dossier — extracted from the leak post
  • financial records
  • internal working materials
  • employee personal data

What the group claims

A moving and logistics company offering local, long distance, and international moving, lab relocation services, and logistics solutions to both residential and commercial customers. Suffered a cyberattack resulting in theft of approximately 27,000 internal files and encryption of company systems.

The leak post

captured from the group's site
A company has suffered a major cyberattack resulting in the theft of approximately 27,000 internal files. The leaked documents include financial records, internal working materials, and personal data of employees. Attackers encrypted the company's systems following the breach, severely disrupting operations
Companys offerings include local, long distance, and international moving, lab relocation services, and logistics solutions. They cater to a diverse range of clients, providing professional and comprehensive assistance to both residential and commercial customers.
Investigators are working to identify the perpetrators and assess the full scope of the damage.
A company has suffered a major cyberattack resulting in the theft of approximately 27,000 internal files. The leaked documents include financial records, internal working materials, and personal data of employees. Attackers encrypted the company's systems following the breach, severely disrupting operations
If you’re a journalist, blogger, or have access to corporate networks, we’d love to connect with you. For any inquiries or if you encounter issues with our website, feel free to reach out at the email provided.

Data the group says was taken

  • financial records
  • internal working materials
  • employee personal data

Screenshot of the leak post
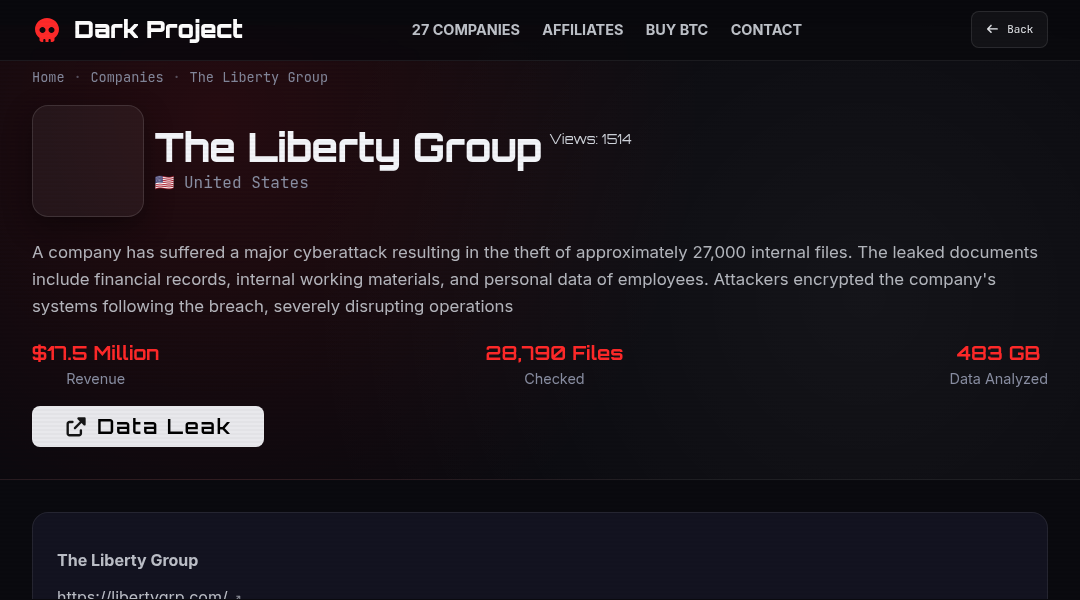
Leak screenshot for Unknown Moving and Logistics Company

Sources

Source

Indexed 1 hour ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Dark Project

Dark Project is a ransomware group first observed in August 2026 with an apparent primary motivation of financial gain, based on its targeting profile and operational patterns consistent with other profit-driven ransomware actors. As of the time of this writing, no major cybersecurity organizations including CISA, the FBI, Mandiant, or other reputable threat intelligence firms have published detailed public reporting attributing Dark Project to a specific nation-state, threat actor cluster, or affiliated ransomware ecosystem, and it remains unclear whether the group operates as a Ransomware-as-a-Service platform or as an independent closed operation. Based on available victim telemetry, the group has claimed at least 18 known victims across a geographically diverse range of countries, with the United States, United Kingdom, Mexico, the Philippines, and Germany representing its most frequently targeted regions. Its sectoral focus spans manufacturing, healthcare, transportation, hospitality, and education, suggesting an opportunistic targeting methodology rather than a narrowly defined strategic focus, though the inclusion of healthcare and critical infrastructure-adjacent sectors such as transportation warrants continued monitoring. Due to the group's recent emergence and limited public documentation at this time, specific details regarding initial access vectors, encryption implementation, extortion tactics, and tooling remain unconfirmed by open-source intelligence sources, and analysts should treat any further claims with appropriate caution pending corroborating reporting from authoritative sources. Dark Project should be considered an emerging threat actor under active observation. The group has been linked to 39 public disclosures across our corpus. First observed on a leak site on August 5, 2026; most recent post September 16, 2026. The operation is currently active.

Timeline of this disclosure

  • September 16, 2026Unknown Moving and Logistics Company listed by Dark Project on the group's public leak site
Records
27000

Sector and geography

This disclosure adds to ransomware activity in the Transportation & Logistics sector, which has 180 disclosures indexed across all operators we track.

If your organisation is affected

A listing by Dark Project means Unknown Moving and Logistics Company appeared on a ransomware extortion site and data attributed to it has been published. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Monitor for the data appearing on Dark Project's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.