

Ransomware victim disclosure

← All victims

Aeroklas

Claimed by Deadlock · listed 4 hours ago

27 GB
Data size
186207 files records
Today
Age
since listed · listed for ransom

Status timeline

  1. ListedOct 14, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Country
Thailand
Listed on leak site
Oct 14, 2026
Data size
27 GB
Records
186207 files

About the victim

AI dossier — public-source company profile

Aeroklas is a global automotive accessory manufacturer formed as a strategic joint venture between Duys Engineering Group (founded South Africa, 1960) and Aeroklas, owned by Eastern Polymer Group of Thailand. The company specializes in automotive components and accessories.

Industry
Automotive Manufacturing & Accessories

Attack summary

Severity: medium — 27 GB of data exfiltrated with indication of employee/personal records at risk, but the leak post is extremely confused and conflates many unrelated organizations, making verification of what was actually taken from Aeroklas impossible. No specific proof files shown for Aeroklas victim.

Deadlock claims to have exfiltrated 27 GB of data from Aeroklas. The leak post conflates multiple unrelated companies (pharmaceutical, machine vision, construction, law firm, etc.), making the specific attack claims against Aeroklas unclear, though the post references 186,207 files including personal and financial records.

medium

Data the group says was taken

AI dossier — extracted from the leak post
  • Business and operational files
  • Employee personal data
  • Financial records
  • Unspecified corporate documents

What the group claims

A prominent global automotive accessory manufacturer owned by the Eastern Polymer Group of Thailand, part of a joint venture with Duys Engineering Group.

The leak post

captured from the group's site
Aeroklas Duys / Duys Engineering Group
a specialized automotive manufacturing company It was formed as a strategic joint venture between the Duys Engineering Group and Aeroklas (a prominent global automotive accessory manufacturer owned by the Eastern Polymer Group of Thailand). an industrial and mechanical engineering firm founded in South Africa in 1960. 
is an Italian pharmaceutical company specializing in the research and development of innovative nutraceuticals and medical devices. The company focuses on formulations covered by patents and unique dosage technologies to improve patient health and quality of life (but their data leak). 
is a American supplier and distributor of machine vision components, industrial cameras and image processing systems. 
Greggio Argento is a long-established Italian family business founded in 1948 in Sarmeola di Rubano (Padua). 
is a commercial construction company and general contractor headquartered in Placentia, California Founded in 2009, the company specializes in SCIF(Sensitive Compartmented Information Facilities) construction projects for high-security facilities, as well as tenant improvements in the aerospace and defense industry. Their…

Screenshot of the leak post
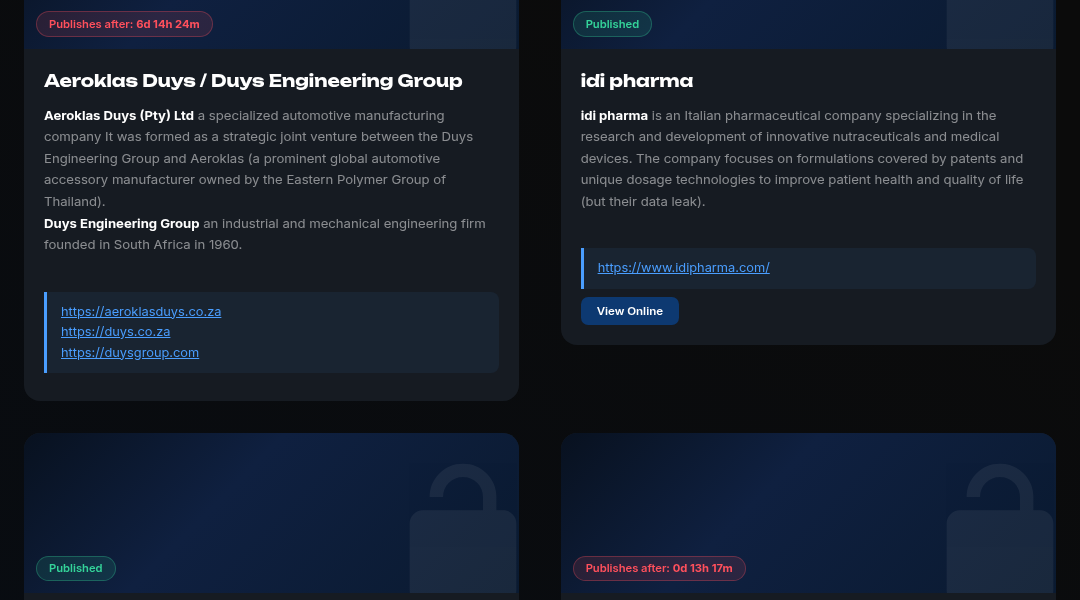
Leak screenshot for Aeroklas

Sources

Source

Indexed 4 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Deadlock

Deadlock is a ransomware group first observed in June 2026 with an apparent financial motivation, having claimed responsibility for attacks against at least 10 known victims across a geographically diverse target set. Given the recency of their emergence and limited public documentation by major threat intelligence organizations such as CISA, FBI, or Mandiant at this time, a comprehensive technical profile cannot be fully established. Based on available victimology data, the group has demonstrated a targeting pattern spanning Singapore, China, Sweden, Spain, and Nigeria, suggesting an opportunistic or globally distributed operational scope rather than a regionally focused campaign. Targeted sectors include manufacturing, business services, telecommunications, and financial services, indicating a preference for industries with high operational dependencies and potential for significant disruption, which is consistent with financially motivated ransomware actors seeking maximum leverage for ransom payment. No confirmed attribution regarding country of origin, RaaS affiliation, or specific tooling has been publicly documented by authoritative sources as of this profile's preparation. Due to the group's nascent operational timeline and the limited volume of publicly verified intelligence, analysts should treat this profile as preliminary and subject to significant revision as additional technical indicators, victim disclosures, and research reporting become available. Continued monitoring is advised given the cross-sector and cross-regional targeting behavior observed in this early operational phase. The group has been linked to 137 public disclosures across our corpus. First observed on a leak site on June 15, 2026; most recent post October 14, 2026. The operation is currently active.

Timeline of this disclosure

  • October 14, 2026Aeroklas listed by Deadlock on the group's public leak site
Data size
27 GB
Records
186207 files

Sector and geography

This disclosure adds to ransomware activity in the Automotive Manufacturing sector. Geographically, Aeroklas is reported in Thailand, a country with 63 ransomware disclosures in our corpus.

If your organisation is affected

A listing by Deadlock means Aeroklas appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Monitor for the data appearing on Deadlock's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.