Ransomware victim disclosure

← All victims

Anaergia Inc.

Claimed by CRY0 · listed 4 hours ago

~51.7 GB
Data size
33,233 files records
Today
Age
since listed · data leaked

Status timeline

  1. ListedOct 13, 2026
  2. Data leakeddate unknown

At a glance

Group
CRY0
Status
Data leaked
Country
Canada
Listed on leak site
Oct 13, 2026
Data size
~51.7 GB
Records
33,233 files

About the victim

AI dossier — public-source company profile

Anaergia Inc. is a company specializing in anaerobic digestion solutions, a technology used to convert organic waste into biogas and renewable energy. Based in Burlington, Ontario, Canada, they serve environmental and energy sectors.

Industry
Environmental Engineering & Renewable Energy (Anaerobic Digestion)
Address
809 Harrington Ct, Burlington, ON L7N 3N, Canada

Attack summary

Severity: high — Confirmed exfiltration of significant data volume (51.7 GB, 33k+ files) from a company in critical infrastructure (renewable energy/waste management). Data has been published. No detail on sensitive data types (PII, financial, proprietary IP) is given in the post, preventing 'critical' rating, but the volume and disclosure status warrant 'high'.

CRY0 claims to have exfiltrated approximately 33,233 files totaling ~51.7 GB from Anaergia Inc. The group published the data on their leak site, indicating data theft (exfiltration) rather than encryption-only.

high

Data the group says was taken

AI dossier — extracted from the leak post
  • Business files
  • Corporate records
  • Operational documents

What the group claims

World-Leading Anaerobic Digestion Solutions, located at 809 Harrington Ct, Burlington, ON L7N 3N

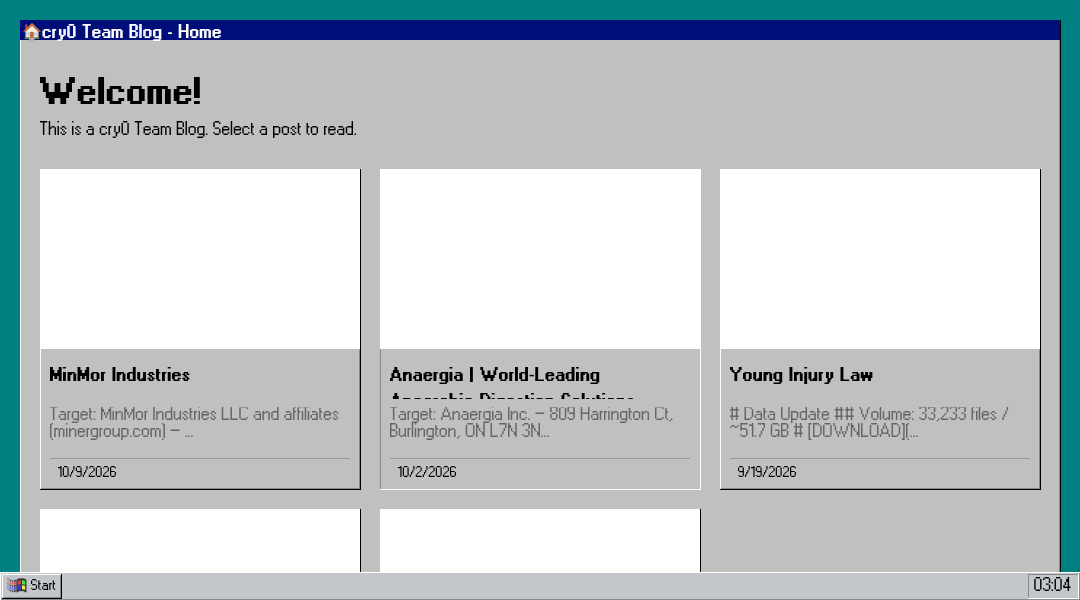
The leak post

captured from the group's site
cry0 Team Blog - Home
This is a cry0 Team Blog. Select a post to read.
Target: MinMor Industries LLC and affiliates (minergroup.com) — ...
### Anaergia | World-Leading Anaerobic Digestion Solutions
Target: Anaergia Inc. — 809 Harrington Ct, Burlington, ON L7N 3N...
# Data Update ## Volume: 33,233 files / ~51.7 GB # [DOWNLOAD](...
DINI is a family-run transportation and automotive business base...

Data the group says was taken

  • files

Screenshot of the leak post

Leak screenshot for Anaergia Inc.

Sources

Source

Indexed 4 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About CRY0

CRY0 is a ransomware group first observed in May 2026 with an apparent financial motivation, though its limited activity to date makes comprehensive attribution difficult. With only a single confirmed victim recorded and a targeting pattern focused on the transportation and automotive sectors, the group remains nascent and has not yet accumulated sufficient operational history to establish a well-documented profile in open-source intelligence reporting by organizations such as CISA, the FBI, Mandiant, or comparable security research firms. No confirmed country of origin, RaaS affiliation, or links to established threat actor clusters have been publicly documented at this time. Similarly, specific details regarding initial access vectors, tooling, encryption methodologies, or data exfiltration practices have not been publicly attributed to CRY0 by reputable sources, and no notable high-profile campaigns, record ransom demands, or law enforcement actions have been recorded against the group. Given its emergence in May 2026 and minimal victim count, CRY0 should be regarded as an emerging and unverified threat actor warranting continued monitoring, particularly within transportation and automotive industry verticals, as future activity may yield more substantive intelligence to support a fuller threat assessment. The group has been linked to 8 public disclosures across our corpus. First observed on a leak site on May 17, 2026; most recent post October 13, 2026. The operation is currently active.

Timeline of this disclosure

  • October 13, 2026Anaergia Inc. listed by CRY0 on the group's public leak site
Data size
~51.7 GB
Records
33,233 files

Other recent disclosures by CRY0

CRY0 has been linked to 8 public victims on Darkfield. A sample of the most recent:

See the full CRY0 dossier →

Sector and geography

This disclosure adds to ransomware activity in the Environmental/Energy sector. Geographically, Anaergia Inc. is reported in Canada, a country with 1,055 ransomware disclosures in our corpus.

If your organisation is affected

A listing by CRY0 means Anaergia Inc. appeared on a ransomware extortion site and data attributed to it has been published. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CCCS (Canada), as required for your jurisdiction.
  • Monitor for the data appearing on CRY0's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.