

Ransomware victim disclosure

← All victims

Unknown Berlin-based Online Marketing Agency

Claimed by Rhysida · listed 4 hours ago

Today
Age
since listed · listed for ransom

Status timeline

  1. ListedOct 4, 2026

Current state: Listed for ransom

At a glance

Group
Rhysida
Status
Listed for ransom
Country
Germany
Listed on leak site
Oct 4, 2026

About the victim

AI dossier — public-source company profile

A Berlin-based online marketing agency with over 12 years of specialisation in managing national and international digital projects. Operating from four German cities (Berlin, Dresden, Munich, Cologne), the firm serves clients across multiple industries with a team of more than 40 employees.

Industry
Online Marketing & Advertising
Address
Berlin, Germany (with offices in Dresden, Munich, and Cologne)
Employees
40+

Attack summary

Severity: low — The post lists only the company name and operational structure with no specific data categories, file counts, or proof materials attributed to the Berlin marketing agency. The surrounding entries in the post are distinct victims unrelated to this target. Without demonstrated exfiltration or operational impact, this is a listing/announcement only.

Rhysida claims to have exfiltrated 2,478,837 files totalling 1.84 TB of data. The leak post is a collage mixing unrelated victims (SKAFF decorative fabrics in Lebanon, Mat Bao Corporation in Vietnam, ElectroHeat furnaces, a US HOA/homeowner database, and a US medical clinic), but the Berlin marketing agency entry states only general company information with no specific data inventory disclosed for this victim.

low

What the group claims

An agency with more than 40 employees managing national and international online projects. Based in Berlin, Dresden, Munich and Cologne, specialist in online marketing for more than twelve years.

The leak post

captured from the group's site
SKAFF is a leader in Lebanon in the field of decorative fabrics. Files: 139,377Data volume: ~268 GB**Full HR dossiers - ~40 scans of Lebanese national ID cards (both sides + photos), a director's passport, civil-status extracts.Banking data - employee account files at Byblos Bank (named per person), Cedrus Bank corporate card program with banker contacts, account statements.Payroll violations - unpaid-salary analysis file, payroll module source code, staff leave requests.Employees' private lives - family photo archives on the work server.Commerce � price lists, Four Seasons and Les Galeries proposals, customs/export documents (Dubai, Erbil), customer claims.
With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner!
Mat Bao Corporation offers a range of services including domain registration, cloud hosting, professional email solutions, and cloud server storage. Files: 746,108Data volume: 106.8 GBGovernment inspection materials - NEAC inspection decision No. 61/QD (29.04.2025) against the certification authority, worki…

Screenshot of the leak post
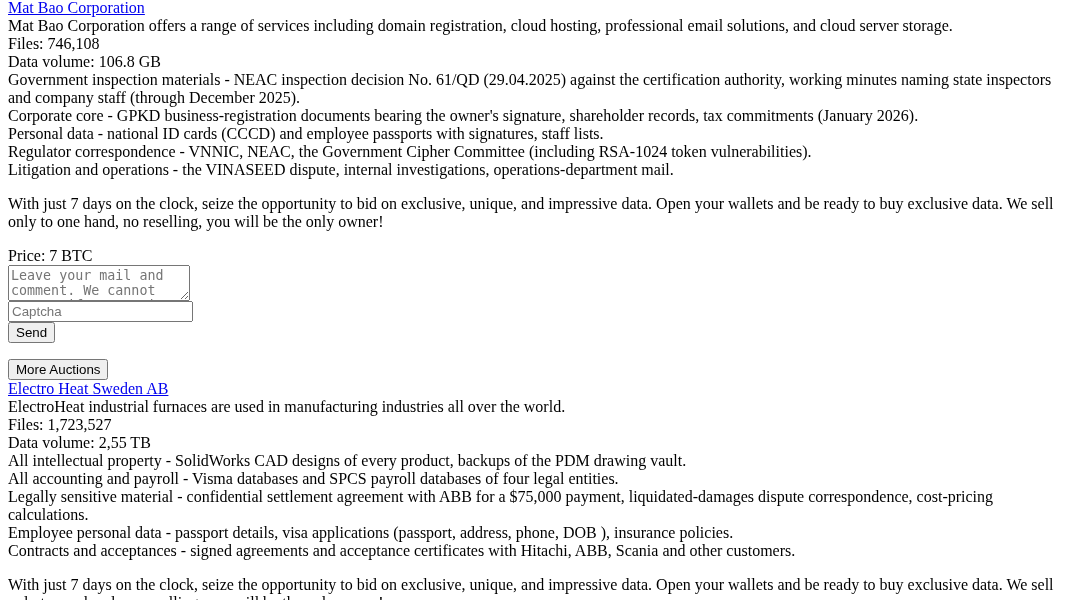
Leak screenshot for Unknown Berlin-based Online Marketing Agency

Sources

Source

Indexed 4 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Rhysida

Rhysida is a ransomware group that emerged in June 2023, operating with primarily financial motivations through targeted attacks against critical infrastructure and public sector organizations. The group's origin and potential state affiliations remain unclear, though they operate independently rather than as a traditional Ransomware-as-a-Service model, with limited public documentation regarding connections to other cybercriminal organizations. Rhysida employs double extortion tactics, typically gaining initial access through compromised VPN credentials and exploiting vulnerable public-facing applications before deploying their ransomware payload and exfiltrating sensitive data prior to encryption. The group has demonstrated a particular focus on healthcare and educational institutions, with notable attacks documented by CISA and FBI advisories highlighting their targeting of hospitals and school districts across multiple countries, resulting in significant operational disruptions to critical services. As of late 2024, Rhysida remains an active threat with continued operations targeting organizations primarily in the United States, Canada, and other Western nations, maintaining their focus on high-value sectors where operational disruption can maximize ransom payment likelihood. The group has been linked to 369 public disclosures across our corpus. First observed on a leak site on June 5, 2023; most recent post October 4, 2026. The operation is currently active.

Timeline of this disclosure

  • October 4, 2026Unknown Berlin-based Online Marketing Agency listed by Rhysida on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the Marketing/Advertising sector. Geographically, Unknown Berlin-based Online Marketing Agency is reported in Germany, a country with 926 ransomware disclosures in our corpus.

If your organisation is affected

A listing by Rhysida means Unknown Berlin-based Online Marketing Agency appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CERT-Bund (Germany), as required for your jurisdiction.
  • Monitor for the data appearing on Rhysida's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.