

Ransomware victim disclosure
← All victimsSKAFF
Claimed by Rhysida · listed 4 hours ago
Status timeline
- ListedOct 4, 2026
Current state: Listed for ransom
At a glance
- Group
- Rhysida
- Status
- Listed for ransom
- Country
- Lebanon
- Sector
- Retail/Textiles
- Listed on leak site
- Oct 4, 2026
- Data size
- ~268 GB
- Records
- 139377
About the victim
AI dossier — public-source company profileSKAFF is a Lebanese leader in decorative fabrics, supplying commercial clients including high-end hospitality brands. The company operates in Beirut and engages in regional trade including exports to Dubai and Erbil.
- Industry
- Decorative Fabrics & Textiles
Attack summary
Severity: critical — Confirmed exfiltration of PII at scale including government-issued ID documents (40+ national ID cards), passport data, banking account information, and employee personal records. Includes financial data from named Lebanese banks and sensitive HR/payroll information.Rhysida claims to have exfiltrated approximately 268 GB of SKAFF data, including full HR dossiers with national ID scans, banking account details, payroll records, and customer information. The group offers the data for auction with a 7-day bidding window.
Data the group says was taken
AI dossier — extracted from the leak post- HR dossiers with Lebanese national ID cards (40+ scans, both sides and photos)
- Director's passport and civil-status documents
- Employee banking data from Byblos Bank and Cedrus Bank
- Payroll records and unpaid-salary analysis
- Payroll module source code
- Staff leave requests
- Family photo archives
- Customer price lists and proposals
- Customs and export documents
What the group claims
SKAFF is a leader in Lebanon in the field of decorative fabrics.
The leak post
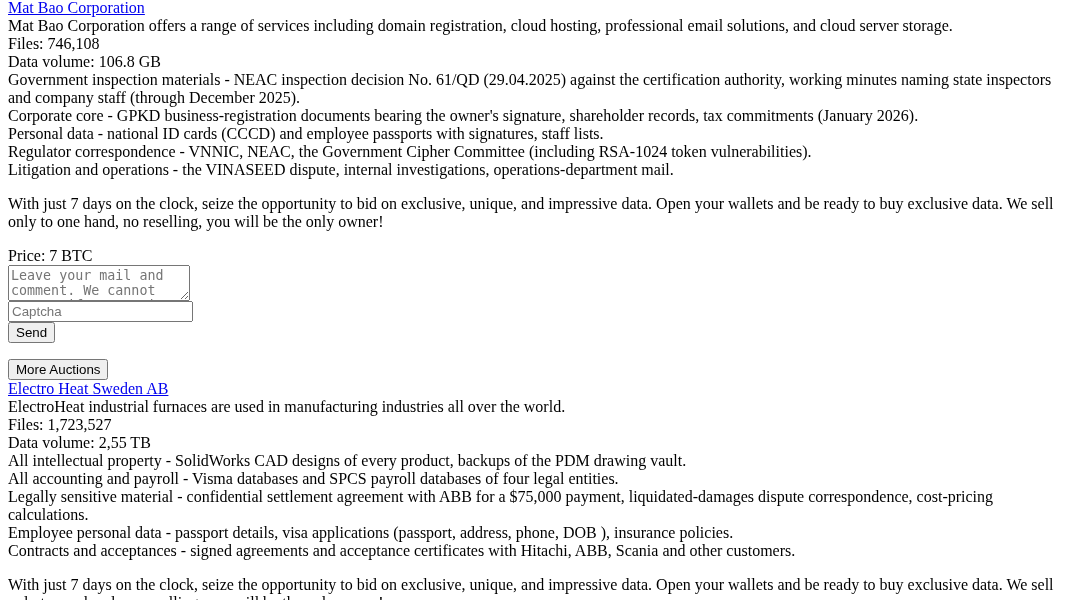
captured from the group's siteSKAFF is a leader in Lebanon in the field of decorative fabrics. Files: 139,377Data volume: ~268 GB**Full HR dossiers - ~40 scans of Lebanese national ID cards (both sides + photos), a director's passport, civil-status extracts.Banking data - employee account files at Byblos Bank (named per person), Cedrus Bank corporate card program with banker contacts, account statements.Payroll violations - unpaid-salary analysis file, payroll module source code, staff leave requests.Employees' private lives - family photo archives on the work server.Commerce � price lists, Four Seasons and Les Galeries proposals, customs/export documents (Dubai, Erbil), customer claims. With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! Mat Bao Corporation offers a range of services including domain registration, cloud hosting, professional email solutions, and cloud server storage. Files: 746,108Data volume: 106.8 GBGovernment inspection materials - NEAC inspection decision No. 61/QD (29.04.2025) against the certification authority, worki…
Data the group says was taken
- HR dossiers
- national ID cards
- passport
- civil-status extracts
- banking data
- employee account files
- corporate card program data
- account statements
- payroll data
- payroll module source code
- leave requests
- family photos
- price lists
- customs/export documents
- customer claims
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.