

Ransomware victim disclosure
← All victimsItaly (government/institutions)
Claimed by IAMNOTAVILLAIN · listed 1 hour ago
Status timeline
- ListedSep 29, 2026
Current state: Listed for ransom
At a glance
- Group
- IAMNOTAVILLAIN
- Status
- Listed for ransom
- Country
- Italy
- Sector
- Government
- Listed on leak site
- Sep 29, 2026
- Data size
- 150GB
- Records
- 85000+ files
About the victim
AI dossier — public-source company profileItalian government institutions and departments. The leak post references multiple top-level government units and offices across Italy's public sector.
- Industry
- Government & Public Administration
Attack summary
Severity: critical — Claimed exfiltration of 150GB from Italian government institutions combined with large-scale financial/identity data (KYC records) from Revolut users—regulated financial data at significant scale affecting both government operations and individual financial identity.IAMNOTAVILLAIN claims to have exfiltrated 150GB of data (85,000+ files) from Italian government departments and institutions for alleged failure to follow data protection laws. The group also references Revolut user data (KYC documents, addresses, phone numbers, emails, bank/crypto transaction records) obtained from the company, claiming Revolut ignored a security report.
Data the group says was taken
AI dossier — extracted from the leak post- Government department files
- KYC documents (Revolut users)
- Personal addresses
- Phone numbers
- Email addresses
- Bank account information
- Cryptocurrency transaction records
- Fiat transaction records
- ID scans
What the group claims
Italy exposed for failing to follow proper data protection laws. Top departments, units, and offices affected.
The leak post
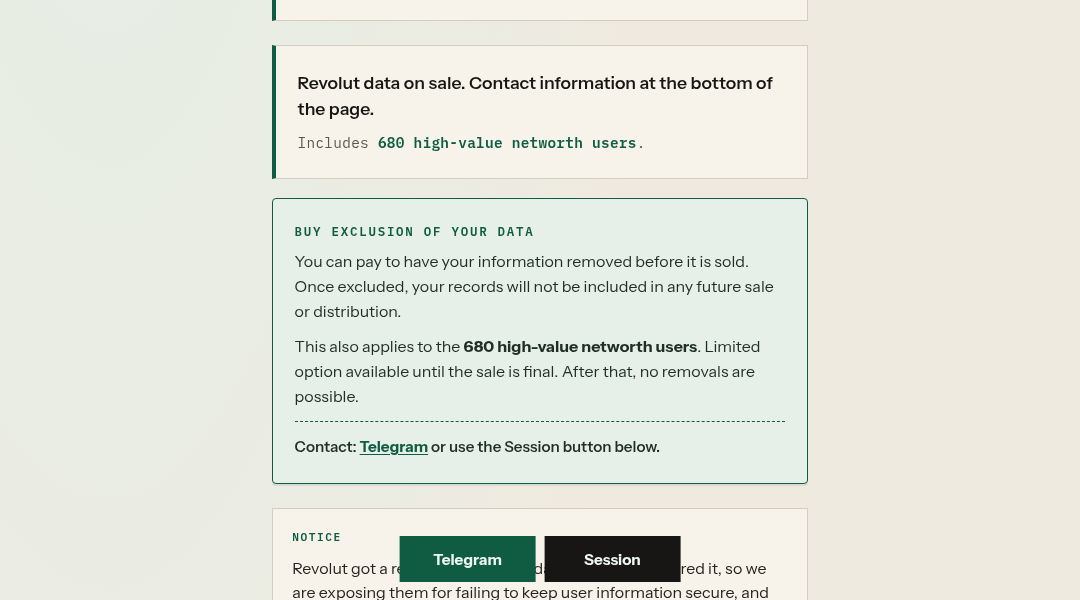
captured from the group's siteItaly is being exposed for failing to follow proper data protection laws. Includes Includes 85,000+ Files — 150GB. Top departments, units, offices affected. Revolut data on sale. Contact information at the bottom of the page. ### Buy exclusion of your data You can pay to have your information removed before it is sold. Once excluded, your records will not be included in any future sale or distribution. This also applies to the . Limited option available until the sale is final. After that, no removals are possible. Contact: or use the Session button below. Revolut got a report about a user database. They ignored it, so we are exposing them for failing to keep user information secure, and for sending data from a different jurisdiction. We have everything, including KYC documents, address, phone number, email, bank accounts, and fiat and crypto transactions. An impersonator and scammer who used to work with us took a small sample we handed him and is now claiming the breach as his. That cut is not the full set. Revolut and the other companies sent the data to us. He did not do this. We can prove it: the originals, the volume, the conversations, and the companies that sent it.…
Data the group says was taken
- files
Screenshot of the leak post
Sources
Source
Indexed 1 hour agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.