Ransomware victim disclosure
← All victimsRevolut
Claimed by IAMNOTAVILLAIN · listed 15 days ago
Status timeline
- ListedSep 29, 2026
- Data leakeddate unknown
At a glance
- Group
- IAMNOTAVILLAIN
- Status
- Data leaked
- Sector
- Financial Services
- Listed on leak site
- Sep 29, 2026
- Data size
- 150 GB
About the victim
AI dossier — public-source company profileRevolut is a financial services and cryptocurrency platform offering banking, payment, and digital asset trading services. The company operates internationally with a user base requiring KYC (Know Your Customer) documentation.
- Industry
- Financial Services & Fintech
Attack summary
Severity: critical — Confirmed exfiltration of large-scale PII and financial data (85,000+ user records including KYC documents, account identifiers, transaction history). Data involves regulated financial institution with sensitive customer identity and transaction information. Published status indicates proof materials are available.The IAMNOTAVILLAIN group claims to have exfiltrated a user database containing 85,000+ files (150 GB) from Revolut, including KYC documents, personal identifiers, and transaction records. The group alleges Revolut ignored a security report and transferred customer data across jurisdictions in violation of data protection law.
Data the group says was taken
AI dossier — extracted from the leak post- KYC documents
- User database records
- Names
- Email addresses
- Phone numbers
- Physical addresses
- Bank account details
- ID document scans
- Fiat transaction history
- Cryptocurrency transaction history
What the group claims
Revolut exposed for failing to keep user information secure and for sending data from a different jurisdiction. Includes KYC documents, contact information, bank accounts, and transaction data. An ignored report about a user database led to exposure.
The leak post
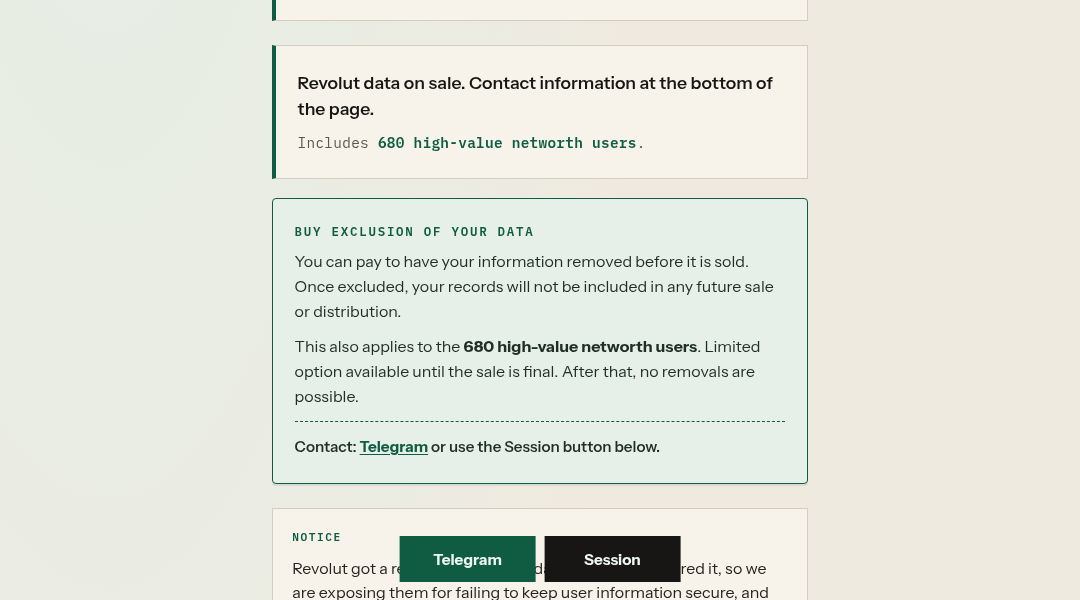
captured from the group's siteItaly is being exposed for failing to follow proper data protection laws. Includes Includes 85,000+ Files — 150GB. Top departments, units, offices affected. Revolut data on sale. Contact information at the bottom of the page. ### Buy exclusion of your data You can pay to have your information removed before it is sold. Once excluded, your records will not be included in any future sale or distribution. This also applies to the . Limited option available until the sale is final. After that, no removals are possible. Contact: or use the Session button below. Revolut got a report about a user database. They ignored it, so we are exposing them for failing to keep user information secure, and for sending data from a different jurisdiction. We have everything, including KYC documents, address, phone number, email, bank accounts, and fiat and crypto transactions. An impersonator and scammer who used to work with us took a small sample we handed him and is now claiming the breach as his. That cut is not the full set. Revolut and the other companies sent the data to us. He did not do this. We can prove it: the originals, the volume, the conversations, and the companies that sent it.…
Data the group says was taken
- KYC documents
- name
- phone number
- address
- account identifiers
- ID scans
- fiat transactions
- crypto transactions
- bank accounts
Screenshot of the leak post
Sources
Source
Indexed 15 days agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.