

Ransomware victim disclosure
← All victimsAnne Arundel County
Claimed by Rhysida · listed 2 hours ago
Status timeline
- ListedOct 11, 2026
Current state: Listed for ransom
At a glance
- Group
- Rhysida
- Status
- Listed for ransom
- Country
- United States
- Sector
- Government
- Listed on leak site
- Oct 11, 2026
- Data size
- 2.6 TB
- Records
- 814,500 files
About the victim
AI dossier — public-source company profileAnne Arundel County is a governmental body established in 1964, headquartered in Anne Arundel County, Maryland. It consists of numerous departments, services and sections providing public administration and services to county residents.
- Industry
- Local Government Administration
- Address
- Anne Arundel County, Maryland, US
- Founded
- 1964
Attack summary
Severity: critical — Exfiltration of massive scale (2.6 TB from county alone) involving highly regulated and sensitive data: background checks with SSNs, methadone clinic records under 42 CFR Part 2 (strictest US confidentiality regime), medical records with diagnoses and PHI, financial/banking data, government payroll, and law enforcement intelligence. Multiple categories of PII and regulated health data at scale affecting thousands of individuals and government operations.Rhysida claims to have exfiltrated 814,500 files totaling 2.6 TB from Anne Arundel County, including background checks, medical records, payroll data, and jail intelligence files. The group also claims separate compromise of law firm Gress Clark Young & Schoepper (167,804 files, ~166.4 GB) containing client banking details, SSNs, medical records, and court e-filing credentials.
Data the group says was taken
AI dossier — extracted from the leak post- 721 background-check dossiers with full SSNs
- Tens of thousands of medical faxes (2022–2026) with patient names and diagnoses
- Methadone clinic records (42 CFR Part 2 regulated)
- 47,602 medical-assistance files with driver licenses, Green Cards, SSN cards, tax forms, bank data
- County payroll registers with salaries, HR memos, contracts, pension and discipline databases
- Jail gang-intelligence files and gang-member master list
- Law firm banking details, client SSNs and signatures
- W-9, I-9, W-4 forms with DL/SSN card copies
- Medical photos and imaging; hundreds of pages of PHI
- Court e-filing system credentials
What the group claims
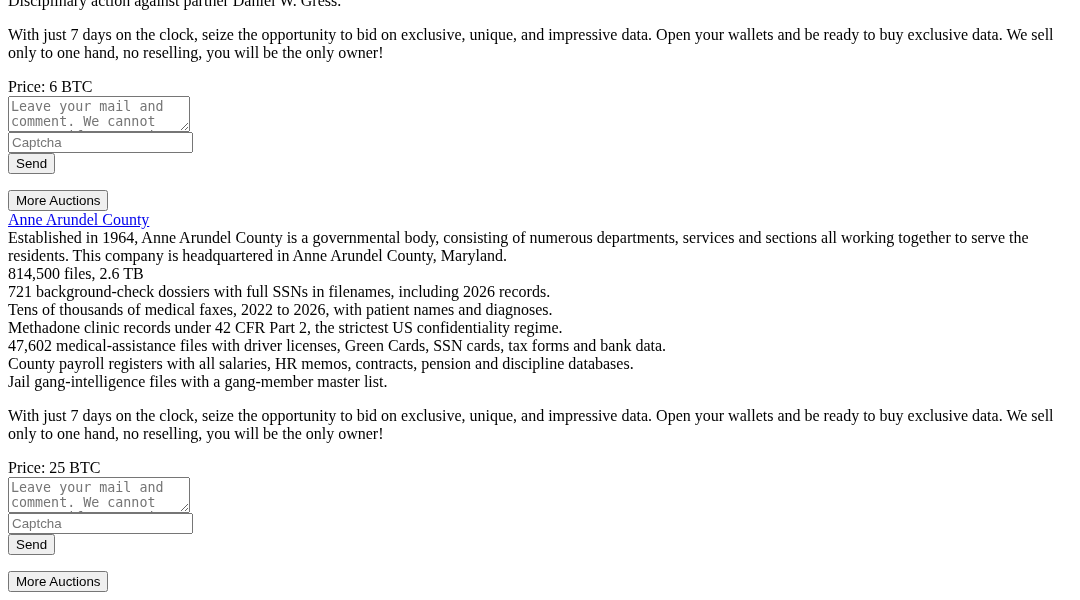
Governmental body established in 1964, headquartered in Anne Arundel County, Maryland, consisting of numerous departments, services and sections serving residents. Data includes background-check dossiers with SSNs, medical faxes with patient names and diagnoses, methadone clinic records under 42 CFR Part 2, medical-assistance files with identity documents and financial data, payroll registers, HR records, pension and discipline databases, and jail gang-intelligence files.
The leak post
captured from the group's site[Gress Clark Young & Schoepper](https://www.gressandclarklaw.com)
167,804 files / ~166.4 GBBanking details - of the firm and its clients.SSNs + signatures of clients/witnesses; W-9, I-9 forms with DL/SSN card copies; W-4 forms.BIIA case-management procedures (Board of Industrial Insurance Appeals): default orders (Order of Default), internal 'Conference Questions', consulting-fee payments to experts.Firm finances: the firm's QuickBooks company file, VOID checks bearing signatures, expert-payment records, SaaS invoices.Medical photos and imaging; hundreds of pages of PHI/APF (Activity Prescription Forms) - X-rays, complete medical records.'Coaching' letters to doctors - including a letter to the physician in the Jachacy matter with wording indicative of steering a medical opinion ('coaching letter') - a potential ethics violation regarding witness handling.Credentials/access to the SPC e-file system (court e-filing).Disciplinary action against partner Daniel W. Gress.
With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only …Data the group says was taken
- background check dossiers
- SSNs
- medical faxes
- patient names
- diagnoses
- methadone clinic records
- medical-assistance files
- driver licenses
- Green Cards
- SSN cards
- tax forms
- bank data
- payroll registers
- HR memos
- contracts
- pension databases
- discipline databases
- gang-intelligence files
- gang-member master list
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.