

Ransomware victim disclosure
← All victimsSIFCO Industries
Claimed by METAENCRYPTER · listed 1 hour ago
Status timeline
- ListedSep 16, 2026
Current state: Listed for ransom
At a glance
- Group
- METAENCRYPTER
- Status
- Listed for ransom
- Country
- United States
- Listed on leak site
- Sep 16, 2026
- Data size
- 1 TB
About the victim
AI dossier — public-source company profileSIFCO Industries is a worldwide provider of highly engineered forged components and machined assemblies to the aerospace, energy, and defense markets. The company supplies flight-critical components to leading aircraft and engine manufacturers, as well as to steam and gas turbine manufacturers and oil producers in the energy sector.
- Industry
- Aerospace & Defense Manufacturing
Attack summary
Severity: high — Confirmed exfiltration of 2 TB of data from a defense and aerospace contractor handling flight-critical components. Exposure includes proprietary engineering, business records, and strategic information for a company supplying the global aviation and energy sectors. Defense/aerospace sector classification elevates severity even without explicit regulated data confirmation.METAENCRYPTER claims to have exfiltrated 1 TB of internal data from SIFCO Industries, with an additional 1 TB obtained in the 24 hours preceding the leak post. The group states the company 'remains vulnerable' and has listed the victim with a manifest of exfiltrated files and representative samples.
Data the group says was taken
AI dossier — extracted from the leak post- Internal correspondence
- Engineering and design documents
- Business records and financial data
- Employee and customer information
- Proprietary manufacturing processes
- Strategic business information
What the group claims
A worldwide provider of highly engineered forged components to the Aerospace, Energy and Defense markets. Supplies flight-critical forged components and machined assemblies to leading aircraft and engine manufacturers, steam and gas turbine manufacturers, and oil producers.
The leak post
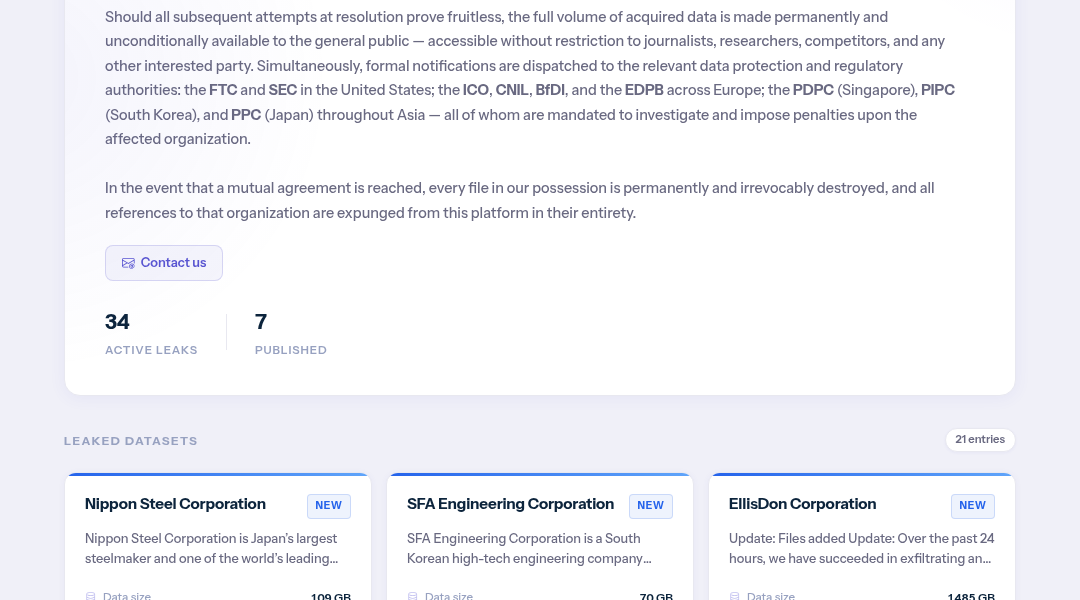
captured from the group's siteThis platform publishes data belonging to organizations that have elected to forgo negotiation entirely.Upon a company's initial listing, the complete manifest of exfiltrated files is disclosed alongside a curated selection of representative samples. Should the organization fail to establish contact prior to the stated deadline, a portion of the compromised data is released into the public domain.Should all subsequent attempts at resolution prove fruitless, the full volume of acquired data is made permanently and unconditionally available to the general public — accessible without restriction to journalists, researchers, competitors, and any other interested party. Simultaneously, formal notifications are dispatched to the relevant data protection and regulatory authorities: the and in the United States; the , , , and the across Europe; the (Singapore), (South Korea), and (Japan) throughout Asia — all of whom are mandated to investigate and impose penalties upon the affected organization.In the event that a mutual agreement is reached, every file in our possession is permanently and irrevocably destroyed, and all references to that organization are expunged from this platform in th…
Screenshot of the leak post
Sources
Source
Indexed 1 hour agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.