

Ransomware victim disclosure

All victims

Hologic, Inc.

Claimed by METAENCRYPTER · listed 1 hour ago

1 TB (additional, exfiltrated over 24 hours)
Data size
Today
Age
since listed · data leaked

Status timeline

  1. ListedSep 16, 2026
  2. Data leakeddate unknown

At a glance

Status
Data leaked
Listed on leak site
Sep 16, 2026
Data size
1 TB (additional, exfiltrated over 24 hours)

What the group claims

A U.S.-based medical technology company specializing in women's health. Develops and manufactures diagnostic, imaging, and surgical products with a strong focus on breast health, gynecology, diagnostics, and osteoporosis assessment.

The leak post

captured from the group's site
This platform publishes data belonging to organizations that have elected to forgo negotiation entirely.Upon a company's initial listing, the complete manifest of exfiltrated files is disclosed alongside a curated selection of representative samples. Should the organization fail to establish contact prior to the stated deadline, a portion of the compromised data is released into the public domain.Should all subsequent attempts at resolution prove fruitless, the full volume of acquired data is made permanently and unconditionally available to the general public — accessible without restriction to journalists, researchers, competitors, and any other interested party. Simultaneously, formal notifications are dispatched to the relevant data protection and regulatory authorities: the and in the United States; the , , , and the across Europe; the (Singapore), (South Korea), and (Japan) throughout Asia — all of whom are mandated to investigate and impose penalties upon the affected organization.In the event that a mutual agreement is reached, every file in our possession is permanently and irrevocably destroyed, and all references to that organization are expunged from this platform in th…

Data the group says was taken

  • internal data

Screenshot of the leak post
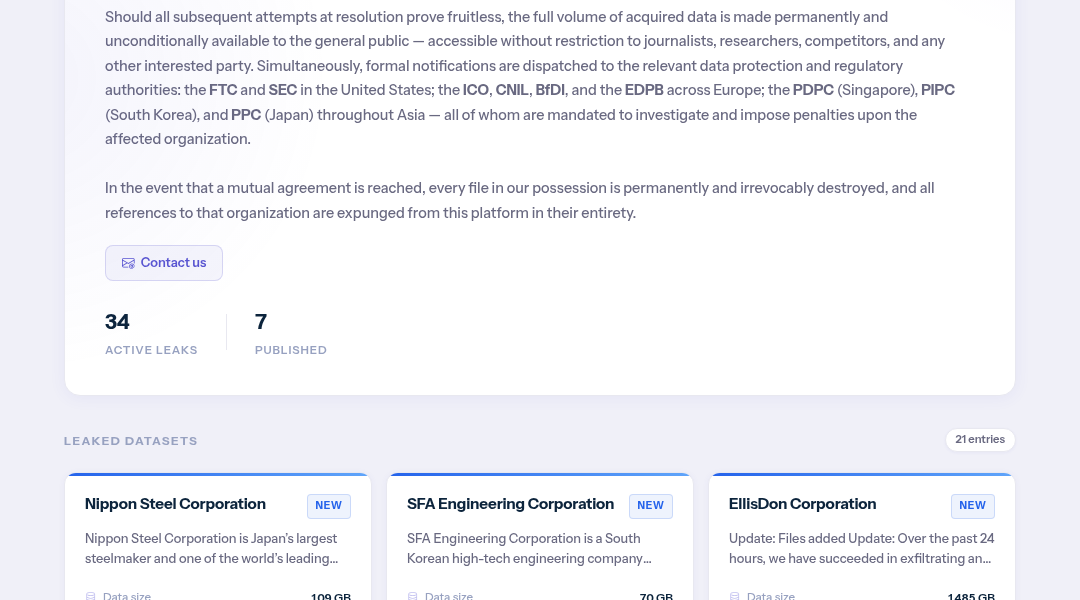
Leak screenshot for Hologic, Inc.

Sources

Source

Indexed 1 hour ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About METAENCRYPTER

METAENCRYPTER is a ransomware group first observed in September 2026 with an apparent primary motivation of financial gain, having claimed at least 13 known victims across multiple high-value sectors since its emergence. The group's country of origin and potential affiliations with established threat actors or ransomware-as-a-service ecosystems remain unconfirmed in publicly available reporting from CISA, FBI, Mandiant, or other reputable security research organizations at this time. Based on victim telemetry, METAENCRYPTER demonstrates a clear focus on industrial and technology-oriented sectors, including manufacturing, home appliances and HVAC, high-tech engineering and industrial automation, pharmaceuticals, automotive manufacturing, and medical technology and healthcare, suggesting deliberate targeting of organizations with high operational disruption thresholds and potential willingness to pay ransoms to restore critical processes. The group's primary attack vectors, tooling, encryption mechanisms, and use of double or triple extortion tactics have not been extensively documented in open-source intelligence reporting as of this writing, likely reflecting the group's recent emergence and relatively limited victim count. Geographic targeting patterns indicate a concentration on victims in the United States, Japan, Germany, Singapore, and Canada, consistent with a financially motivated actor prioritizing economically developed nations with technology-heavy industrial bases. Given the group's recent first observation date and limited public attribution data, METAENCRYPTER should be considered an emerging threat requiring continued monitoring, and organizations in the targeted sectors are advised to follow CISA and FBI guidance on ransomware defense pending further technical reporting. The group has been linked to 13 public disclosures across our corpus. First observed on a leak site on September 16, 2026. The operation is currently active.

Timeline of this disclosure

  • September 16, 2026Hologic, Inc. listed by METAENCRYPTER on the group's public leak site
Data size
1 TB (additional, exfiltrated over 24 hours)

Sector and geography

This disclosure adds to ransomware activity in the Medical Technology / Healthcare sector. Geographically, Hologic, Inc. is reported in United States, a country with 11,033 ransomware disclosures in our corpus.

If your organisation is affected

A listing by METAENCRYPTER means Hologic, Inc. appeared on a ransomware extortion site and data attributed to it has been published. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CISA (United States), as required for your jurisdiction.
  • Monitor for the data appearing on METAENCRYPTER's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.