

Ransomware victim disclosure
← All victimsAudit and Tax Audit Company Medellín
Claimed by Emperador · listed 3 hours ago
Status timeline
- ListedOct 8, 2026
- Data leakeddate unknown
At a glance
About the victim
AI dossier — public-source company profileA Colombian audit and tax services firm based in Medellín with over 5 years of operating experience. The company provides audit and tax consulting services to business clients.
- Industry
- Professional Services / Audit & Tax
- Address
- Calle 17 sur 44 - 159, Oficina 1501, Edificio Claroscuro, Medellín, Colombia
Attack summary
Severity: high — Confirmed exfiltration of sensitive data including PII (employee and customer personal data) and tax/financial documents from a professional services firm. Scale of 17,000 documents indicates significant data volume. Tax and financial records are regulated sensitive data.The emperador group claims to have exfiltrated personal data of employees and customers, tax documents, databases, and other business documents from the company.
Data the group says was taken
AI dossier — extracted from the leak post- Employee personal data
- Customer personal data
- Tax documents
- Databases
- Business documents
What the group claims
Colombian company providing audit and tax audit services with more than 5 years of experience, located at Calle 17 sur 44 - 159 Oficina 1501 Edificio Claroscuro, Medellín, Colombia.
The leak post
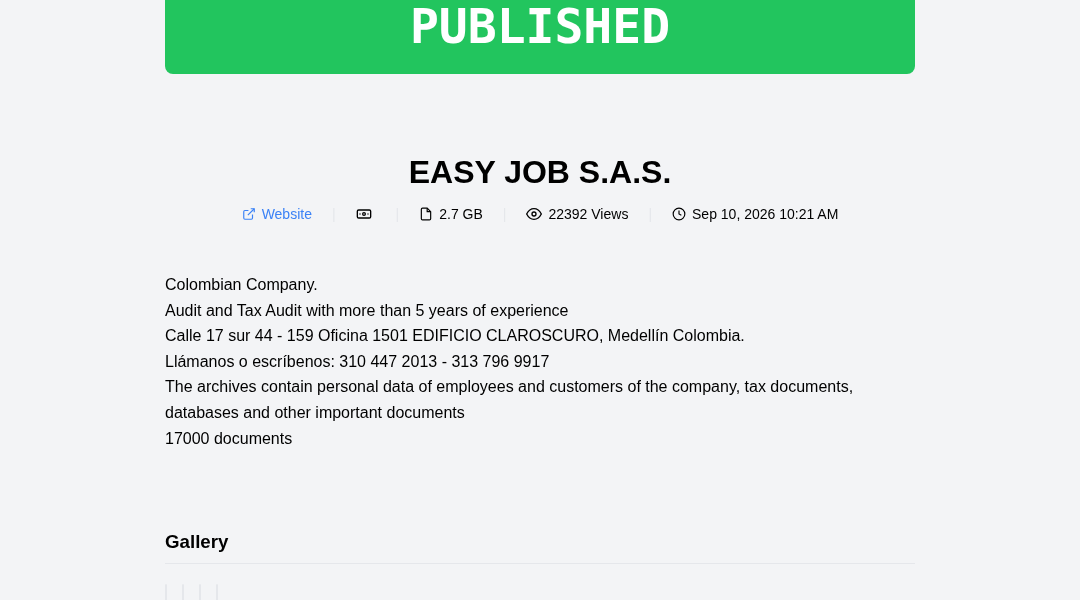
captured from the group's siteColombian Company.Audit and Tax Audit with more than 5 years of experienceCalle 17 sur 44 - 159 Oficina 1501 EDIFICIO CLAROSCURO, Medellín Colombia.Llámanos o escríbenos: 310 447 2013 - 313 796 9917The archives contain personal data of employees and customers of the company, tax documents, databases and other important documents17000 documents
Data the group says was taken
- personal data of employees
- personal data of customers
- tax documents
- databases
- other important documents
Screenshot of the leak post
Sources
Source
Indexed 3 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.