

Ransomware victim disclosure
← All victimsGranja Avícola La Ponderosa
listed as Granja Avicola La Ponderosa · Claimed by Emperador · listed 55 minutes ago
Status timeline
- ListedOct 2, 2026
Current state: Listed for ransom
At a glance
About the victim
AI dossier — public-source company profileGranja Avícola La Ponderosa is a Venezuelan agricultural enterprise specializing in the purchase, sale, import, export, breeding, processing, and marketing of poultry and domestic animals. The company maintains personnel and customer records across its operations.
- Industry
- Poultry & Livestock Breeding
Attack summary
Severity: high — Confirmed exfiltration of 41 GB including personnel and customer data at scale; sensitive business records exposed.The grupo emperador claims to have exfiltrated 41 GB of data including several thousand documents containing personnel and customer information from the company's systems.
Data the group says was taken
AI dossier — extracted from the leak post- Personnel records
- Customer data
- Business documents
What the group claims
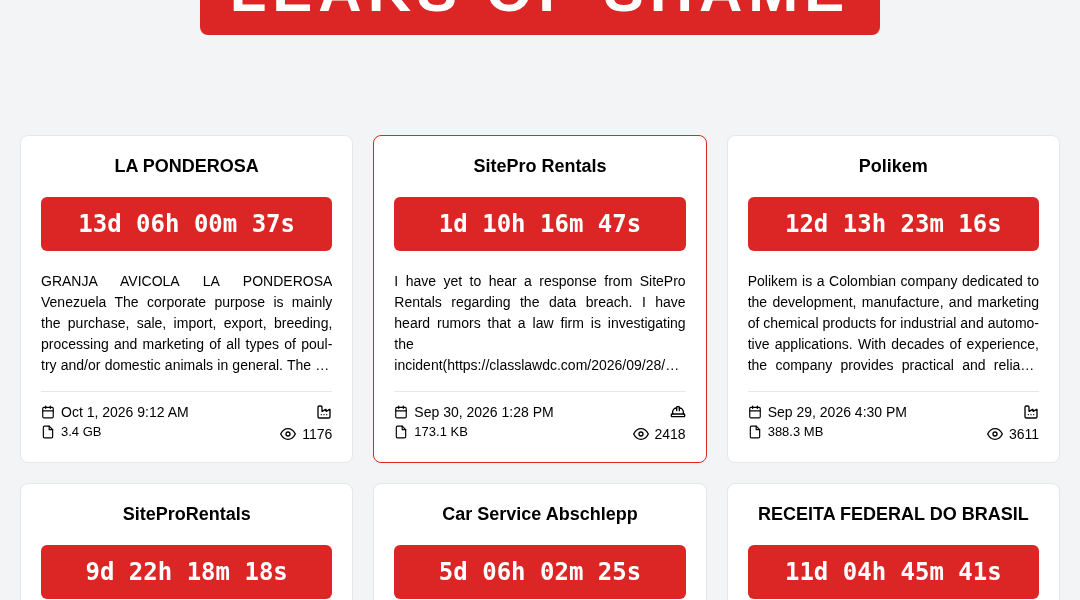
Corporate purpose is mainly the purchase, sale, import, export, breeding, processing and marketing of all types of poultry and/or domestic animals in general.
The leak post
captured from the group's site[ GRANJA AVICOLA LA PONDEROSA Venezuela The corporate purpose is mainly the purchase, sale, import, export, breeding, processing and marketing of all types of poultry and/or domestic animals in general. The archives contain several thousand documents with personnel and customer data. ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/la-ponderosa/) [ I have yet to hear a response from SitePro Rentals regarding the data breach. I have heard rumors that a law firm is investigating the incident(https://classlawdc.com/2026/09/28/sitepro-rentals-data-breach-investigation/). I am giving you 72 hours to contact me, otherwise I will leak the active employee details. The information includes: IsTotalItem, Department_ShortName, Employee_FirstName, Employee_LastName, EmployeeEmploymentStatus_EmployeeNumber, Employee_HireDate, EmploymentStatus_ShortName, OrgUnit_ShortName, DeptJob_ShortName, EmployeeManager_ManagerDisplayName, PayType_ShortName, PayClass_ShortName, Employee_SocialSecurityNumber, Department_ShortName2, Employee_Gender, Employee_MiddleName, PersonAddress_Address1, PersonAddress_Address2, PersonAddress_City, PersonAddress_PostalCode, PersonAddress_StateC…
Data the group says was taken
- personnel data
- customer data
Screenshot of the leak post
Sources
Source
Indexed 55 minutes agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.