

Ransomware victim disclosure
← All victimsAmazon Informática LTDA
Claimed by Emperador · listed 2 hours ago
Status timeline
- ListedSep 29, 2026
Current state: Listed for ransom
At a glance
- Group
- Emperador
- Status
- Listed for ransom
- Country
- Brazil
- Sector
- Information Technology
- Listed on leak site
- Sep 29, 2026
- Data size
- 41 GB
- Records
- 17000 files
About the victim
AI dossier — public-source company profileAmazon Informática LTDA is an IT solutions integrator and managed services provider founded in Brazil in 1995. The company primarily serves public sector and government agencies across Brazilian federal and state entities, with strategic offices in Brasília and Belém, and international operations in Latin America and Portugal delivering government tech solutions and enterprise infrastructure support.
- Industry
- Information Technology Solutions & Managed Services
- Address
- Brasília/DF and Belém/PA, Brazil; with offices in Latin America and Europe (Portugal)
- Founded
- 1995
Attack summary
Severity: critical — Confirmed exfiltration of regulated PII at scale (CPF/RG data, banking credentials) from a government-focused IT provider with access to state and federal infrastructure. Data involves multiple sensitive Brazilian identity and financial documents.The grupo emperador claims full network compromise with access to virtual infrastructure, database clusters, and administrative credentials exposed in plaintext. They claim exfiltration of production and integration databases containing sensitive PII schemas, employee registries, banking credentials, CPF (Brazilian tax ID), and RG (identity) data.
Data the group says was taken
AI dossier — extracted from the leak post- Production and integration databases
- Employee registries
- Banking credentials
- CPF (Brazilian tax ID) data
- RG (national ID) data
- Confidential and financial information
- Administrative master credentials
What the group claims
Brazilian IT solutions integrator and managed services provider founded in 1995, primarily serving the public sector. Offices in Brasília/DF, Belém/PA, and internationally in Latin America and Portugal. Full network compromise with administrative credentials exposed.
The leak post
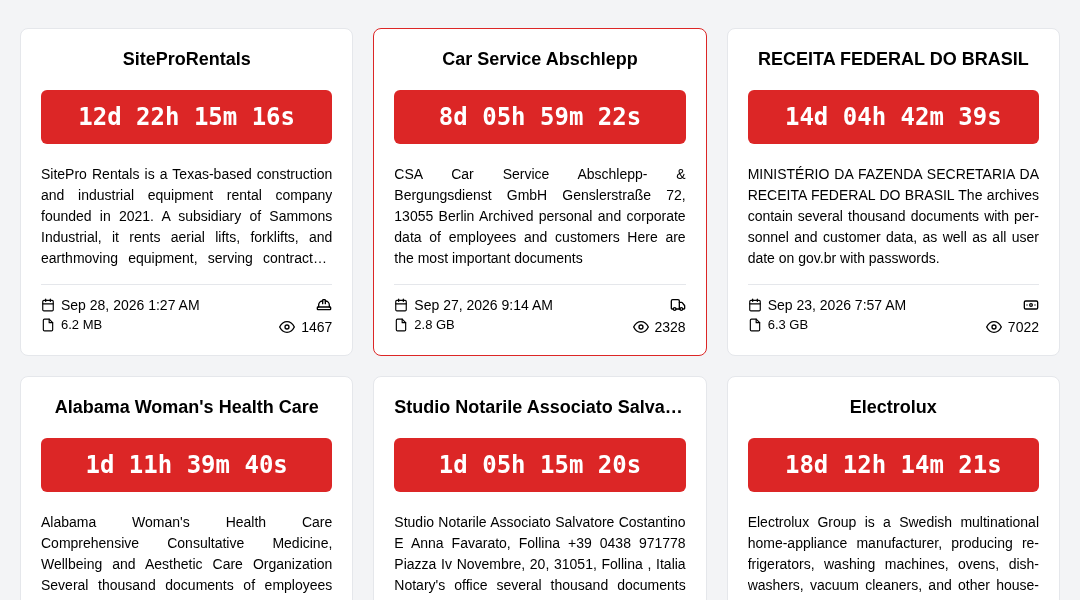
captured from the group's site[ SitePro Rentals is a Texas-based construction and industrial equipment rental company founded in 2021. A subsidiary of Sammons Industrial, it rents aerial lifts, forklifts, and earthmoving equipment, serving contractors across the U.S. from over 30 locations. We have every employee's Social Security number. Home addresses. Birth dates. Salaries. We know who's sick, who's on leave, who got fired and why. We also have 338,000 pay records.... Shortly, you will receive an email containing the instructions on how to proceed with this situation. The ransom is relatively small, just $150k USD in XMR... If you do not receive the email, contact us at: Email: [email protected] Session: 05651c7323273b723588d47455471ee9e27feb5187a30f2933554a705aacb38358 ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/siteprorentals/) [ CSA Car Service Abschlepp- & Bergungsdienst GmbH Genslerstraße 72, 13055 Berlin Archived personal and corporate data of employees and customers Here are the most important documents ](http://emprdr4p7iwlhpky33tswt3k2qdeljyjcdpoysabudmmrz4z32laexad.onion/post/car-service-abschlepp/) [ MINISTÉRIO DA FAZENDA SECRETARIA DA RECEITA FEDERAL DO BRASIL The …
Data the group says was taken
- infrastructure access
- databases
- PII
- employee registries
- banking credentials
- CPF
- RG data
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.