

Ransomware victim disclosure
← All victimsCSA Car Service Abschlepp- & Bergungsdienst GmbH
Claimed by Emperador · listed 22 hours ago
Status timeline
- ListedSep 28, 2026
- Data leakeddate unknown
At a glance
- Group
- Emperador
- Status
- Data leaked
- Country
- Germany
- Sector
- Transportation
- Listed on leak site
- Sep 28, 2026
About the victim
AI dossier — public-source company profileCSA Car Service Abschlepp- & Bergungsdienst GmbH is a German towing and vehicle recovery service operator based in Berlin. The company name indicates provision of roadside assistance and salvage/recovery services (Abschlepp- & Bergungsdienst).
- Industry
- Automotive Towing & Recovery Services
- Address
- Genslerstraße 72, 13055 Berlin, Germany
Attack summary
Severity: medium — Confirmed exfiltration of employee and customer PII at an unspecified scale; no proof files or screenshots are advertised in the truncated post. Moderate sensitivity due to personal data exposure, but lack of quantified proof or details limits classification to medium.The emperador group claims to have exfiltrated archived personal and corporate data of employees and customers. The post references 'most important documents' but does not specify the scope of data or confirm encryption.
Data the group says was taken
AI dossier — extracted from the leak post- employee personal data
- customer personal data
- corporate records
What the group claims
Car service, towing and recovery company based in Berlin. Archived personal and corporate data of employees and customers reportedly exfiltrated.
The leak post
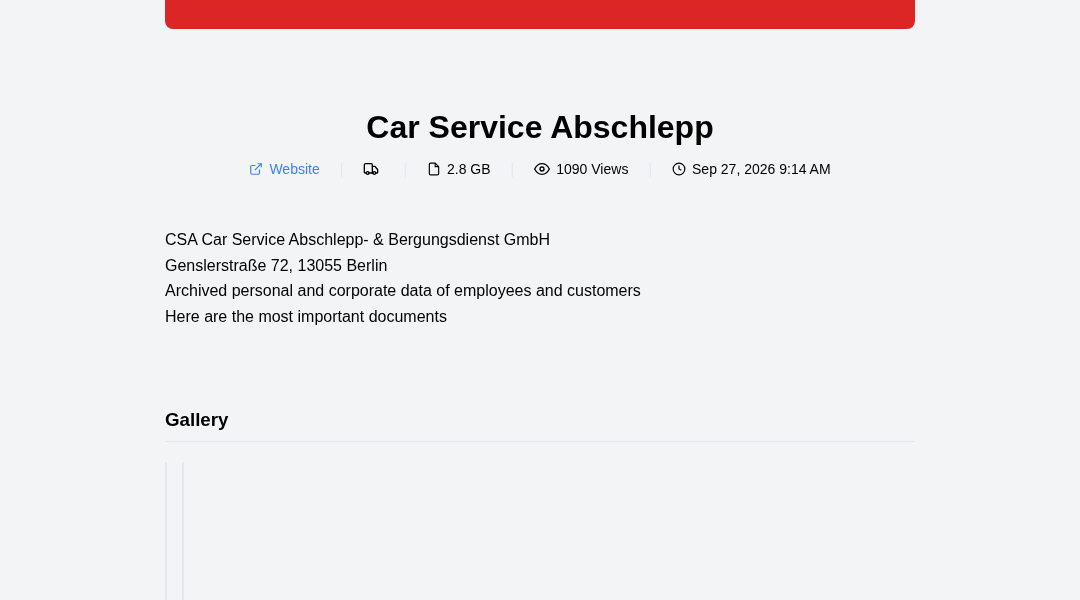
captured from the group's siteCSA Car Service Abschlepp- & Bergungsdienst GmbHGenslerstraße 72, 13055 BerlinArchived personal and corporate data of employees and customersHere are the most important documents
Data the group says was taken
- personal data
- corporate data
- employee data
- customer data
Screenshot of the leak post
Sources
Source
Indexed 22 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.