

Ransomware victim disclosure
← All victimsMinistério da Fazenda – Secretaria da Receita Federal do Brasil
listed as MINISTÉRIO DA FAZENDA SECRETARIA DA RECEITA FEDERAL DO BRASIL · Claimed by Emperador · listed 2 hours ago
Status timeline
- ListedSep 26, 2026
Current state: Listed for ransom
At a glance
- Group
- Emperador
- Status
- Listed for ransom
- Country
- Brazil
- Sector
- Government
- Listed on leak site
- Sep 26, 2026
- Data size
- 41 GB
- Records
- 17000 files
About the victim
AI dossier — public-source company profileThe Brazilian Federal Revenue Service (Receita Federal do Brasil) is the tax authority under the Ministry of Finance, responsible for tax collection, customs, and financial administration at the federal level. It operates across Brazil.
- Industry
- Government – Federal Revenue/Tax Administration
- Address
- Brasília, Brazil
Attack summary
Severity: critical — Confirmed exfiltration of government credentials, user authentication data (passwords), and PII at scale from a Brazilian federal tax authority. Exposure of gov.br system access and financial sector connectivity represents a threat to national infrastructure and public citizen data.The Emperador group claims to have exfiltrated several thousand documents containing personnel and customer data, as well as user data from gov.br systems including passwords. The group has not publicly disclosed a specific ransom demand for this victim.
Data the group says was taken
AI dossier — extracted from the leak post- Personnel records
- Customer data
- gov.br user accounts with passwords
- Government documents
What the group claims
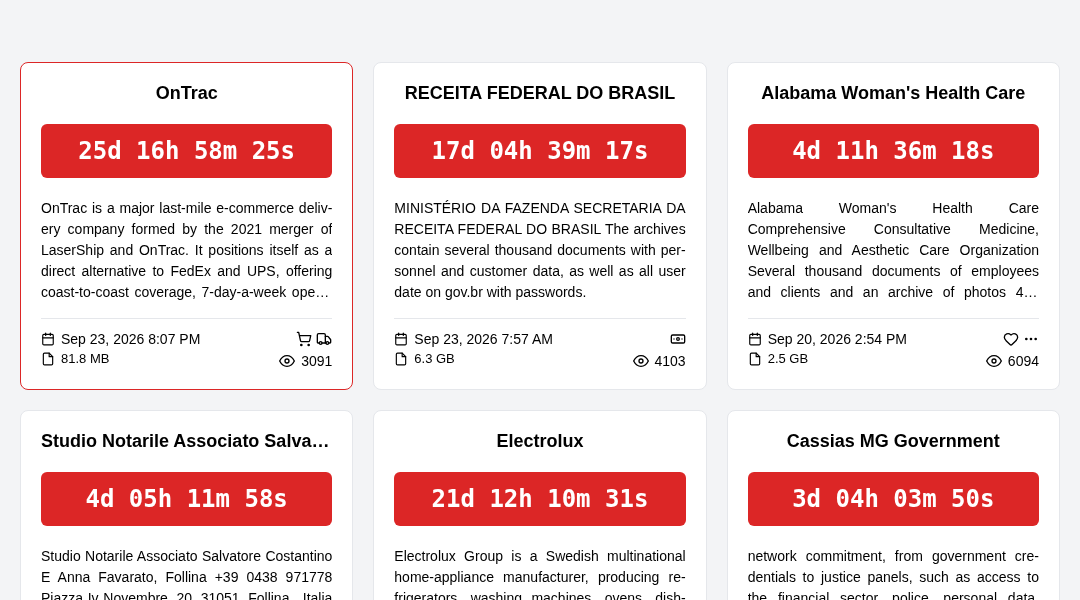
Brazilian Federal Revenue Service. Archives contain several thousand documents with personnel and customer data, as well as all user data on gov.br with passwords.
The leak post
captured from the group's site[ OnTrac is a major last-mile e-commerce delivery company formed by the 2021 merger of LaserShip and OnTrac. It positions itself as a direct alternative to FedEx and UPS, offering coast-to-coast coverage, 7-day-a-week operations, and competitive rates to reach over 75% of the U.S. population. We hold your full employee database, 197k records of employee PII: employeeNumber, xrefCode, firstName,middleName, lastName, loginId, employeeId, hireDate, originalHireDate, startDate, terminated, roles, legalEntity, legalEntityAddress, homePhone, mobilePhone, businessPhone, businessMobile, pager, personalFax, personalEmail, businessEmail, facebook, linkedin, addressPrimary1, addressPrimary2, addressMailing1, addressMailing2, userApproved, nativeAuth, culture & more. We demand an amount of $1M USD in XMR, otherwise your data WILL be publicly posted. Instructions will be emailed to you shortly. If you do not receive them, contact me on session, or email me. Session: 05651c7323273b723588d47455471ee9e27feb5187a30f2933554a705aacb38358 Email: [email protected], [email protected] (I prefer session.) If you do not cooperate, your partners and employees will be targeted, we will also se…
Data the group says was taken
- personnel data
- customer data
- gov.br user data
- passwords
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.