Ransomware victim disclosure

All victims

MINISTÉRIO DA FAZENDA - SECRETARIA DA RECEITA FEDERAL DO BRASIL

Claimed by Emperador · listed 2 hours ago

Today
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 24, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Country
Brazil
Listed on leak site
Sep 24, 2026

About the victim

AI dossier — public-source company profile

The Brazilian Federal Revenue Service (Secretaria da Receita Federal do Brasil), a department of the Ministry of Finance (Ministério da Fazenda), is responsible for federal tax collection, customs administration, and revenue enforcement across Brazil.

Industry
Government - Tax & Revenue Administration
Address
Brasília, Brazil

Attack summary

Severity: critical — Alleged exfiltration of PII at scale (personnel and customer data), government employee credentials, and passwords from a core Brazilian federal tax/revenue authority. This represents compromise of a critical government infrastructure entity with access to sensitive taxpayer and administrative information.

The group claims to have exfiltrated several thousand documents containing personnel and customer data, as well as user accounts and passwords from gov.br government systems.

critical

Data the group says was taken

AI dossier — extracted from the leak post
  • Personnel records
  • Customer data
  • Government employee accounts
  • Login credentials (passwords)
  • Gov.br system data

What the group claims

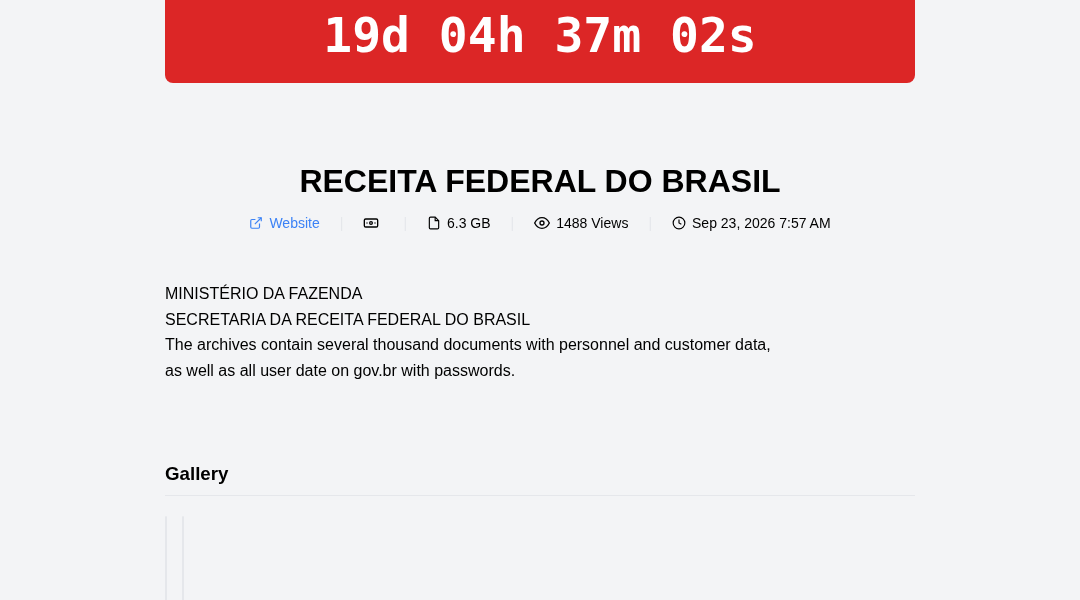
Archives contain several thousand documents with personnel and customer data, as well as all user data on gov.br with passwords.

The leak post

captured from the group's site
MINISTÉRIO DA FAZENDASECRETARIA DA RECEITA FEDERAL DO BRASILThe archives contain several thousand documents with personnel and customer data,as well as all user date on gov.br with passwords.

Data the group says was taken

  • personnel data
  • customer data
  • user credentials
  • passwords

Screenshot of the leak post

Leak screenshot for MINISTÉRIO DA FAZENDA - SECRETARIA DA RECEITA FEDERAL DO BRASIL

Sources

Source

Indexed 2 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About emperador

Emperador is a ransomware group first observed in August 2026 with an apparent financial motivation, though its limited operational history makes comprehensive attribution difficult at this time. Based on available data, the group has recorded at least one confirmed victim, with targeting concentrated in the Philippines and a demonstrated focus on the Government and Defense sector, suggesting either opportunistic targeting or a deliberate interest in sensitive public-sector data. Specific details regarding initial access vectors, encryption methodologies, and tooling have not been publicly documented by CISA, the FBI, Mandiant, or other reputable threat intelligence sources as of this profile's compilation, and no affiliation with known ransomware-as-a-service ecosystems or established threat actor clusters has been formally established. No notable high-profile campaigns, record ransom demands, or law enforcement actions have been publicly attributed to this group, which is consistent with its nascent operational timeline and minimal victim count. Given its very recent emergence and limited observed activity, Emperador should be considered an emerging and uncharacterized threat requiring continued monitoring, particularly by organizations operating within Philippine government and defense environments. The group has been linked to 44 public disclosures across our corpus. First observed on a leak site on August 12, 2026; most recent post September 24, 2026. The operation is currently active.

Timeline of this disclosure

  • September 24, 2026MINISTÉRIO DA FAZENDA - SECRETARIA DA RECEITA FEDERAL DO BRASIL listed by emperador on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the Government sector, which has 685 disclosures indexed across all operators we track. Geographically, MINISTÉRIO DA FAZENDA - SECRETARIA DA RECEITA FEDERAL DO BRASIL is reported in Brazil, a country with 209 ransomware disclosures in our corpus.

If your organisation is affected

A listing by emperador means MINISTÉRIO DA FAZENDA - SECRETARIA DA RECEITA FEDERAL DO BRASIL appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CERT.br (Brazil), as required for your jurisdiction.
  • Monitor for the data appearing on emperador's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.