

Ransomware victim disclosure

All victims

Unknown County/Government Agency (US)

Claimed by Rhysida · listed 2 hours ago

2.6 TB
Data size
814,500 files records
Today
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 21, 2026

Current state: Listed for ransom

At a glance

Group
Rhysida
Status
Listed for ransom
Listed on leak site
Sep 21, 2026
Data size
2.6 TB
Records
814,500 files

What the group claims

An unidentified US county or government entity with records including background checks, medical faxes, methadone clinic records, medical assistance files, county payroll, and jail gang-intelligence files.

The leak post

captured from the group's site
The Kreishandwerkerschaft Borken is the official trade association and advocacy organization representing local craft enterprises (Handwerksbetriebe) in the Borken district of Germany.1,382,523 files, 1.31 TBhealth data (disability lists with ID numbers, GdB medical ruling with diagnosis)sick leave, absence records, pension ruling2026 payslip (tax ID, social-security no., IBAN) and staff rostersigned contracts/terminations, CV with religionmember and creditor IBANsSCHUFA credit checks, court enforcement order, debtor affidavitMail and databases in full (Exchange, PST, SQL backups) + access/infrastructure slide (2FA secrets, S-FIRM code)
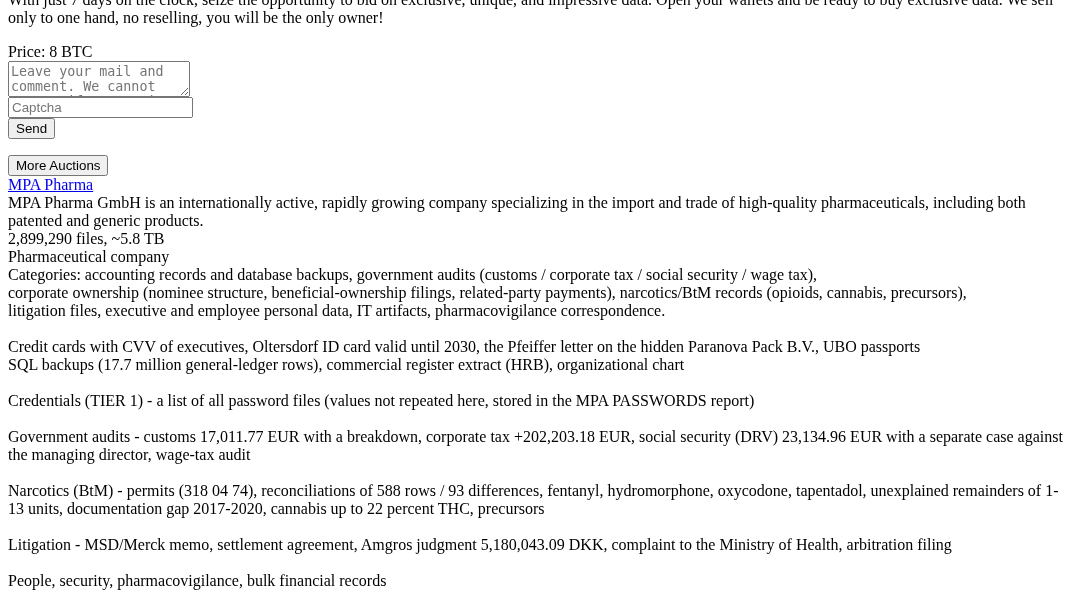
With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner!
MPA Pharma GmbH is an internationally active, rapidly growing company specializing in the import and trade of high-quality pharmaceuticals, including both patented and generic products. 2,899,290 files, ~5.8 TBPharmaceutical companyCategories: accounting records and database backups, government audits (customs / corporate tax / …

Data the group says was taken

  • background check dossiers
  • SSNs
  • medical faxes
  • patient names and diagnoses
  • methadone clinic records
  • medical assistance files
  • driver licenses
  • Green Cards
  • SSN cards
  • tax forms
  • bank data
  • county payroll registers
  • HR memos
  • contracts
  • pension databases
  • discipline databases
  • jail gang-intelligence files
  • gang-member master list

Screenshot of the leak post
Leak screenshot for Unknown County/Government Agency (US)

Sources

Source

Indexed 2 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Rhysida

Rhysida is a ransomware group that emerged in June 2023, operating with primarily financial motivations through targeted attacks against critical infrastructure and public sector organizations. The group's origin and potential state affiliations remain unclear, though they operate independently rather than as a traditional Ransomware-as-a-Service model, with limited public documentation regarding connections to other cybercriminal organizations. Rhysida employs double extortion tactics, typically gaining initial access through compromised VPN credentials and exploiting vulnerable public-facing applications before deploying their ransomware payload and exfiltrating sensitive data prior to encryption. The group has demonstrated a particular focus on healthcare and educational institutions, with notable attacks documented by CISA and FBI advisories highlighting their targeting of hospitals and school districts across multiple countries, resulting in significant operational disruptions to critical services. As of late 2024, Rhysida remains an active threat with continued operations targeting organizations primarily in the United States, Canada, and other Western nations, maintaining their focus on high-value sectors where operational disruption can maximize ransom payment likelihood. The group has been linked to 340 public disclosures across our corpus. First observed on a leak site on June 5, 2023; most recent post September 21, 2026. The operation is currently active.

Timeline of this disclosure

  • September 21, 2026Unknown County/Government Agency (US) listed by Rhysida on the group's public leak site
Data size
2.6 TB
Records
814,500 files

Sector and geography

This disclosure adds to ransomware activity in the Government / Public Health / Law Enforcement sector. Geographically, Unknown County/Government Agency (US) is reported in United States, a country with 3,167 ransomware disclosures in our corpus.

If your organisation is affected

A listing by Rhysida means Unknown County/Government Agency (US) appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CISA (United States), as required for your jurisdiction.
  • Monitor for the data appearing on Rhysida's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.