

Ransomware victim disclosure
← All victimsMomentum
Claimed by EndZone · listed 2 hours ago
Status timeline
- ListedSep 26, 2026
Current state: Negotiating
At a glance
- Group
- EndZone
- Status
- Negotiating
- Sector
- Telecommunications
- Listed on leak site
- Sep 26, 2026
- Records
- 7500000
About the victim
AI dossier — public-source company profileMomentum is a telecommunications company founded in 2001 that provides cloud-based communication solutions for businesses, including cloud voice services, managed networks, SD-WAN solutions, and Microsoft Teams Phone integration. The company operates a diagnostic and provisioning tool that manages internet and voice services for millions of users across global markets through multiple service operators (MSOs).
- Industry
- Telecommunications & Cloud Communications
- Founded
- 2001
Attack summary
Severity: critical — Confirmed exfiltration of PII at massive scale (7.5+ million users); demonstrated operational disruption to critical communications infrastructure affecting hundreds of thousands of customers; ongoing ransom negotiation with threat of public disclosure.EndZone claims to have compromised Momentum's diagnostic and provisioning tool via a Multi-Service Operator (MSO), gaining access to personally identifiable information for over 7.5 million users across all MSOs. The group states it has caused widespread operational disruption by deleting over 100,000 modem packages, cutting tens of thousands of customers from internet service, and threatens to publish exfiltrated data on October 5, 2026 unless the company negotiates.
Data the group says was taken
AI dossier — extracted from the leak post- PII for 7.5+ million users
- Customer names and contact information
- Billing account details
- Service configurations and modem MAC addresses
- MSO network configurations
The group's post references roughly 5 sample user records shown; operational disruption corroborated by referenced news article proof files.
What the group claims
Momentum is a telecommunications company founded in 2001 that provides cloud-based communication solutions for businesses, specializing in cloud voice services, managed networks, SD-WAN solutions, and Microsoft Teams Phone integration. Attackers gained access via a compromised Multi-Service Operator (MSO) diagnostic and provisioning tool, exposing PII for over 7.5 million users and causing widespread internet outages by deleting over 100,000 modem packages.
The leak post
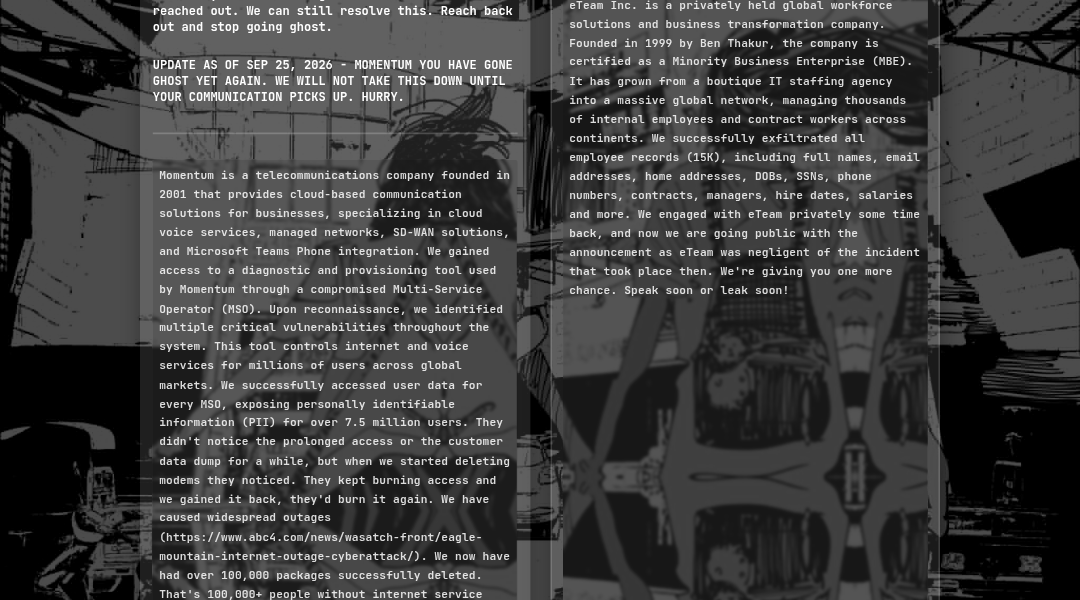
captured from the group's siteData will be public on: October 5, 2026 URGENT: Momentum we were very patient. Why ignore us when you know how big of a breach this is? YOU reached out. We can still resolve this. Reach back out and stop going ghost. UPDATE AS OF SEP 25, 2026 - MOMENTUM YOU HAVE GONE GHOST YET AGAIN. WE WILL NOT TAKE THIS DOWN UNTIL YOUR COMMUNICATION PICKS UP. HURRY. Momentum is a telecommunications company founded in 2001 that provides cloud-based communication solutions for businesses, specializing in cloud voice services, managed networks, SD-WAN solutions, and Microsoft Teams Phone integration. We gained access to a diagnostic and provisioning tool used by Momentum through a compromised Multi-Service Operator (MSO). Upon reconnaissance, we identified multiple critical vulnerabilities throughout the system. This tool controls internet and voice services for millions of users across global markets. We successfully accessed user data for every MSO, exposing personally identifiable information (PII) for over 7.5 million users. They didn't notice the prolonged access or the customer data dump for a while, but when we started deleting modems they noticed. They kept burning access and we gained it ba…
Data the group says was taken
- PII
- user data
- names
- addresses
- phone numbers
- email addresses
- billing information
- IP addresses
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.