

Ransomware victim disclosure

← All victims

Union FA (Union Financial Associates) / rogdianakis.gr

Claimed by Deadlock · listed 3 hours ago

Today
Age
since listed · listed for ransom

Status timeline

  1. ListedOct 3, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Country
Greece
Sector
Finance
Listed on leak site
Oct 3, 2026

About the victim

AI dossier — public-source company profile

Union Financial Associates (Union FA) is a Greek accounting and tax consulting firm based in Kallithea, Athens, headed by CEO Giorgos Rogdianakis. The company provides integrated accounting, tax, insurance, and financial services to businesses ranging from small enterprises to corporations, with emphasis on business oversight and advisory services.

Industry
Accounting, Tax & Business Consulting Services
Address
Λ. Ανδρέα Συγγρού 294, Καλλιθέα, ΤΚ 17673, Greece

Attack summary

Severity: medium — The leak post mentions Union FA among multiple victims but provides no specific proof files, data volume, or detailed inventory for this company. The lack of published proof or clear data specification prevents higher severity assessment, though exposure of accounting and tax consulting client data would carry moderate sensitivity.

The Deadlock group claims to have exfiltrated an unspecified volume of data from Union FA. The leak post does not detail the specific data types taken from this victim or provide clarity on the scope of compromise relative to this company alone.

medium

Data the group says was taken

AI dossier — extracted from the leak post
  • Client business records
  • Financial documentation
  • Tax records

What the group claims

A company providing accounting, tax and consulting services to businesses, owned by Giorgos Rogdianakis (CEO).

The leak post

captured from the group's site
Publishes after: <b>13d 4h 44m</b>
is a commercial construction company and general contractor headquartered in Placentia, California Founded in 2009, the company specializes in SCIF(Sensitive Compartmented Information Facilities) construction projects for high-security facilities, as well as tenant improvements in the aerospace and defense industry. Their well-known project partners and clients include Boeing, Jet Propulsion Laboratory (JPL), and Northrop Grumman 
Publishes after: <b>6d 4h 39m</b>
rogdianakis.gr leads to (or is directly related to) the company Union FA (Union Financial Associates) , which is owned by Giorgos Rogdianakis (CEO of the company). This is a company that provides accounting, tax and consulting services to businesses. 
Furniture Bargaining Council in South Africa. This is the tariff council for the furniture, mattress and upholstery industry.The platform serves employers and employees in the industry in regions such as Gauteng, North West, Mpumalanga, Limpopo and the Free State to handle legal and administrative processes. 
186,207 files (incl. 58,000+ scanned documents), structured as: 47,749 unique SA ID numbers 39,014 bank account records 10,498 salary…

Screenshot of the leak post
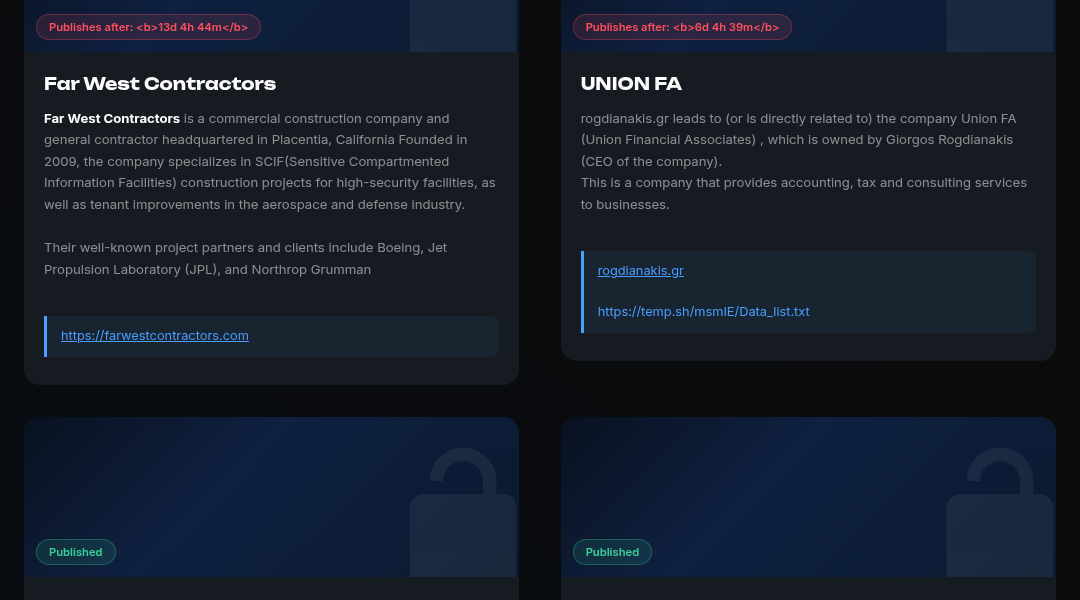
Leak screenshot for Union FA (Union Financial Associates) / rogdianakis.gr

Sources

Source

Indexed 3 hours ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About Deadlock

Deadlock is a ransomware group first observed in June 2026 with an apparent financial motivation, having claimed responsibility for attacks against at least 10 known victims across a geographically diverse target set. Given the recency of their emergence and limited public documentation by major threat intelligence organizations such as CISA, FBI, or Mandiant at this time, a comprehensive technical profile cannot be fully established. Based on available victimology data, the group has demonstrated a targeting pattern spanning Singapore, China, Sweden, Spain, and Nigeria, suggesting an opportunistic or globally distributed operational scope rather than a regionally focused campaign. Targeted sectors include manufacturing, business services, telecommunications, and financial services, indicating a preference for industries with high operational dependencies and potential for significant disruption, which is consistent with financially motivated ransomware actors seeking maximum leverage for ransom payment. No confirmed attribution regarding country of origin, RaaS affiliation, or specific tooling has been publicly documented by authoritative sources as of this profile's preparation. Due to the group's nascent operational timeline and the limited volume of publicly verified intelligence, analysts should treat this profile as preliminary and subject to significant revision as additional technical indicators, victim disclosures, and research reporting become available. Continued monitoring is advised given the cross-sector and cross-regional targeting behavior observed in this early operational phase. The group has been linked to 124 public disclosures across our corpus. First observed on a leak site on June 15, 2026; most recent post October 3, 2026. The operation is currently active.

Timeline of this disclosure

  • October 3, 2026Union FA (Union Financial Associates) / rogdianakis.gr listed by Deadlock on the group's public leak site

Sector and geography

This disclosure adds to ransomware activity in the Finance sector, which has 108 disclosures indexed across all operators we track. Geographically, Union FA (Union Financial Associates) / rogdianakis.gr is reported in Greece, a country with 3 ransomware disclosures in our corpus.

If your organisation is affected

A listing by Deadlock means Union FA (Union Financial Associates) / rogdianakis.gr appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Monitor for the data appearing on Deadlock's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.