

Ransomware victim disclosure
← All victimsLegis
Claimed by Rhysida · listed 2 hours ago
Status timeline
- ListedSep 24, 2026
Current state: Listed for ransom
At a glance
About the victim
AI dossier — public-source company profileLegis is a Latin American publisher specializing in legal and business information resources serving professionals across six countries: Colombia, Venezuela, Argentina, Mexico, Peru, and Chile. Founded over 60 years ago, the company provides databases and information to law firms, universities, government contractors, and major corporations.
- Industry
- Legal Publishing & Information Services
- Founded
- 1960
Attack summary
Severity: critical — Confirmed exfiltration of regulated personal data at scale (ID copies, claimant PII in constitutional records), financial records, government contract information, shareholder registers with identification documents, and litigation files. Exposure affects a publishing company serving six countries with access to sensitive legal and business intelligence across the region.Rhysida claims to have exfiltrated comprehensive databases from Legis including SQL databases, email archives, legal documents, financial records, customer lists, and shareholder information. The group claims access to constitutional litigation records with personal data, ID copies, financial reports, customer databases including major firms like Ecopetrol and Halliburton, and ownership structure details.
Data the group says was taken
AI dossier — extracted from the leak post- SQL databases
- Email archives (PST/OST)
- Legal documents and litigation records
- Shareholder and beneficial-owner register with ID copies
- Financial and tax reporting
- Customer databases (law firms, universities, government agencies)
- Tax IDs and corporate contacts
- Contract matrices and payment agreements
- Constitutional action records (Tutela) with claimant personal data
- ID card copies (cédulas)
- Sanction and dispute proceedings
What the group claims
Well-known Latin American publisher that creates specialized legal and business information resources. Founded over 60 years ago, serves professionals across six countries including Colombia, Venezuela, Argentina, Mexico, Peru, and Chile.
The leak post
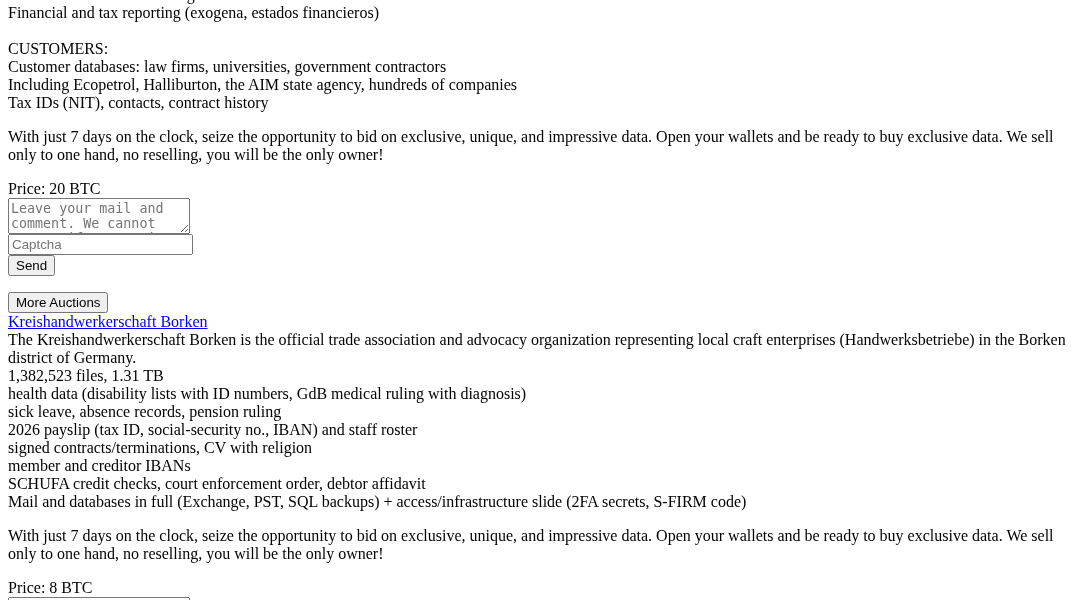
captured from the group's siteLegis is a well-known Latin American publisher that creates specialized legal and business information resources. Founded over 60 years ago, the company serves professionals across six countries including Colombia, Venezuela, Argentina, Mexico, Peru, and Chile.DATABASES (SQL)PST/OSTLEGAL DOCUMENTS:Tutela - constitutional actions with claimants' personal dataID card copies (cedulas) of shareholders and third partiesEnvironmental sanction proceedings against the company (AUTO 10852)Sanction dispute with the pension authority (UGPP)Signed cease & desist - trademark dispute (Xpandia case)Personal data transfer agreements (Colsubsidio, Universidad Externado)Litigation log of all company lawsuitsContract matrix, payment agreements, reorganization documentsFINANCE & OWNERSHIP:Shareholder and ultimate-beneficial-owner register with ID copiesOwnership structure: ~99.94% held by a single ownerDividend payment recordsDebt write-off letters naming debtors and amountsFinancial and tax reporting (exogena, estados financieros)CUSTOMERS:Customer databases: law firms, universities, government contractorsIncluding Ecopetrol, Halliburton, the AIM state agency, hundreds of companiesTax IDs (NIT), cont…
Data the group says was taken
- SQL databases
- PST/OST files
- legal documents
- constitutional action records
- ID card copies
- environmental sanction proceedings
- litigation logs
- contract documents
- shareholder/UBO register
- financial records
- tax records
- customer databases
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.