

Ransomware victim disclosure
← All victimsUnknown Pharmaceutical Manufacturer
Claimed by N0n · listed 5 hours ago
Status timeline
- ListedOct 6, 2026
Current state: Listed for ransom
At a glance
About the victim
AI dossier — public-source company profileA pharmaceutical manufacturer operating three sites in Türkiye, subject to GxP (Good manufacturing Practice) regulatory requirements. The company manufactures regulated pharmaceutical products across a distributed multi-site operational footprint.
- Industry
- Pharmaceutical Manufacturing (GxP)
Attack summary
Severity: critical — Exfiltration of complete network-security configurations, remote-access mappings, and 1.35M connection records from a GxP-regulated pharmaceutical manufacturer creates immediate operational and security risk. GxP environments handle regulated drug manufacturing; disclosure of security infrastructure and credentials enables follow-on attacks and regulatory non-compliance. Total network blackout across three sites indicates operational disruption to drug production.The N0n group claims to have encrypted all three sites' networks and exfiltrated complete internal network-security configurations and connection records from M365/Intune, SAP Concur, UniFi camera systems, and internal applications. The group states all sites are under total network blackout and that backups and shadow copies have been destroyed.
Data the group says was taken
AI dossier — extracted from the leak post- network security configurations (all 3 sites)
- M365/Intune connection records
- SAP Concur records
- UniFi camera system data
- internal application data
- remote-access mappings
What the group claims
Pharmaceutical manufacturing company operating 3 sites under GxP standards
The leak post
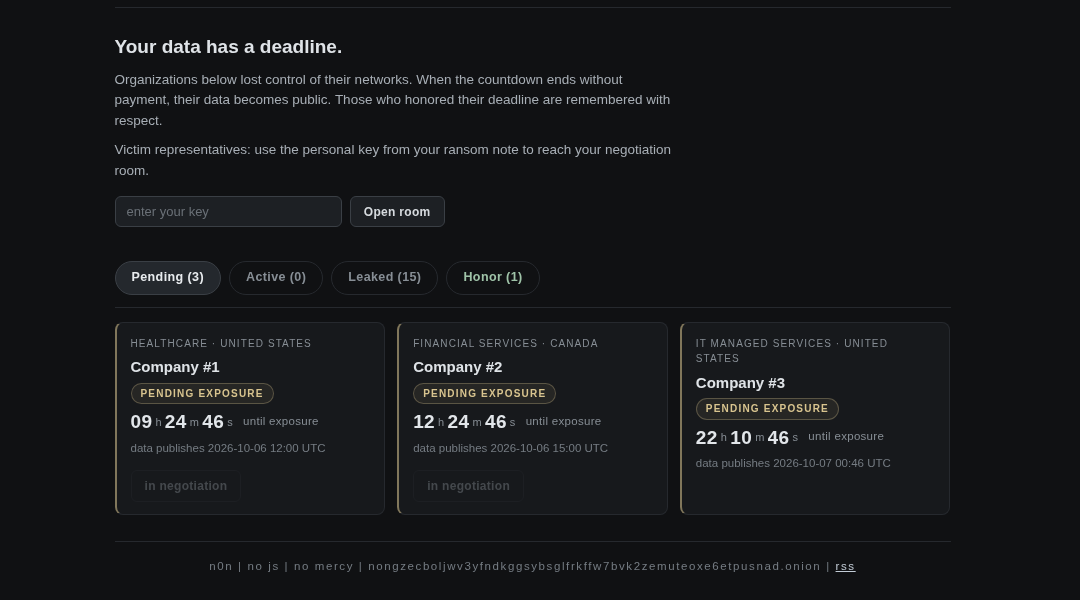
captured from the group's site# Your data has a deadline. Organizations below lost control of their networks. When the countdown ends without payment, their data becomes public. Those who honored their deadline are remembered with respect. Victim representatives: use the personal key from your ransom note to reach your negotiation room. ### FinSoft (Kolibri retail back-office software) Retail software vendor / IT services · Uzbekistan #### What will be published if no settlement is reached * Everything: client databases of 10+ retail chains (keddo, marc, lancaster, comf_rus and others), the back-office platform and API service data Their business operations are fully stopped. Nothing restores operations without settlement — all backups and shadow copies are encrypted or destroyed. ### AFRICA-TECH (IT services / document processing) IT services / document services · Mali #### What will be published if no settlement is reached * Client documents: scans, attestations, insurance and embassy files, shared business folders Operations are fully stopped. Nothing restores without settlement — all backups and shadow copies are encrypted or destroyed. ### Fanatics (global sports commerce platform) Sports commerce …
Data the group says was taken
- network-security configuration
- device definitions
- remote-access mappings
- connection records
- M365/Intune data
- SAP Concur data
- UniFi camera estate data
Screenshot of the leak post
Sources
Source
Indexed 5 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.